How to Conduct a Risk Assessment That Actually Improves Compliance
Introduction: Moving Beyond Checkbox Compliance
For many organizations, risk assessments are still treated as a routine task something to complete before an audit and then forget But in 2026, that approach creates more risk than it reduces. Cyber threats evolve constantly, and compliance frameworks now expect businesses to demonstrate continuous awareness, not periodic effort
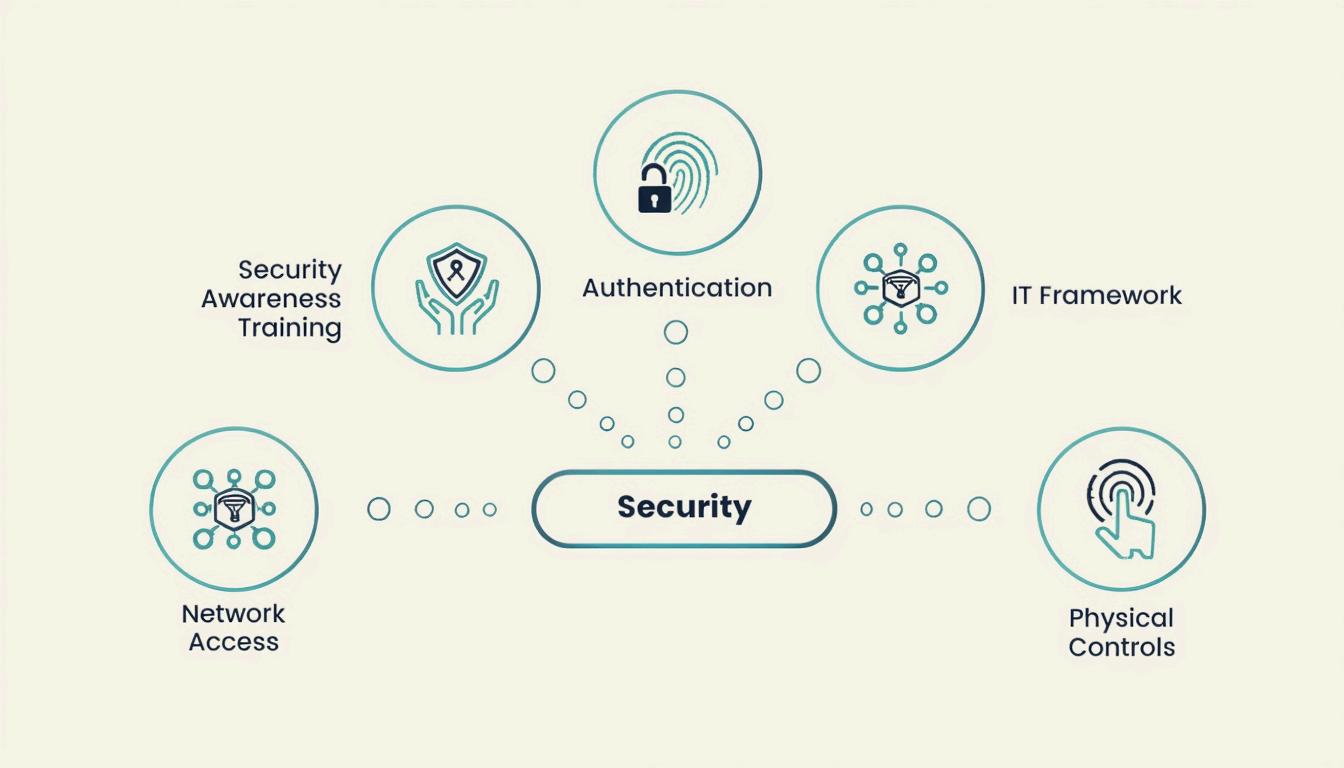
A modern risk assessment should do more than identify gaps It should actively strengthen your compliance posture, guide decision-making, and reduce real-world exposure. Organizations achieving this are increasingly relying on structured processes and cybersecurity compliance solutions to connect risk insights directly with regulatory requirements. When done right, risk assessment becomes a strategic advantage not just an obligation.
Risk assessment today is no longer just about listing threats and vulnerabilities It is about understanding how those risks impact your ability to meet compliance standards such as NIST 800-171, CMMC, SOC 2, or ISO 27001
The Shift from Static to Continuous Risk Evaluation
Traditional assessments were conducted annually or quarterly In 2026, that model is outdated Threats evolve too quickly, and businesses are expected to maintain a real-time understanding of their risk landscape.
Continuous risk evaluation means your organization is always aware of new vulnerabilities, system changes, and emerging threats. This directly improves compliance because controls remain aligned with current risks rather than outdated assumptions
Why Compliance Depends on Risk Context
Compliance frameworks are not random checklists; they are built to address real risks However, many organizations fail audits not because they lack controls, but because their controls are not aligned with their actual risk exposure. A risk-based approach ensures that every control you implement has a clear purpose tied to both security and compliance outcomes
Infrequent Updates
An assessment that is not updated regularly quickly becomes irrelevant In a fast-changing threat landscape, outdated risk data leads to ineffective compliance strategies.
Building a Risk Assessment That Drives Real Compliance
To make risk assessment truly effective, organizations need a structured, practical approach that connects risk identification directly to compliance action.
Identifying Critical Assets and Data
Every risk assessment should begin with clarity about what needs to be protected.
Mapping Your Data Environment
This includes identifying where sensitive data is stored, how it flows through systems, and who has access to it In 2026, data mapping is a core expectation in most compliance frameworks
Without this visibility, risk assessment becomes incomplete and unreliable
Understanding Asset Criticality
Not all systems carry the same level of importance. A customer database, for example, presents a far higher compliance risk than an internal communication tool. Prioritizing assets ensures that your efforts are focused where they matter most
Identifying Relevant Threats
Once assets are defined, the next step is understanding the threats that could impact them
Modern Threat Landscape in 2026
Threats today include AI-driven phishing, ransomware-as-a-service, credential stuffing, and supply chain attacks. These are not theoretical, they are actively targeting SMBs and mid-sized organizations Understanding which threats are most relevant to your business helps eliminate unnecessary noise and keeps the assessment focused
Using
Threat Intelligence
Incorporating real-world threat data allows organizations to align their risk models with current attack patterns. This improves both accuracy and relevance.
Evaluating Vulnerabilities with Context
Identifying vulnerabilities is not enough The key is understanding how they can be exploited in your specific environment.
Technical vs Contextual Risk
A vulnerability may appear minor in isolation but become critical when connected to sensitive data or privileged access
For example, an outdated system may not seem urgent until it becomes an entry point to financial records or customer information
Access and Exposure Analysis
Understanding who can access a system and how that access is controlled is essential Weak access controls often amplify the impact of vulnerabilities
Prioritizing Risks Effectively
Not all risks should be treated equally Prioritization is what turns a risk assessment into a practical tool.
Likelihood and Impact Modeling
Each risk should be evaluated based on how likely it is to occur and the damage it could cause. This allows organizations to focus on high-impact, high-probability risks first
Dynamic Risk Scoring
In 2026, many organizations are moving toward dynamic scoring models that adjust based on real-time data. This ensures that priorities remain aligned with the current threat landscape.
Aligning Risk Assessment with Compliance Frameworks
A strong risk assessment directly supports compliance by linking risks to specific controls
Mapping Risks to Controls
Every identified risk should correspond to one or more compliance controls For example, if credential theft is a major risk, implementing multi-factor authentication directly addresses both security and compliance requirements.
Creating Audit-Ready Documentation
Auditors expect clear evidence of how risks are identified and mitigated.
Maintaining Clear Records
This includes documenting risk evaluations, control implementations, and ongoing monitoring efforts
Demonstrating Continuous Improvement
Compliance is no longer about a single point in time Organizations must show that they are actively managing and reducing risk over time.
Moving Toward Continuous Risk Assessment
One of the most important shifts in 2026 is the move from periodic assessments to continuous monitoring.
Real-Time Visibility
Organizations need the ability to detect changes in their environment as they happen. This includes new vulnerabilities, unusual user behavior, and system updates
Automation and Integration
Automation reduces the burden on internal teams while improving accuracy. Integrated systems ensure that risk data, compliance requirements, and security controls are always aligned
This approach not only improves security but also makes compliance easier to maintain throughout the year
Common Mistakes to Avoid
Even well-designed risk assessments can fail if certain pitfalls are not addressed.
Overcomplicating the Process
Trying to evaluate every possible risk often leads to confusion and inefficiency. Focus on what truly matters
Treating Compliance as the End Goal
Compliance should be the result of strong security practices not the primary objective
Ignoring Cross-Functional Input
Risk assessment should involve multiple departments, not just IT Business context is essential for accurate evaluation.
Failing to Update Regularly
An outdated assessment is as risky as having none at all. Regular updates are critical.