
Inthispaperwepresentanintrusiondetectionsystemthat usestriangular membership functiontodetectthe type of intrusioninthenetwork.
A computer network contains a set of hardware and softwarecomponentsinordertoestablishawidenetwork. Both hardware and software components have their own risks,vulnerabilitiesandsecurityproblems. Thesoftware makesthedatainopenenvironmentofcomputernetwork veryvulnerabledueto theattack.Computernetworksare beingattackedeverydayandthereforetheyareunreliable and unsafe, which means that the users may experience maliciousactivitiesandmaylosetheirprivacy,personaldata oranyotherimportantinformationthatisavailableon line, dependingonthenatureofattacks.Toprotectthesystem fromalltheinternalandexternalmaliciousattacksweuse various network security .The external attacks by the intruders can be detected by IDS(Intrusion Detection System).Networkintrusiondetectionsystem(NIDS)isused for detection of attacks in computer networks. NIDS is installed on server side to monitor the incoming and outgoingtrafficfordetectionofintrusion.Theobjectiveof IDS to give a mass protection to stand up to the attack of computersystemininternet.Theintrusiondetectionsystem worksonthecollectedinformation
1.INTRODUCTION
Intrusioninacomputernetworkisagroup ofactivitiesthat degrade,disrupt,denyordestroyinformationandserviceson thecomputernetwork.Intrudersareexecutedthroughdata whichflowthroughthecomputernetworksandmaydisturb theintegrity,confidentiality,oravailabilityofthecomputer networks. Examples of intruders are viruses attached to email,internetworm,unauthorizedusagesofsystem,denial of services, probing of the system to collect information. Intruders are often called hackers and there are three different classes of intruders’ masquerades, social engineeringintrudersandabuseoffunctionalityintruders. First,themasquerades,preventindividualsfromusingtheir computersystemsandthenpenetratethecomputersystems entrybyutilizingcredentialsoftheindividuals.Second,the social engineering intruders, in which unauthorized user obtaintheinternalinformationofthecomputersystemsto get access to a required computer system. Third, abuse of functionalityintruders,inwhichattackerperformunwanted activity for a computer system failure by overdoing a legitimateaction. Intrusion detection system (IDS) is an equipment for checking,
1.1 Intrusion Detection System
International Research Journal of Engineering and Technology (IRJET) e ISSN: 2395 0056 Volume: 09 Issue: 01 | Jan 2022 www.irjet.net p ISSN: 2395 0072 © 2022, IRJET | Impact Factor value: 7.529 | ISO 9001:2008 Certified Journal | Page932 Detecting Various Intrusion Attacks using A Fuzzy Triangular Membership Function Richa Mishra1, Sakshi Koli2 , Shubham Gupta3 1Mrs. Richa Mishra, Assistant Professor, Dept. of CSE 2Ms Sakshi Koli, Assistant Professor, Dept. of CSE 3Mr. Shubham Gupta, Assistant Professor, Dept. of CSE Tula’s Institute Dehradun *** Abstract - In recent years, the area of intrusion detection has received a lot of consideration. One factor is the internet's exponential growthandthevastnumberofnetworkedsystems found in various organizations. As a result of this growth, the number of cyber attacksagainstthesedevicesandservices has increased as well.. Each sort of attack has distinct characteristics that can be identified and prevented using supervised learning techniques. Many advances have been made thanks to the efforts of various academics who are actively researching on various techniques to improve ID performance. However, advancements in a number of other processes and technologies continuously present new opportunities to add a sharp edge to IDS and to make it more reliable and robust. In this paper we make to detect various attacks by using fuzzy and of triangular membership function and to normalize huge data standard deviation is used. This template, modified in MS Word 2007 and saved as a “Word97 2003 Document ( Size 10 & Italic , cambria font)
Key Words: , Supervised Learning , Fuzzy Logic ,Triangular Membership Function
networksystemfrombasedcollectcredentimaytrafficTheactivityincidents.distinguishingandbreakingdowntheinfringementTheIDSmonitorsnetworktrafficfordistrustfulandcansendalarmstothenetworkadministrators.IDSmayrespondtomaliciousalsocalledabnormalbytakingappropriateactions.TheappropriateactionsbetakensuchasblockingthesourceIPaddressoruseralinformationfromaccessingthenetworkIDScandatafromahostbasedsystemorfromanetworksystem.Inthehostbasedsystemdataarecollectedsystemlogfilesandauditlogfiles.Inthenetworkbaseddataarecollectedandanalyzedbyanalyzingthepackets

TheNIDScollectsdataandmanipulatesthecollecteddata for better analysis wherein the HIDS collects data from systemlogfilesandauditlogfilesforevaluation.
1Supervised learning: In supervised learning labelled datasetsareused.Trainingisdoneunderthesupervisionof ateacher.Thelabelledtrainingdatasetsareusedintraining phase. There are different types of supervised learning
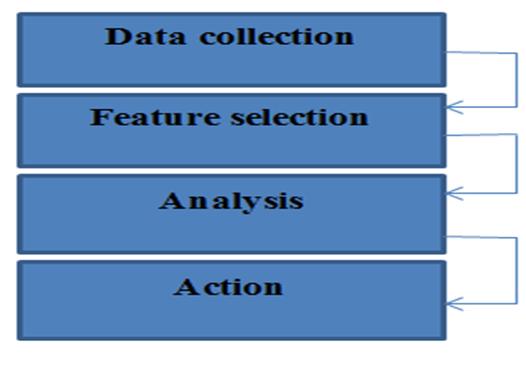
1.Datacollection:TheDatacollectionsection,collectsdata fortheIDS.Thedataarecollectedfromdifferentsourcesand arestoredinfilesandthenanalysed
2.Featureselection:Infeatureselectionmodule,a specific attribute is selected for the IDS. The specific attribute decreases the computational time and increases the performance.The featureselectionisperformedbasedon internet protocol (IP) addresses of the source and target systems., Types of protocols, header length and size of packetsareconsideredasmainfieldstodetectanintrusion.
AnIDShasfourmainfunctionsi.e.,DataCollection,Feature Selection,AnalysisandAction.(asshowninfig2).
3.Analysis:Thecollecteddataareanalyzedinthisfunction. This module plays important role in intrusion detection. TherearetwokeywaysforIntrusionDetection RuleBased and Anomaly Based. The Rule Based technique work on information collected from real time environment. In anomalybaseddetection,datamatchingisperformedwitha normalprofiledatatocheckthedeviations.Anintrusionis consideredwhenanydeviationisfoundinthematch.
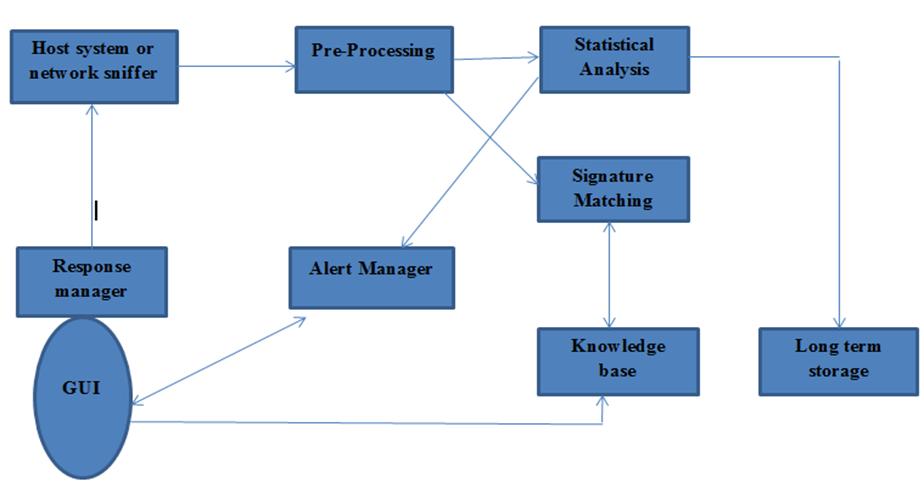
Figure1.1showsthedetailworkingofanintrusiondetection system.Inthisdataarecollectedfromhostornetwork.After collection and pre processing of data is performed, the collected data are matched with the defined signature. If attacksaredetected,itwillgenerateanalerttothesystem.If collecteddatadoes notmatchtotheexistingsignaturethenit willbedefined asanormaltraffic.
Fig1.2(FunctionofIDS)
4. Action: In this section attack detections and alert generationsarethemaintasks.Thenetworkadministrator willgenerateanalarmoritwilldropanemailmessageinthe eventofanyattack.
(Hostbasedintrusiondetectionsystem)
1.Hostbasedintrusiondetectionsystem(HIDS)isinstalled on a single system. The HIDS detects intrusion in local environmentandanalyzesthehostsystem.Asensorwhich can be installed on the host system can obtain data from system log files. The system log files are generated from operatingsystem(OS) installedonthehostsystem.TheHIDS doesnotappearintheOSauditloggingmechanism.TheHIDS dependsonaudittrailsandareeasytoinstallandmaintain. theaudittrailsverifysuccessorfailureoftheattacksonthe hostsystem.
International Research Journal of Engineering and Technology (IRJET) e ISSN: 2395 0056 Volume: 09 Issue: 01 | Jan 2022 www.irjet.net p ISSN: 2395 0072 © 2022, IRJET | Impact Factor value: 7.529 | ISO 9001:2008 Certified Journal | Page933
1.2 Function of IDS :
2.NIDS(Networkbasedintrusiondetectionsystem)
1.3 Intrusion Detection techniques: Todaycomputernetworksareincreasingrapidly.That’swhy security is a measure concern in the computer networks. Thesetechniquesaredifferentfromtheirworkingmethod andwayofimplementation.Thesetechniquesarebeingused to detect intrusion in the computer networks. Network attacks prevention can be done only when a reliable intrusiondetectionsystemisused.Broadly,therearethree techniques for intrusion detection: Supervised learning, Unsupervisedlearning,andReinforcementLearning.
TherearetwotypesofIDSbasedondeploymentoftheIDSas following:1.HIDS
Figure1.1StandardIDS
2.Networkbasedintrusiondetectionsystem(NIDS)collects data fromcomputernetworks.TheNIDSconductsauditof attacksonthecomputernetworksbywatchingthepackets across the computer network . In NIDS audit, sensors are deployedonthenetworkedsystemsandarewellarmedwith ruleswhichareformedbysignaturebased observations.to examinenetworkpacketheaders.NIDSiseasyandcheapto implementand monitorsattacks like DoS attacksand root attacks.
Cristiani etal.proposed FROST(AnIDSbasedonthefuzzy setstheory)toidentifyvarious kindsofcyber attacksonIoT networks. Main concept of FROST was to suggestively decreasedthenumberofoccurrencesrelatedtoanewtypeof attackclassifiedasoneoftheidentifiedattacks.Duetothe attackclassification,alowererrorrateisshown. Saidi, F et al. introduced a Fuzzy IDS as a Service which consider fuzzyrulesbaseandtheMamdanimethodtogather the rules. It enabled network administrators and cyber securityspecialiststofollow therealtimethenetworktraffic behaviour. Network traffic behaviour includes the Port ScanningCriticalityLevel(PSCL). ASaaSdynamicdashboard is used to swiftly and efficiently recognize spiteful port systemsthescanningactivity.ExperimentsandassessmentsrevealedthatsuggestedsystemoutperformedSnortandrelatedIDSinmultilevelportscanningdetection.
d)DataMining e)Fuzzy 1.SupportLogic.VectorMachinedoesnotworkonlargevolume ofdatasetandtakesmorecomputational time.Because of highcomplexitymorememoryisrequired.
3Reinforcementlearning:Reinforcementlearningisacritic basedlearning.Inthislearningalgorithm,outsidefeedback isrequired.Inthislearningcomputercaninteractwiththe environment for learning. A user can label the datasets in reinforcementlearning
Ding et al. Proposed optimization based cluster analysis approachwithfeatureselectionwithafuzzyandrealcoded chemical reaction for the intrusion detection system. The results showed that FMIFS RCCRO FCM outperforms the othermethodsintermsofbothefficiencyandaccuracy.With the help of FMIFS approach with RCCRO FCM model processing of a large number of features can be avoided Seasily.Douzi, S et al. proposed a combined algorithm based on featureselectiontechniquessuchasWeightedFuzzyC Mean Clustering Algorithm (WFCM) and Fuzzy logic. The methodologyreducedtheinputdataandintroducedweights intoeachofthedatadimension.Thismainfocusofthisarticle wastolowerthefalsealarmrateswhichareveryproblematic for IDS, and ensure the flexibility of intrusion detection systemsinanenvironmentwithinaccuracyanduncertainty.
2. Hierarchal k map does not work on KDD dataset, becauseitdoesnotworkonmorethan5variables.
1.4 Classification in IDS : Varioustypesofclassifiersareusedforintrusiondetection, whichare:
algorithms.BayesianStatistics,ANN,Lazylearning,Gaussian Process Regression, Nearest Neighbor algorithm, Support VectorMachine,HiddenMarkovModel,BayesianNetworks, Decision Trees, Perceptron, SVM and classifiers aresomeofthemostpopularsupervisedlearningalgorithms
There are various important clustering algorithms for unsupervised learning like Cluster analysis (K means clustering,Fuzzyclustering),Hierarchicalclustering,Outlier detection (Local outlier factor), Self Organizing Map, Apriorityalgorithm,Éclatalgorithm.
a)SupportVectorMachine b)HierarchicalK Map c)NeuralNetwork
Quadratic
International Research Journal of Engineering and Technology (IRJET) e ISSN: 2395 0056 Volume: 09 Issue: 01 | Jan 2022 www.irjet.net p ISSN: 2395 0072 © 2022, IRJET | Impact Factor value: 7.529 | ISO 9001:2008 Certified Journal | Page934
2. LITERATURE REVIEW
3.Neuralnetworkrequiremorecomputationalresources. Laterdataadditionintrainingnetworkisdifficultinneural network.4.Data mining provide facility to perform operation on large dataset, but have some issues of security, privacy. Fuzzylogicprovidesmoreaccuratedetectionrateasequated to support vector machine, neural network, data mining. Fuzzy logic does not have fine tuned classifier, not have selected features for reduced computational time and improveddetectionrate.Entropybasedfeaturesselection andlayeredclassifierusingfuzzycontrolledlogicisusedto overcomethislimitation.Itwilldecreasethefalsepositive rateofdetectionofattacks,andreducesthecomputational time.
2Unsupervisedlearning:Whenlearningisdonewithoutany guidancethenitiscalledunsupervisedlearning.Clusteringis basicallyanunsupervisedlearning.Forexample,afishkid does not know swimming, with her mother they learn swimming by their own. This is unsupervised learning. In this, unlabelled datasets are used as training datasets. Outsidefeedbackisnotrequiredinunsupervisedlearning.
1.5 KDD Dataset in IDS KDD dataset is used as a training dataset. For testing dataset,dataarecollectedfromWireshark. KDD dataset can be used as training dataset. It is very populardatasetforintrusiondetection.KDDdatasetcontain millions of records where each record comprises 41 attributes.Someattributehave moreinfluenceonattacks detection,andsomehavelessinfluenceonattackdetection.
Thereareseveralmethodsusedforattributeselection.For attributeselectionFeedforwardneuralnetworkcanbeused andit requiresextensivetraining. Support vector method can also be used for attribute selection. Genetic algorithm is used as attribute selection method as well for reduction of dimensionality. All these selection method does not simultaneously provide the minimumandmaximumvalueswhichareinwithinrange. Entropy based attribute selection method is used for attribute selection. This method uses minimum and maximumvalueforattributeselection. Fuzzy logic provides base to handle imprecision and vagueness as well as mature influence mechanisms using changingdegreeoftruth.InFuzzylogic boundariesarenot alwaysevidentlyclear.Fuzzylogicincludethe identification of complexpatternorbehaviourvariations.Fuzzylogicuses the membership degree to determine the strength of an objectbelongstodifferentclass.
Haiderxal. proposedNGIDS DSwhichhasamedium high qualityofrealismandisgeneratedbytheintelligentuseof thecommercial scalesecuritytesthardwareplatformIXIA Perfect Storm. The NGIDS DS comprised labeled network and host logs. It reflects the current critical cyber infrastructures. It included both normal and abnormal scenarios where abnormal scenario adds accurate attack ofbehaviorsandnormalscenariosaddsnormaltrafficdynamicsrealworldnetworks.
1. Methodsofattributeselection.
Shanmugavadivu,R etal developedanintrusiondetection systembasedon anomalyto detectan intrusionbehaviour over a network. It designed a fuzzy decision making to structurethesystemmoreaccurateforattackdetectionby usingthefuzzyinferenceapproach.Italso usedautomated strategy for generation of fuzzy rules, which are obtained from the definite rules using frequent items. The experimental results clearly showed that the proposed systemaccomplishedhigherprecisioninidentifyingwhether therecordsarenormalorattackone.
International Research Journal of Engineering and Technology (IRJET) e ISSN: 2395 0056 Volume: 09 Issue: 01 | Jan 2022 www.irjet.net p ISSN: 2395 0072 © 2022, IRJET | Impact Factor value: 7.529 | ISO 9001:2008 Certified Journal | Page935
3. METHODOLOGY
Imen Gaied,Farah et al. demonstrated that their approach based on NEFCLASS model is morepowerful in classifying intrusionsthantheonebasedonANFISmodel.Theproposed model istheNeuro Fuzzy model accurately the NEFCLASS (Neuro Fluffy Classification) model of a generic fuzzy perceptronwhichisintheformofagroupingofneuronand fuzzysystemnetworks.
In the process of attack detection, the fuzzy controlled languageisused.Thelayeredmodelisusefulforclassifying themainclassesofattacksandthesubclassesofattacks.A fuzzycontrolledarchitecturedescribeshowtheprocessof attack detection takes place. Fig 3.1 shows the fuzzy controlledarchitecture.Itcontainsthefollowingstepswhich havebeentakenintheprocess.
2. LayeredFuzzycontrollanguage.
datasetFig3.1(FunctionBlock )
Sukumaretal developedanintrusiondetectionsystemthat usesIGKMalgorithmtodetectthetypeofintrusionandthe numberofclusters(k)isnotfixedbeforehand.Itincludedthe k means++setofrulesandanintrusiondetectionsystemthat used IGKM algorithm whilst using smaller subset of KDD . KDDdatasetcontained ninetyninedatasetwiththousand instances.TheShownexperimentresultindicated thatthe intrusiondetection withIGKMalgorithmwasmoreaccurate comparedtok means++algorithm.
creationMachinetechniqueshowedSincefoundandhigherValliaevolvingDistributedIntrusionDetectionSystem(DIDS)thatcombinedandpromisingtechnologiessuchasBlockchainwithsolidfoundationsuchascloudinfrastructureKumariVetal.proposedahybridmechanism.ItshowsprocessingspeedcomparedtomulticlassificationrequireslesstrainingtimecomparedtofullSVM,italsooutlowLabellingcostasinsteadoffullylabelledSVM.smallamountoflabelledsetwasused.ThispaperahybridsemisupervisedmachinelearningthatincludesActivelearningSupportVector(ASVM)andFuzzyCMeans(FCM)clusteringintheofaneffectiveIDS.
Kumari,Vetal proposeda.hybridsemi supervisedmachine learning technique that uses Active learning Support to perceiveattacksinthenetwork.ItincludedVectorMachine (ASVM)andFuzzyC Means(FCM)clusteringinthedesignof anefficientIDS.SetofrulesisexaminedonNSLKDDbench markIDSdatasetandwasinitiatedtobepromising.
3. Testing
Kumar et al. presented the architecture of the Distributed Intrusion Detection System using Cloud Computing Infrastructure andBlockchain. The strategy was builtona
1Methodsofattributeselection: KDDcupdatasetsareused forstudyofmainclassesofattacksandtheirsubattacks.The datasetscontain41attributes,inwhich7arediscreteand34
Balan et al proposed a system that detects the spiteful behaviourofnodebyintrusiondetectionsystemwithfuzzy logictechniqueandalsotocategorizethetypeofattacks.The system is strong enough to detect attacks including black hollowattackandgreyhollowattackandadditionallyableto averttheonestypeofattacksbyusingefficientnodeblocking mechanismsuchthattheproposedsystemprovidesasecure communicationbetweennodes.
ZhanXetal. demonstratedthatthecharacteristicsthatblock chain information cannot be changed at will, network resources are managed and monitored to ensure the uniquenessofdatainformation.Blockchaintechnologyand Internet of Things technology are integrated to label and managetangibleassetstoimprovethetrustworthinessand controllability of tangible asset management. Using block chain technology to increase network infrastructure protection can provide stable services for a variety of network applications while avoiding the maltreatment causedbynetworksecurityhazards.
Warzyński,Aetal.performedthe verificationoftheanomaly detection systems that has an ability to counter different type of attacks. This paper affords the initial outcomes to examinethe investigatepresenceofattackvector,thatmay useadverseexamplestohideaactualoutbreakfrombeing detectedintrusiondetectionsystems.
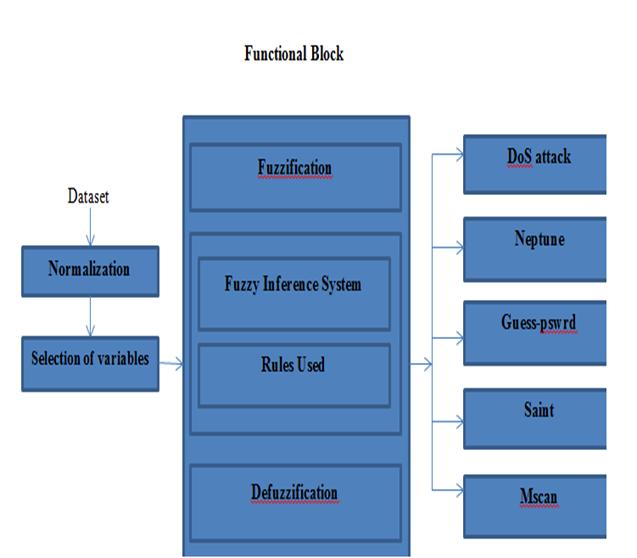
Fuzzy Controlled language: The proposed architecture of fuzzy controlled language contains normalizationandselectionofattributesbeforefuzzification.
b.FuzzyInferenceSystem:Fuzzyinferencesystemistheway toward planning the mapping from a given input to the outputusingfuzzylogic.Withthehelpofmappingofinputto theoutputdecisionscan be made,orpatternsrecognized.
International Research Journal of Engineering and Technology (IRJET) e ISSN: 2395 0056 Volume: 09 Issue: 01 | Jan 2022 www.irjet.net p ISSN: 2395 0072 © 2022, IRJET | Impact Factor value: 7.529 | ISO 9001:2008 Certified Journal | Page936 are continuous with a large domain of values. Some attributeshavelimitedcontributionindetectionofattacks. The attributes which do not contain any valuable informationforattacksareeliminatedfromthedatasets.21 attributesareconsideredwhichhavevaluableinformation about the attacks. The values which are not useful are eliminated. So, the features which contain valuable information for attacks are used for attack detection and classification.Variousstepsareperformedforselectionof attributesfromKDDdatasets. 1.1A)Attributenormalization:Therearedifferenttypesof valuespresentinaKDDdataset.Itincludes41attributes,7 discreteand34continuousvariables.The34attributesare takenfornormalization.InthisKDDdataset,somevaluesare highandsomevaluesareverylow.Theseelementscontain verylargerangeofvaluesie.0to5,13,1424. Toavoidthis, normalization is performed on selected values . With the helpofnormalization,thevaluesarenormalizedintherange of0and1. B) Method used for normalization Standard deviation methodisusedfornormalizationofdata.Standarddeviation givesbetterresultthananyothermethodwhichisusedfor normalization. Standard deviation is calculated with the followingequation: 2 1 1 N i Ni x 3.1 =Standarddeviation N=Noofinstances =Mean X=Samplemean B) Attribute selection: A KDD dataset contains 41 elements. Some attributes play important role in attack detection and some have not any role in attack detection. Performance of attack detection is reduced with these unnecessaryattributes.Computationaltimealsoincreases with more attributes. Selection of useful attributes will increasetheperformanceof thedetectionrate.Entropyis calculatedfortheselectionofattributes.Entropyismeasure of uncertainty and randomness. Very low values and very high values which come after entropy calculation are selectedforattackdetection. Entropyiscalculatedwiththis formula. nf i nf ai nf ai et 1 log …….3.2 et=Entropyofthedataset, isnumberoffeatures,ais 2.Layereddataset
FuzzyInferenceSystem
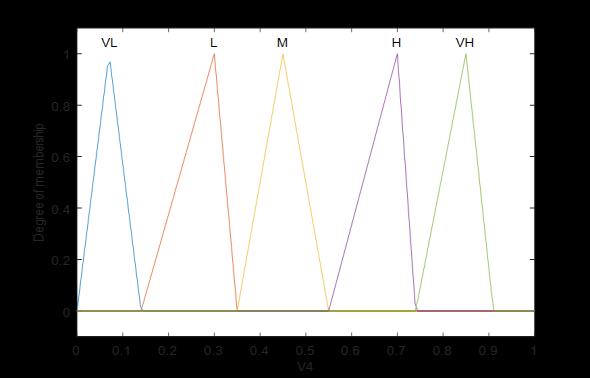
Membership function: Triangular membership function is used in this process of membership declaration Three variablesa,bandcareused,aandclocatethebaseofthe triangle and b locates peak of the triangle. The triangular membership function value of variable V0 is defined as [ (VL:0.000.050.100.15),(L:0.10 0.16,0..27 0.35),(M:0.27 0.36,0.50 0.60),(H:0.50 0.62,0.70 0.80),(VH:0.70 0.82,0.90 1.00)].Valuesofallvariablesaregivenintable3.1
Figure3.3Membershipvaluesofthevariable
a.Fuzzification:Intheprocessoffuzzificationconversionof crisp value to fuzzy value takes place for defining the membershipfunction.
a)Defuzzification://// Defuzzification is the process in which fuzzyvaluesareconvertedintocrispvaluesforidentifying the attacks using a layered approach. Centroid method is usedfordefuzzification.
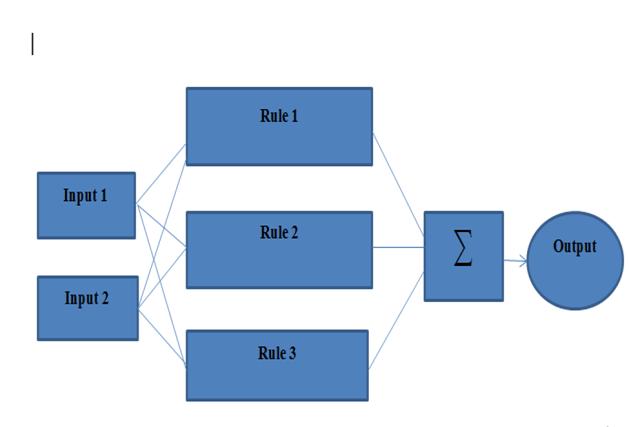
Theprocesscontainsfuzzyinferencesystem,ruleboxand defuzzificationunits.
Theprocessoffuzzyinferencesystemincludesalltheparts thataredescribedlogicaloperation,membershipfunction andIf Thenrules.Ruleswhichareusedforinferencesystem aregivenintable Figure3.23.2
1.1 If(V0isVL)and(V1isVH)and(V2isVL)and(V11isVL)then(SubAttack issmurf)(1) 1.2 If(V0isL)or(V1isL)or(V2isL)or(V11isL)or(V12isL)or(V13isH) or(V15isL)or(V16isM)then(SubAttackisneptune)(1)
3.1 If(V0isL)and(V1isVL)and(V2isL)and(V11isM)and(V13isVH)and (V15isM)then(SubAttackisprocesstable)(1)
1 If(Portisicmp)or(sishttp)or(fisS1)then(AttackisDOS)(1)
b) Ifruleis2.2thensubattackisguess_psword
c) Ifruleis2.3thensubattackissatan Ifruleis2.4thensubattackismscan Ifruleis2.5thensubattackissaint Ifruleis2.6thensubattackisportsweep Ifruleis2.7thensubattackisipsweep
d)
3.2 isIf(V0isVL)and(V1isL)and(V2isL)and(V3isVL)and(V5isVL)and(V6VL)and(V11isH)then(SubAttackispod)(1)
a) Ifruleis1.1thensubattackissmurf
2 If(Portisicmp)or(sisall_u)or(fisRSTR)then(Attackisprobe)(1)
e)
International Research Journal of Engineering and Technology (IRJET) e ISSN: 2395 0056 Volume: 09 Issue: 01 | Jan 2022 www.irjet.net p ISSN: 2395 0072 © 2022, IRJET | Impact Factor value: 7.529 | ISO 9001:2008 Certified Journal | Page937 max min max min tdt tutdt COG ……….3.3 Denotethealgebraicintegration,thismethodisalsoknown ascentreofgravity. 3Testingdatasets:Testingdataarecollectedwiththehelpof Wireshark.Thefuzzyruleistestedondatageneratedfrom Wireshark. Wireshark is an open source packet tracer. A networkpackettracercapturesrealtime networkpackets andtriestodisplayallthedetailsofthecapturedpackets. 3.2Rulesusedforattackdetection: Fuzzy inferencesystemworksbasedontherulesgiven in below table. Rules will detect main classes of attacks and their sub classes. Rules are designed with the help of variables which are identified by the process of normalization.Thesearethemembershipvaluesrangefrom variableV0toV22. 4. Proposed Algorithm for identifying attacks Step 1 Readdata Step 2 ManageData Step 3 NormalizeData Step 4 CreateFuzzyInferencesystems. a) Createinputmembershipfunction b) Createoutputmembershipfunction c) Createrules d) d)Parserules c)Generatefuzzy e) Step5ReadFuzzyvalues f) Step6EvaluateFuzzyvalues g) Step7Loopfromnumber1tothelengthofdata h) Step8Passtofuzzy i) Step9
3 If(Portisicmp)or(sisftp)or(fisS2)then(AttackisR2L)(1)
A) If result is rule 1 then DoS attack
g)
2.6 If(V0isL)and(V1isVL)and(V2isVL)and(V5isVL)and(V6isVL)and (V9isVH)and(V10isVH)and(V11isVL)and(V13isVH)and(V14isVL) and(V16isM)and(V20isVH)and(V21isVH)then(SubAttackisportsweep) (1) 2.7 If(V0isVL)and(V1isVL)and(V2isL)and(V6isVL)and(V9isVH)and (V10isVH)and(V11isVL)and(V13isVH)and(V14isVL)and(V16isM) and(V20isVH)and(V21isVH)then(SubAttackisipsweep)(1)
1.4 If(V0isVL)and(V1isM)and(V2isM)and(V11isVL)and(V13isVH) and(V15isL)then(SubAttackisback)(1)
3.3 If(V0isL)and(V1isL)and(V2isVL)and(V11isM)and(V13isVH)and (V14isM)and(V15isH)then(SubAttackissnmpguess)(1)
2.3 If(V0isM)and(V1isVL)and(V2isVL)and(V5isL)and(V6isVL)and (V9isM)and(V13isM)and(V14isVH)and(V16isL)then(SubAttackis satan)(1) 2.4 If(V0isVH)and(V1isVL)and(V2isVL)and(V4isVL)and(V7isVH) and(V15isL)and(V16isH)thenSubAttackismscan 2.5 If(V0isVL)and(V1isVL)and(V2isVL)and(V5isVL)and(V11isVH) and(V15isVH)and(V16isVH)then(SubAttackissaint)(1)
1.3 If(V0isM)and(V1isH)and(V2isL)and(V5isVL)and(V13isVH)then (SubAttackismailbomb)(1)
b) Ifruleis1.2thensubattackisNeptune Ifruleis1.3thensubattackismailbomb Ifruleis1.4thensubattackisback Ifruleis1.5thensubattackisapache2
a) Ifruleis2.1thensubattackissnmpgetattack
d)
c)
Sr.No RulesDesignedForFuzzyInferenceSystem
2.1 If(V0isVL)and(V1isM)and(V2isH)and(V5isL)and(V6isL)and (V11isVL)and(V13isVH)then(SubAttackissnmpgetattack)(1)
3.4 If(V0isVL)and(V1isVL)and(V2isVL)and(V11isVL)and(V13isVL) and(V14isVL)and(V15isVL)thenAttackisnomal Table 3.3 Comparison of normalization and membership function
B)Ifruleis2thenattackisProbe
2.2 If(V0isVL)or(V1isVL)or(V2isM)or(V4isVH)or(V5isVH)or(V6is VH)or(V11isVH)or(V18isVL)or(V19isL)or(V20isM)or(V21isM) then(SubAttackisguess_passwd)(1)
1.5 If(V0isVL)or(V1isVL)or(V2isVL)or(V7isH)or(V8isVH)or(V11is L)or(V13isVH)or(V20isH)or(V21isH)then(SubAttackisapache2)(1)
f)
e)
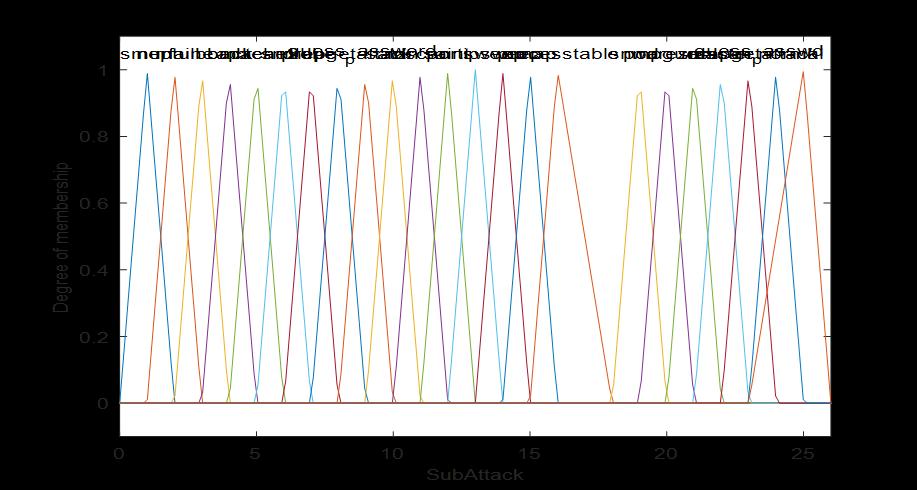
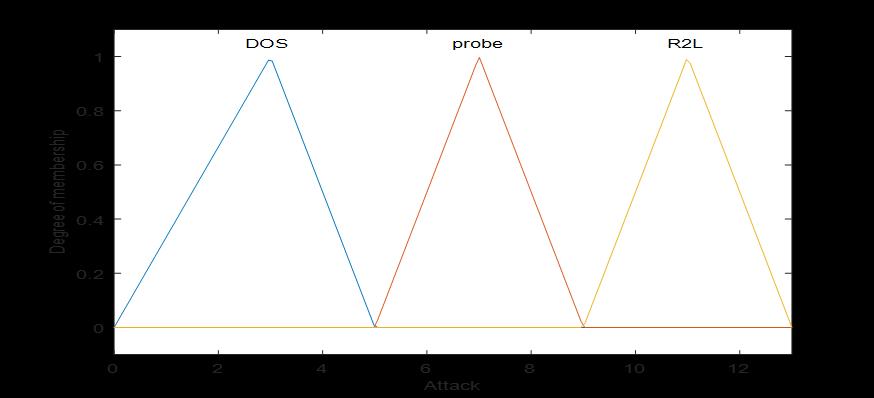
International Research Journal of Engineering and Technology (IRJET) e ISSN: 2395 0056 Volume: 09 Issue: 01 | Jan 2022 www.irjet.net p ISSN: 2395 0072 © 2022, IRJET | Impact Factor value: 7.529 | ISO 9001:2008 Certified Journal | Page938 C) If rule is 3 then attack is R2L a) Ifruleis3.1thensubattackisprocessstable b) Ifruleis3.2thensubattackispod c) Ifruleis3.3thensubattackissnmpguess d) ElseNormal 4 1 Implementation of Proposed Algorithm e) The variables which are taken are plot with the membership values. There are 21 variables are used for attackdetection.Someofthegraphwiththeirmembership Figure 3.4 Variable V0 with their membership value Figure 3.5 Variable V4 with their membership value Figure3.4and3.5showsthemembershipvaluesofvariable V0 and V4. This membership have five values ie VL, L, M, H,VH. Figure 3.6 Output values of various attacks Figure 3.7 Output values of various sub attacks Figure 3.6 and 3.7 give the membership values of main attacksandtheirsubattacks. 4.2Results and Analysis Morethan10,000recordstakenforattackdetection.Main classesofattackaredetectedandtheirsubattacksarealso NormalResultsdetected.Data=10899 DosAttack=529 ProbeAttack=448 R2LAttack=65 TotalPacket=11941 SmurfAttack=121 NeptuneAttack=60 MailbombAttack=92 BackAttack=27 TeardropAttack=1 SnmepgeAttack=55 GuessAttack=213 GuessPasswordAttack=28 MscanAttack=8 SaintAttack=112 iPsweepAttack=14
International Research Journal of Engineering and Technology (IRJET) e ISSN: 2395 0056 Volume: 09 Issue: 01 | Jan 2022 www.irjet.net p ISSN: 2395 0072 © 2022, IRJET | Impact Factor value: 7.529 | ISO 9001:2008 Certified Journal | Page939 PortSweepAttack=3 mapAttack=1 2001000 300 600500400 DosAttak ProbeAttack R2LAttack Attacks Packets Figure 3.8 Bar graph showing Dos, Probe and R2L attacks. 1160011400112001100010800106001040010200 11800 1220012000 TotalPacket NormalData TotalpacketsandCleanData Packets Figure 3.9 Bar graph showing total Packets checked and clean data detected. Figure3.8showsthenumberofmainattacksdetected,and figure3.9showsthegraph oftotal packetandthe normal data. 5. RESULTS AND DISCUSSIONS Theresultsobtainedshowedthatanaccuracywas 61.53% andperformancewas44.44%whichwere betterthanthe Attack’s Feature Selection Based Network Intrusion Detection System Using Fuzzy Control Language. The proposed system uses a self formulated normalization as shown in table 3.1 The formula used has been explained above. The membership function used by the proposed systemisTriangularwhichwasfoundtogivebetterresults asittakesminimum,maximumandpeakvaluesresultantly therangeisclearlydefined forthesystemtoarriveatthe results.Therulesarealsodesignedinsuchawaythatthey candetectmaximumpossibleattacks. Methodused Attack’sFeature Selection Based Network UsingDetectionIntrusionSystemFuzzyControl Proposed Language. onNormalizati VarVar VarVar Var n maxmin min 2 1 1 N i Ni x pMembershifunction Trapezoidal Triangular Formula used for accuracy Accuracy: 100100 R TAR ……..3.4 Withuseofthelayeredapproach,thesubclassesofattacks aredetected.Attacksaredetectedover11000datasets.Frist ofall,itdetectsmainclassofattacksandthenthesubclasses ofattacksaredetected. Figure3.10showsthegraphofnumbersofthesubattacks detected.Theseattacksaresmurf,Neptune,mailbomb,back, teardrop, snmpgetattack, Guess passwd, mscan, saint, portsweep,ipsweep,Nmap,snmpguess. Table3.4Improvementinnumberofattackdetected Attacks Attack’sFeatureSelectionBased NetworkIntrusionDetection SystemUsingFuzzyControl Language Propose Do’s Yes Yes Probe Yes Yes R2L Yes Yes Smurf Yes Yes Neptune Yes Yes Mailbomb No Yes Back Yes Yes TeardropApache2 Yes Yes Snmpgetattack No Yes Guesspsswd Yes Yes MscanSatan No Yes Saint No Yes Portsweep Yes Yes Ipsweep Yes Yes SnmpguessPodProcesstable No Yes Warezmaster Table 4.1 Number of sub attacks detected by layered classifier.
[1] Ding, W., Nayak, J., Naik, B., Pelusi, D., & Mishra, M. (2020). Fuzzy and Real Coded Chemical Reaction Optimization for Intrusion Detection in Industrial Big Data Environment. IEEE Transactions on Industrial Informatics,17(6),4298 4307.
International Research Journal of Engineering and Technology (IRJET) e ISSN: 2395 0056 Volume: 09 Issue: 01 | Jan 2022 www.irjet.net p ISSN: 2395 0072 © 2022, IRJET | Impact Factor value: 7.529 | ISO 9001:2008 Certified Journal | Page940 Sr.No. Layer Attack type No of detectedattack 1 DoS Smurf 121 Neptune 60 Mailbomb 92 Back 27 TeApacheardrop 1 2 Probe Snmpgetattack 28 Guess_passwd 213 MscanSatan 8 Saint 121 Portsweep 3 Ipsweep 14 Nmap 1 3 R2L SnmpguessPodProcesstable 55 Warezmaster 250200150100500 Attacksdetected Figure 4.2 Bar graph showing Attacks detected. 6. CONCLUSIONS Intrusion detection technology has always been a major topic in the realm of computer network security. The purpose of intrusion detection technology is to efficiently monitoranomalousdatatrafficinthenetworkinrealtime, prevent it while it is still budding, and isolate it from the targetregion,tokeeptrackofmaliciousactivityinatimely andefficientmanner.Wehaveshownthatthe Fuzzymodel ishighly efficaciousforthereductionof andforits higher accuracyrateincomparisonwithothermodels.Theresult obtained showed an accuracy of 61.53% ,The attacks detected were Mailbomb, Snmpgetattack, Mscan, Saint, Snmpguess are improved name of detected attacks.In the future,itmaybepossibletodeveloparealisticapplication basedonunsupervisedlearningmethodsthatmaynotonly identifyanintrusionbutalsoprovideuserswithalternate defencemechanisms. REFERENCES
[2] Douzi, S., Benchaji, I., & ElOuahidi, B. (2018, October). Hybrid approach for intrusion detection using fuzzy association rules. In 2018 2nd Cyber Security in NetworkingConference(CSNet)(pp.1 3).IEEE.
[3] Cristiani,A.L.,Lieira,D.D.,Meneguette,R.I.,&Camargo, H. A. (2020, November). A Fuzzy Intrusion Detection SystemforIdentifyingCyber AttacksonIoTNetworks. In 2020 IEEE Latin American Conference on Communications(LATINCOM)(pp.1 6).IEEE. [4] Saidi,F.,Trabelsi,Z.,&Ghazela,H.B.(2019,November). Fuzzy logic based intrusion detection system as a serviceformaliciousportscanningtrafficdetection.In 2019 IEEE/ACS 16th International Conference on ComputerSystemsandApplications(AICCSA)(pp.1 9). IEEE. [5] Kumar, M., & Singh, A. K. (2020, June). Distributed intrusiondetectionsystemusingblockchainandcloud computing infrastructure. In 2020 4th International Conference on Trends in Electronics and Informatics (ICOEI)(48184)(pp.248 252).IEEE. [6] . Kumari, V. V., & Varma, P. R. K. (2017, February). A semi supervisedintrusiondetectionsystemusingactive learning SVM and fuzzy c means clustering. In 2017 International Conference on I SMAC (IoT in Social, Mobile, Analytics and Cloud)(I SMAC) (pp. 481 485). IEEE. [7] Warzyński, A., & Kołaczek, G. (2018, July). Intrusion detection systems vulnerability on adversarial examples. In 2018 Innovations in Intelligent Systems andApplications(INISTA)(pp.1 4).IEEE.. [8] Zhan, X., Yuan, H., & Wang, X. (2019, September). ResearchonBlockChainNetworkIntrusionDetection System.In2019InternationalConferenceonComputer Network,ElectronicandAutomation(ICCNEA)(pp.191 196).IEEE. [9] Sukumar,J.A.,Pranav,I.,Neetish,M.M.,&Narayanan,J. (2018,September).Networkintrusiondetectionusing improved genetic k means algorithm. In 2018 International Conference on Advances in Computing, Communications and Informatics (ICACCI) (pp. 2441 2446).IEEE. [10] Gaied, I., Jemili, F., & Korbaa, O. (2015, November). Intrusiondetectionbasedonneuro fuzzyclassification. In 2015 IEEE/ACS 12th International Conference of ComputerSystemsandApplications(AICCSA)(pp.1 8). IEEE..\ [11] Haider,W.,Hu,J.,Slay,J.,Turnbull,B.P.,&Xie,Y.(2017). Generatingrealisticintrusiondetectionsystemdataset basedonfuzzyqualitativemodeling.JournalofNetwork andComputerApplications,87,185 192. [12] Kumari,V.V.,&Varma,P.R.K.(2017,February).Asemi supervised intrusion detection system using active learning SVM and fuzzy c means clustering. In 2017 International Conference on I SMAC (IoT in Social, Mobile, Analytics and Cloud)(I SMAC) (pp. 481 485). IEEE.
International Research Journal of Engineering and Technology (IRJET) e ISSN: 2395 0056 Volume: 09 Issue: 01 | Jan 2022 www.irjet.net p ISSN: 2395 0072 © 2022, IRJET | Impact Factor value: 7.529 | ISO 9001:2008 Certified Journal | Page941 [13] Shanmugavadivu,R.,&Nagarajan,N.(2011).Network intrusion detection system using fuzzy logic. Indian Journal of Computer Science and Engineering (IJCSE), 2(1),101 111. [14] Balan, E. V., Priyan, M. K., Gokulnath, C., & Devi, G. U. (2015). Fuzzy based intrusion detection systems in MANET.ProcediaComputerScience,50,109 114.