PLACING VALUE ON HEALTHCARE SECURITY ROLES
FUN WAYS TO TEACH STAFF SECURITY FUNDAMENTALS
ELEMENTS OF SUCCESSFUL DISASTER RECOVERY
PAGE 6
PAGE 16
PAGE 20
Canadian
January/February 2017
THE PUBLICATION FOR PROFESSIONAL SECURITY MANAGEMENT
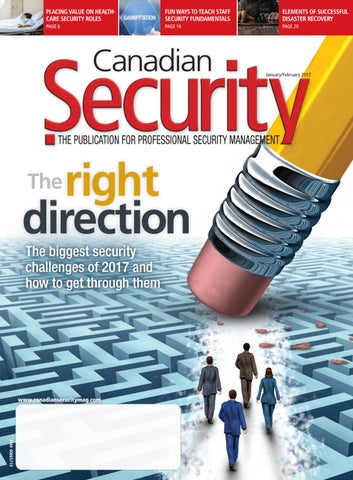
right direction The
The biggest security challenges of 2017 and how to get through them
www.canadiansecuritymag.com
PM# 40065710
January/February 2017 • www.canadiansecuritymag.com
BUILT IN SECURITY Protecting Canadians and their businesses comes naturally to us. Commissionaires offers more than just security. We provide a peace of mind that is backed up by experience, innovation and dedication.
TO FIND A SERVICE THAT IS RIGHT FOR YOU, CA L L : 877 322 6777
or visit commissionaires.ca/cdnsecurity
CONTENTS 3
Canadian Volume 39 Number 1
THE PUBLICATION FOR PROFESSIONAL SECURITY MANAGEMENT
Columns
Useful security advice for 2017
6 FOCUS ON HEALTH CARE SECURITY Patient watch plus
We asked our editorial advisory board to answer one question: What is the biggest challenge security professionals will face this year and how should they prepare? The answers may help you think differently about today’s (and tomorrow’s) challenges
8 PARTNERS AGAINST CRIME Critical thinking 9 MUNICIPAL MATTERS When the system breaks down
12
10 RISK PERSPECTIVE The next level
Departments Make a game of it
4 EDITOR’S NOTEBOOK Valued contributions
Training employees to recognize phishing attacks and cyber scams is a lot more effective if you make it engaging
5 TRENDING 11 ASIS UPDATE Eastern greetings
By Megan Brister and Tiffany Williams
21 BOOK REVIEW The truth about lying
16
22 PRODUCT FOCUS Locks & door hardware
visit www.CanadianSecuritymag.com Security leaders will be dropping by our studio in 2017, so be sure to check out the video section of our website for new content.
ARE YOU RECEIVING Canadian THE PUBLICATION FOR PROFESSIONAL SECURITY MANAGEMENT
e-news?
SUBSCRIBE TODAY! www.canadiansecuritymag.com @SecurityEd • January/February 2017
4 EDITOR’S NOTEBOOK By Neil Sutton
VALUED CONTRIBUTIONS Security questions and answers are always part of a larger discussion
R
ecently, Annex Business Media (publisher of this and more than 50 other magazines) undertook an exercise to establish a corporate values blueprint. The purpose was to identify goals, ideas, work habits, and of course, values, that were important to the organization across its many departments and divisions. To accomplish this, the company organized a values team made up of personnel from every department and level of seniority. Together they came up with six core ideals that make sense for everybody. I wasn’t part of this team, but I am the recipient of a document, and a broader philosophy, that has enshrined these ideals into our company culture. Or, to put it another way, the company culture has yielded these ideals over time and the working “We can assume group identified them. What really brought this home for me was setting this year will aside an hour or two to speak with a member of the values team about what each of those values means, bring significant how I live them (or how I don’t), and identifying areas challenges.” for personal growth. None of this was recorded, I wasn’t given a grade or evaluation — it was simply an honest discussion between two co-workers. I like to think our cover story for this issue follows the same espirits de corps. I asked Canadian Security’s editorial advisory board to think about a question for a few weeks, then submit an answer we could publish in the magazine. On the surface, the question does not directly relate to corporate culture, values, personal growth, or anything one would immediately associate with organizational culture, but in a very real sense it’s addressing all of those things and more. I asked the board: What will be the biggest challenge security professionals will face in 2017 and how should they prepare? Some of the answers were anticipated and some were not. All are good, insightful and worth your time. All, in some shape or form, talk about culture and values, whether they reflect the culture and values of the individual, the company or organization they represent or the professional security community in Canada. There are no perfect answers, no complete lists. That would be a virtual impossibility, since no one knows for sure the extent of the challenges security professionals will face this year. If the past few years are to be reckoned with, we can more or less assume that this one will bring significant challenges. If you want advice on cyber security, security budgets, professionalism, job mobility, risk assessment and more, turn to p. 12 and keep reading. As previously mentioned, Annex identified six core values. The reason I’m not listing them here is because yours might be different. It’s up to each of us and the organizations we work for to figure out what they are and do our best to embody them. I didn’t ask the advisory board to specifically identify values, but what they have written is equally important.
@SecurityEd
January/February 2017 • www.canadiansecuritymag.com
Canadian THE PUBLICATION FOR PROFESSIONAL SECURITY MANAGEMENT Group Publisher Paul Grossinger pgrossinger@annexweb.com
Art Director Graham Jeffrey gjeffrey@annexweb.com
Publisher Peter Young pyoung@annexweb.com
Account Coordinator Trish Ramsay tramsay@annexweb.com
Editor Neil Sutton nsutton@annexweb.com
COO Ted Markle tmarkle@annexweb.com
Assistant Editor Renée Francoeur rfrancoeur@annexweb.com
President & CEO Mike Fredericks
National Account Manager Jennifer Dyer jdyer@annexweb.com
Editorial and Sales Office 222 Edward Street, Aurora, Ontario L4G 1W6 (905) 727-0077 • Fax (905) 727-0017 Web Site: www.canadiansecuritymag.com Canadian Security is the key publication for professional security management in Canada, providing balanced editorial on issues relevant to end users across all industry sectors. Editorial content may, at times, be viewed as controversial but at all times serves to inform and educate readers on topics relevant to their individual and collective growth and interests. Canadian Security is published six times per year by Annex Business Media. Publication Mail Agreement #40065710 Printed in Canada I.S.S.N. 0709-3403 Subscription Rates Canada: 1 Year $40.95 + HST; U.S.A. (payable in US dollars): 1 Year $70.00; International (payable in US dollars): 1 Year $80.00 Circulation Tel: (416) 510-5189 Fax: (416) 510-5170 asingh@annexbizmedia.com 80 Valleybrook Drive, Toronto, ON M3B 2S9 The contents of Canadian Security are copyright by ©2017 Annex Publishing & Printing Inc. and may not be reproduced in whole or part without written consent. Annex Business Media disclaims any warranty as to the accuracy, completeness or currency of the contents of this publication and disclaims all liability in respect of the results of any action taken or not taken in reliance upon information in this publication.
Editorial Advisory Board Jason Caissie Profile Group
Sherri Ireland Security Exclusive
Theresa Rowsell Kit and Ace
Ken Close Trillium Health Partners
Mark LaLonde Simon Fraser University
Tim Saunders G4S Canada
Ashley Cooper Paladin Security
Bill McQuade Final Image
David Hyde Hyde & Assoc.
Carol Osler TD Bank
Sean Sportun Mac’s Convenience Stores
TRENDING 5 CALENDAR March 8, 2017 Security Career Expo Toronto, Ont. www.securitycareerexpo.ca April 5-7, 2017 ISC West Las Vegas, Nev. www.iscwest.com April 12,2017 Focus On Cyber Security Toronto, Ont. www.focusonseries.ca April 23-25, 2017 IAHSS Annual Conference & Exhibition Vancouver, B.C. www.iahss.org April 26, 2017 Security Canada East Laval, Que. www.securitycanadaexpo.com May 2, 2017 Blue Line Expo Mississauga, Ont. www.blueline.ca May 10, 2017 Security Canada Alberta Edmonton, Alta. www.securitycanadaexpo.com May 31, 2017 Security Canada Ottawa Ottawa, Ont. www.securitycanadaexpo.com May 31-June 1, 2017 CANSEC Ottawa, Ont. www.defenceandsecurity.ca/ CANSEC June 14-15, 2017 Security Summit Canada Toronto, Ont. www.securitysummitcanada.com June 23-27, 2017 IACLEA Annual Conference & Exposition Milwaukee, Wis. www.iaclea.org September 25-27, 2017 (ISC)² Security Congress Austin, Tex. congress.isc2.org
Canadian rejoins (ISC)² board Members and non-members alike are (ISC)² recently announced the annual welcome to attend its regular meetings. election results for its board of directors: “The reason why we don’t require three representatives from the U.S., one you to be a member is because we from New Zealand and one from Canada. have a lot of aspiring members who Greg Thompson, who is vicewant to break into the field,” president, global operational says Thompson. “We want risk and governance at to keep that avenue open to Scotiabank, has joined the them — making connections board, but not for the first with existing members and time. He previously served finding ways to achieve their from 2012 to 2015 as treasurer certifications are all positive and head of the compensation steps that not only help grow committee. Thompson said the global membership but membership is a serious time certainly help our communities. commitment but ultimately As as we all know, there’s said yes to returning. “I’ve Greg Thompson certainly a huge cyber-security made so many contacts and skills gap. The more we can pull so many close personal and people into the profession, I professional relationships since think the better off we’ll be.” my board membership last time. I’ve kept Thompson’s cyber security career in very close contact with the current spans almost two decades — the last 14 board and our local chapter.” years at Scotiabank. Thompson said his Thompson is also engaged on a role at the bank broadened in 2015 to regular basis with the Toronto chapter include global operational risk, including of (ISC)². He says the group is aiming to both IT and business risk. grow its ranks and encourage budding professionals to get more involved. — Neil Sutton
LETTER TO THE EDITOR Re: Snowden takes aim at Canadian anti-terror laws (Canadian Security, Nov/Dec 2016) I have been in law enforcement and security management for 41 years now and consider myself to be well versed in the security field with a background in both domestic and international terrorism. I have been an avid reader of your publication and read with great disgust the “Trending” article involving Edward Snowden. He is not an elected official and does not speak for me in any way, shape or form. Terrorism has taken on a new and disturbing face since Sept 11, 2001, with governments trying to react to ensure we do not have further incidents. We have failed a number of
times worldwide but in saying that, the public is not aware of the hundreds of attacks that have been prevented because of policies and laws now in place. Snowden has caused considerable damage to many investigations and lives, yet we allow him to continue to preach “his” beliefs for the sake of making conferences more interesting. Our democratic society is based on laws that protect all citizens, even if some people’s privacy rights may appear to be violated. Do you really think the criminals and terrorists care about our privacy rights or play by our rules? Paul Folkes RCMP (retired) @SecurityEd • January/February 2017
6 FOCUS ON HEALTH CARE SECURITY By Aidan West
PATIENT WATCH PLUS
C Health-care security role is more than just entry-level
ontinuous Visual Observation (CVO) programs vary significantly from healthcare organization to healthcare organization. CVO, also called “Patient Watch,” “1:1” or “Constant Observation” in many organizations, is often viewed as a low-paid, onboarding/entry-level position. The role is typically paid less than their base security counterparts and usually receives little or no training. The scenario often goes like this: a security professional is hired at an organization, assigned to a patient watch and left to his or her own devices. The guard often is unfamiliar with the organization, the unit and the service. They are unclear on what they are supposed to do or what is expected of them. Most learn the skill of CVO on the job. This approach creates a great deal of exposure for the organization and can lead to critical incidents and adverse patient outcomes such as elopement, self-harm and suicide. This will negatively reflect on the security service and its brand. As we have seen recently with the steady number of reports of hospital worker exposure to violence, the reliance on security will continue to increase. In order to effectively mitigate these risks and ensure the safety of all staff and patients, the approach to CVO needs to change. In preparing security professionals for CVO, the following are key elements that should be present in a successful program:
Leadership endorsement Directors, managers and supervisors need to demonstrate the value and importance of the role. This can be done in a number of ways, such as: developing a robust training program; ensure only trained staff conduct CVO; posting standard operating procedures that outline expectations and aspects of an effective CVO; and ensure supervisor contact throughout the course of the CVO.
Training Before being permitted to work CVO shifts, a security professional should receive targeted training that focuses on aspects such as: Situational Awareness (Cooper colour January/February 2017 • www.canadiansecuritymag.com
codes); Threat Risk Assessment (TRA) tools; risk mitigation strategies; authority to detain (legislative acts that apply); search parameters and roles; responsibilities and expectations; annual re-training in CVO skills should be required.
Compensation Ensure security guard salaries are reflective of the high risk nature of the position and are in line with base security compensation.
Metrics and measures As part of the service operation plan there should be an objective tied to CVO and reflected on the departmental scorecard. This should be available to all staff, and routinely reviewed and successful milestones should be celebrated.
Culture Change the organizational approach and thinking around CVO. This change should recognize that: • The role is a key risk mitigation function that can prevent significant patient events and avert possible litigation • It is not an entry level position but a skilled role requiring a trained seasoned professional. • It is a key component of a service’s recruit and retention strategy as it creates work opportunities for part-time and casual employees The success of any CVO program will depend on the level of investment the organization makes into the program. By providing staff with the knowledge, skills and tools to utilize during a “patient watch,” acknowledging the role as a skilled position, ensuring compensation equity with other departmental roles and clearly outlining expectations will empower staff, raise the standard of professionalism and the overall reputation of the hospital security service. Aidan West is a Registered Nurse & Licensed Security Professional and the Manager of Integrated Risk Service at the North Bay Regional Health Centre. West delivered a presentation on continuous visual observation Focus on Health Care Security, held in Toronto on Dec. 7, 2016.
Stay on top of the latest trends and security innovations. Canada’s security industry moves at an accelerated pace and Security Canada trade shows help you stay in the race. Held in six locations across Canada, Security Canada trade shows attract thousands of security professionals looking to find the best products and services the industry has to offer. Stay connected. Stay competitive. Register today for free. www.securitycanadaexpo.com
SC EAST
Laval, Quebec April 26
SC ALBERTA
Edmonton, Alberta May 10
SC OTTAWA Ottawa, Ontario May 31
SC WEST
Richmond, British Columbia June 21
SC ATLANTIC
Halifax, Nova Scotia September 13
SC CENTRAL Toronto, Ontario October 18 – 19
8 PARTNERS AGAINST CRIME
By Kenrick Bagnall
CRITICAL THINKING
I
The response to potentially deadly cyberattacks must be preparation and cooperation
t is human nature to sometimes take for in disrupted access to popular sites such as granted the services we expect to be there Paypal, Netflix, Spotify, Amazon and Twitter, when needed.We turn on the tap and to name just a few. clean water begins to flow. We flick a switch Cyber-attacks are wide-ranging and far and a dark room is instantly illuminated. We reaching. Organizations and individuals complain about the cost of fuel and traffic are being forced to do more to protect congestion yet still our vehicles traverse the their virtual assets. In the case of critical roadways of our cities and infrastructure, the we give little to no thought consequences of a cyberto the complex grid of attack could be measured “Law enforcement and traffic signals, cameras in financial losses and in and rail crossings that a worst-case scenario, the security agencies must contribute to making our loss of life. find better ways of journey safe. So what approach I’m going to suggest should be taken to make sharing information.” that there is no threat more our infrastructure more serious to the existence of secure? The approach starts human kind as we know with the right attitude or it today, than that of the threat to critical mindset. One must adopt a “when,” not “if” infrastructure. There was a time when it approach to cyber security. This mindset will was simply, “infrastructure” — the building help to promote the hyper vigilance necessary blocks that made up our supply chain, to keep systems safe. transportation and power grids, food and Strategic partnerships and good water supply, telecommunications, financial communication is also key, engaging with services, health care and more. law enforcement pre-cyber incident can These systems are now interconnected, make things run smoother. Organizations interdependent and in many cases vulnerable like the Canadian Cyber Threat Exchange to cyber-attacks. are excellent resources for the sharing of The Northeast power failure of 2003 information and cyber threat intelligence. effected the North East of the United States Due to the cross border nature of and most of the Province of Ontario. A cybercrime and the shared risk between software glitch caused a cascading effect, countries and governments, law enforcement shutting down adjacent power grids leaving and security agencies must strive to find better millions of people without power for eight to ways of sharing information and working 48 hours. In some remote areas, it took up to together with a view to mitigating the very two weeks to restore power. real threats to critical infrastructure. In 2010 a sophisticated cyber weapon In June 1996, Justice Archie Campbell that came to be known as Stuxnet was said it best in his report when he spoke responsible for disabling the Iranian nuclear about the need for systems to improve program at the Natanz enrichment facility. investigations: “A case management system The source code for Stuxnet has been widely is needed that is based on co-operation, shared and distributed across the Internet. rather than rivalry, among law enforcement In 2014, the Korea Hydro & Nuclear agencies.” Power Co Ltd, reported necessary cyber At a time during the infancy of the security upgrades were implemented after Internet, Justice Campbell had the vision non-critical data was stolen from their to know what one of the keys to successful computer systems. cybercrime investigations would be. It is In October of 2016 a massive DDoS our shared responsibility to see this vision (Distributed Denial of Service) attack was through by working together. executed against DYN, a DNS (Domain Name Services) service provider. This cyberKenrick Bagnall is a Detective Constable with the attack inundated the DYN servers with an Toronto Police Service Computer Cybercrime Unit (C3) unsustainable amount of requests, resulting @KenrickBagnall.
January/February 2017 • www.canadiansecuritymag.com
By Mel Gedruj
MUNICIPAL MATTERS 9
WHEN THE SYSTEM BREAKS DOWN
A So-called accidents may be avoided by rooting out organizational weakness
fter the first Persian Gulf war ended The primary reason would be that an and the no fly zone was in effect, organizational culture cannot be ready made. the U.S. Air Force was tasked with It is organic and evolves over time, therefore controlling the skies over Iraq. whether it goes in the positive safety culture This involved complex tasks requiring direction or not will depend on the quality of stringent measures of safety to prevent leadership and the workforce. While accidents systems failure at any given point. To caused by an individual’s inadequacy may that effect AWACS, the have limited consequences, most advanced Airborne organizational failures have Warning and Controls often disastrous outcomes. “Organizational culture Systems in the world, Another case is the were used. This would be collapse of the then world’s cannot be ready the equivalent in landsecond oldest merchant made. It is organic and based security to a C3 bank, Barings Bank. One (Command and Control aspect common to all evolves over time.” Centre). But, on a clear these situations seems to day in 1994, an accident revolve around a gradual occurred. Despite the most development of an unsafe sophisticated systems ever used and the culture with a mix of ingredients ranging highly trained and experienced professional from incompetent or unconcerned leadership, military personnel involved, two U.S. Black untested procedures, unreported small failures Hawk helicopters were shot down by two until the big one hits. As we can see this is not US F15s in a friendly fire. The choppers confined to one industry or sector and should were carrying 26 people. None survived. A be viewed as a risk management problem of number of studies were carried out in the the highest order. It does seem to affect highaftermath and even a book was published by tech systems where complexity cannot easily the mother of one of the victims. be comprehended by one individual, requiring There were a number of safety controls a layering of safety controls. James Reason that failed one after another. From the IFF was the co-author of an accident causation (Identity Friend or Foe) validation to the model analysis called the “Swiss Cheese radio frequency used down to the visual Model.” It features an easily understood verification. visual representation whereby, as long as the An article published by Dr. Nancy holes in the consecutive slices of cheese do not Leveson of MIT and Dr. Margaret-Ann align, there will be barriers. Accidents occur Storey of University of Victoria, used when all holes align. It reflects adequately all a System Model of Accidents to try to the instances discussed here. understand what took place. The step by To build strong safety cultures: allow step study clearly showed the blind spots reporting (even whistleblowing), provide of the system regardless of the elaborate strong leadership and induce a social structure that was meant to prevent exactly engineering process to make awareness this type of tragedy. paramount and negligence a thing of the Another incident occurred in 2003 past. Avoid rule violation punishment, a between a British Tornado aircraft and a U.S. sure recipe for concealment and encourage Patriot missile battery. Again, the after the positive compliance. Ultimately, reducing fact analysis identified the systemic failures the impact of individual human errors and inadequacies that led to the event. requires a well designed and tested Another research of interest was led organization safety model. by James Reason, of the University of To quote James Reason: “If eternal Manchester, U.K. In his paper “Achieving vigilance is the price of liberty, then chronic a Safety culture — theory and practice,” unease is the price of safety.” he demonstrates that an “unsafe” culture is mostly the result of organizational Mel Gedruj, OAA, CSPM is the president of V2PM Inc., inadequacies rather than individual accidents. specialized in municipal security management planning. @SecurityEd • January/February 2017
10 RISK PERSPECTIVE By Tim McCreight
THE NEXT LEVEL
A
2017 should be an instructive year as we assess recent risks and adopt new approaches
s I begin another year in the security addressed by a “stove pipe” approach to industry, I’m hopeful that during security. 2017 we see our profession focus Security organizations cannot operate on Enterprise Risk Management, and that in one or two silos, hoping to make their we begin the journey to identifying ourselves portion of the enterprise “secure.” Security more closely as enterprise risk professionals. programs cannot be successful if they only ASIS International fuelled some of address a portion of the enterprise, and do my optimism in November of last year not address risks from a holistic perspective. when they announced the resurrection of Throughout the history of this column, Enterprise Security Risk I’ve provided personal Management (ESRM) as examples of what can “We have moved to a strategic priority for go wrong with a risk ASIS and its members assessment, or a security a new level of threat: worldwide. program, if you only focus As a new member on immediate issues, and subtle threats that of the ASIS Board of don’t look at risks from a Directors, I’m encouraged more strategic perspective. mask themselves as to see the focus on We are entering something benign.” addressing risks across into a new time for an enterprise, and how our profession. Recent a security program can headlines across the globe positively affect the have documented what can risk posture of an organization while go wrong when risks are not identified, or enabling business objectives through the their potential impacts are not understood. treatment of risk. For those who’ve read From terrorist strikes to concerns about this column over the past couple of years, altering election outcomes, we were exposed you know where my passion lies — helping to a variety of security events in 2016 that an organization achieve its objectives by should be reviewed in 2017 and beyond. I identifying risks, and either accepting these believe we have moved into a new level of risks or working out strategies to mitigate threat — the subtle threats to organizations the risks. that mask themselves as something entirely I’m hoping this renewed focus on ESRM benign, but with the potential to critically triggers new conversations amongst security impact an organization. professionals, and in turn begins deeper As ASIS International begins its journey dialogues with executives in organizations back along the ESRM path, I am positive regarding enterprise risks. Security this journey is the right one for our professionals will soon see new material on profession to take. I also feel it is the right how ESRM principles can be incorporated time, and that myself and other Board of into a holistic security program, and how Director members are fully engaged and discussions with senior leadership regarding supportive of this initiative for ASIS and its risks and risk treatment can be an amazing members. avenue for greater collaboration across the We need to be engaged at a different enterprise. level within our organizations, looking This program isn’t a panacea for at enterprise level risks that require a the security industry, and it will not help collaborative approach to assess and resolve every risk facing every organization. understand the potential impacts to the On the contrary, this realignment toward organizations in our care. I think we have ESRM principles and practices will have a chance to start making a real difference the opposite effect — more risks will in our organizations if we can embrace the undoubtedly be uncovered in ESRM philosophy and approach. organizations, and from different areas of the Tim McCreight is director, advisory services at Above organization than typically Security (www.abovesecurity.com).
January/February 2017 • www.canadiansecuritymag.com
By Chris Clarke
ASIS UPDATE 11
Eastern greetings
O
n Dec. 7, over 30 professionals from the security management, consulting, integration, manufacturing, and guarding businesses came together for the 2016 ASIS International Atlantic Chapter 202 AGM and Networking event. On behalf of the Board, we greatly appreciate those of you who made it out and missed those of you who Chris Clarke understandably could not make it given the hectic season. Hopefully those who couldn’t make it will be able to make the next one in 2017. I am pleased to announce that the new Chair for ASIS 202 in 2017 will
be Dennis Delaney, CPP. Dennis moves from Co-Chair and he will be primed for a smooth transition. Jeff Vasseur will be joining as Secretary and Chris Leblanc will stay on as Young Professionals liaison. Other positions on the Board and Committees are still available and we welcome your involvement.
Some 2016 Chapter highlights: • Membership up from 25 to 39 • Members now in all 4 provinces • Certified members increased from four to six • Two events conducted in 2016 • Exhibited at Security Canada Atlantic Show
2017 Goals include: • Grow membership to 50 including
increased numbers in NB, NL, and PE • Grow number of Certified members to 10+ • Quarterly ASIS Atlantic meetings • Create or join ASIS Canada web site • Start sponsorship drive It has been a pleasure serving as Chair for the last two years. I wanted to leave the Chapter in a much better position than it was when I took over in 2015 and I feel comfortable saying that it is. Please stay involved and support the new Board and Chapter. Happy New Year to all of you! Chris Clarke is the outgoing Chairperson for ASIS International Atlantic Chapter 202.
Choose Bosch for integrated security solutions Increase security and automate functions for easy operation. Trigger and execute audio announcements based on security events. Manage data with enterprise-wide control of video and security devices. Bosch products integrate seamlessly to help you create complete security solutions.
Video Surveillance Audio and Voice
Watch our video to learn more: http://bit.ly/integratesecurity
Video Verification Services
Intrusion Detection Access Control
@SecurityEd • January/February 2017 CS_Bosch_JanFeb.indd 1
2017-01-20 9:52 AM
12 BEST PRACTICES
The
rightdirection Canadian Security’s editorial advisory board offers guidance for 2017 and beyond
C
anadian Security is fortunate to have a committed Editorial Advisory Board. To kick off this year, we asked each board member (there are a few additions for 2017) a simple two-part question with a complex answer: What is the biggest challenge security professionals will face in 2017 and how should they prepare? The answers are varied and thought-provoking.
Jason Caissie, Vice-President of Operations, Profile Group of Companies Our industry’s biggest problem continues to be public perception. It impacts every single one of us, whether we are selling security guard services or promoting an internal business case to executive leadership. If the general public develops their opinion of “security” through television or film, or from their interactions with low-wage uniformed security in their condominium or business, that opinion carries over to the people who are buying our services and paying our salaries. Public perception will keep security guard wages low, will dissuade young people from pursuing a security career and will keep corporate security departments relegated to the dreaded category of “cost centre.” We need to be seen as a business partner, and the best way to do that industry-wide is to showcase what we do and what makes us professional to the general public. There are some extraordinary tasks that security professionals in Canada accomplish in a day: kidnap and ransom events, active shooters, organized crime theft/fraud, undercover investigations, special event protection, and even just extraordinary customer service interactions by security guards. But we are reluctant to share these stories because of confidentiality, privacy, or because some of us still believe “knowledge is power” and sharing it makes us weaker. As an industry, we need to promote our professionalism in an engaging way to as wide an audience as we can. January/February 2017 • www.canadiansecuritymag.com
Ken Close, Manager Security & Parking Services, Trillium Health Partners Workplace violence is an ongoing challenge and one that I often deal with as manager of security in a major hospital. I’ve attended various seminars over the past few years and usually multiple presentations or discussions are devoted to this topic. This is a hot topic that is highlighted by the media and nursing unions that expect more will be done to protect staff. Most health-care organizations support safe work environments and due to the increase in attention to the topic, most are going above and beyond to improve safe work environments. The organization I work for has created a health workplace committee that has various initiatives to ensure a safe work environment. This committee will be reporting into the senior level of the organization to ensure they are aware of the initiatives available for employees. For our organization, and I’m sure many others, this will be an ongoing initiative in 2017 and for years to come. The expectation is that there will be ongoing support to ensure that all workers have a safe and enjoyable work environment.
David Hyde, Owner and Principal Consultant, David Hyde and Associates Protecting information will continue to be a top priority on the agenda of Canadian security professionals. Corporate and operational security management must avoid looking at information security (including IT/cyber) through a different lens than physical security. Fundamentally, the same concepts apply — security professionals across all domains need to characterize assets; identify threats; establish likelihood and impact of threat realization; assess vulnerability/existing security
controls; and enact/adjust controls to bring security risk levels to as low as reasonably practicable. Approached in the above manner, there is much to be gained from collaboration between physical and IT security pros. Corporate/operational security leaders should understand the primary methods of information targeting — including theft, solicitation, hostile interception, malicious attack and inadvertent disclosure. They must also know the primary avenues of protection — including employee screening, awareness/education, security culture, information classification, technology-based controls, physical security controls, administrative controls, monitoring and response protocols, information security principles (e.g., need-toknow, need-to-go, principle of least privilege, clean desk, etc.) and so on.
Sherri Ireland, Director of Operations, Security Exclusive The physical security industry is a mature industry and best practices are well documented. The challenge in 2017 is, how will cyber security risks impact the physical security business? Cyber attacks in 2016 utilized vulnerable CCTV cameras and DVR/NVRs to propagate DDoS (Distributed Denial of Service) attacks on many well-known organizations, including Twitter. Security professionals must understand the risks that are inherent to the equipment they have installed in their facilities and hold their vendors accountable to ensure strict username and passwords policies are in place for all IP-based equipment. If the IP devices do not have user name and password capability, they should not be installed on a network with external access. As malware becomes more sophisticated, it requires a balancing act when managing people. Do you continue to allow security officers and alarm monitoring operators unrestricted access to the Internet? Do you diminish their ability to perform their jobs and restrict all access to eliminate risk? What type of education do you have in place for your staff regarding cyber risks? Continuing education for security professionals is critical. They must understand cyber security risks, ransomware and plan how your organization will handle an attack to minimize financial risk and for business continuity. An enhanced partnership with the IT department is crucial to the security industry today.
Mark LaLonde, Chief Safety Officer, Simon Fraser University While there are many different trends, outside influences and legislative changes that continue to shape the broad industry we work in, one that I am particularly focused on is the increasing public expectation of greater integration and co-operation between private and public sector actors involved in providing community safety and crime prevention services. This suggests a tiered delivery of services, or as some describe it, @SecurityEd • January/February 2017
14 BEST PRACTICES a continuum of services. Issues of privacy, governance, civilian oversight and agreement on shared goals are all part of the discussion. This is an evolving conversation that is taking place not only in Canada, but in other countries where there are diverse private and public actors who are responsible for services ranging from parking control, bylaw enforcement, security in mass private and quasi-public spaces, investigations, emergency preparedness and response. Within this discussion is the evolving notion of what is “policing” beyond the traditional notion of a job description and perceiving it instead as a service that includes maintaining order, preventing crime and enforcing rules. In this sense, there are a range of entities engaged in policing — private security, bylaw officers, special constables and municipal police officers. The question we are left with is what model of public safety service delivery will work best in urban and rural contexts and is also fair, equitable and meets a consistent professional standard.
Bill McQuade, President, Final Image Inc. We often hear industry peers say the security industry is changing. The reality is our industry changed several years ago. To be successful today, security professionals should have a solid understanding of business fundamentals as it relates to their organization. They also need to have better than average skills in communicating the benefits of a well thought-out security strategy to senior management. At Final Image we engage with many individuals at various stages of their career. It’s unfortunate some find themselves in over their head today due to the fact they are highly invested in the way things used to be and sometimes are adverse to change. My advice to anyone hoping to advance his or her career in the security profession is to embrace change and become fully committed. Obtaining industry certifications is certainly a good way of demonstrating you have the drive and passion to enhance your career by staying current with industry best practices. Network with thought leaders, attend trade shows and aspire to become a subject matter expert in your field. Read as much as possible — specifically around cyber breaches and technology.
Carol Osler, SVP and Head, Financial Crimes & Fraud Management Group, TD Bank Group Currently, the top security challenges faced by our industry vary widely — from the persistent threat of increased social activism and civil protests to cyber-attacks. Which means the security industry needs to be ready for almost anything. To respond quickly and ensure a consistent state of January/February 2017 • www.canadiansecuritymag.com
readiness, security plans need to be constantly evaluated, tested and adjusted to deal with these security challenges. Industry and intelligence sharing between law enforcement agencies and corporations will also continue to play a critical role and inform effective preparation strategies. Cyber-attacks have presented a unique security challenge. The speed and persistence of such attacks require faster identification and prevention strategies that go beyond our traditional defence and protection principles and practices. Passive monitoring tactics will need to be transformed into active monitoring strategies focused on a wider range of targets, both internal and external. The emergence of the Internet of Things (IoT) into corporate environments will challenge our current vulnerability assessment programs, and require coverage of a wider spectrum of interconnected technologies. Clarifying risks related to trusted insiders will also take on increased focus as corporations design more effective programs to monitor those with access to critical company data. While traditional security principles and practices will continue to apply, the need for rapid analysis of security and intelligence information will be critical. As such, we should expect to see an increase in security fusion programs allowing multiple data sources to be consumed, analyzed and quickly acted on.
Theresa Rowsell, Asset Integrity & Inventory, Kit and Ace As 2017 arrives, protecting our businesses from hackers and virtual crime rings continues to be top of mind for security professionals. Rightfully so, as digital technology has become the heart of our businesses. That said, the bigger picture means addressing this but also going beyond the digital world. Having a business continuity plan in place to match the type and size of your business is a must. We’ve seen a steady increase of global events that have the potential to derail your organization’s aspirations and even bankrupt smaller organizations or start-ups. Disruptive protests, workplace violence, cyber attacks targeting company data and violent incidents around our businesses and where our teams live, are events that can create business disruption. The direct impact and potential ripple effect of a single event, or series of events, can result in injuries, profit loss and brand reputation damage. Supporting the success of our companies means security professionals must take intentional and proactive steps. Along with protecting consumer and private company data, it is important to review, update, or create an adequate program for business interruptions that includes: Employee support; public relations representation; appropriate insurance coverage; emergency preparedness and training programs and business continuity planning. Preparation will not prevent uncontrollable events, but it will help to avoid crippling your business and will mitigate the impact on your team, customers, brand and operations.
BEST PRACTICES Tim Saunders, Chief Business Development Officer, G4S Secure Solutions Canada In 2017 the biggest challenge facing security professionals will be the increasing demands by their organization to show a return on investment. The solution for security professionals is to demonstrate an enterprise-wide approach to managing security risk. They should be prepared to continually assess every element of a security program. From there they must understand how each element relates to one another and have the knowledge to find efficiency. For example, can the security guard stationed after-hours be augmented with off-site video monitoring as a “force multiplier” or can the client use off-site video monitoring to altogether replace that shift without compromising the security posture of the site? Furthermore, how does the security program relate to the broader organization? In every large company, there are competing priorities for budget dollars so understanding how your department affects others is critical to your success. Successful security professionals will be those who are generalists, those with a good working knowledge of all facets of security, and those with the contacts in the industry to leverage specialists when required.
Sean Sportun, Manager, Security & Loss Prevention, Mac’s Convenience Stores, Central Canada Outside of the evolving reality of terrorist threats, the biggest challenge for security professionals in 2017 is twofold: the continued advancement of the digital world and its vulnerability to crime, and the reduction of loss prevention funding as a result. These new age criminals possess the information, the means and the motivation to ensure high-profile security breaches continue to make headlines; while disrupting businesses of all sizes. As a result, businesses will need to deploy IT resources in an attempt to protect their valued consumers and maintain their brand reputation. The continued investment on the IT end could result in shrinking budgets on the loss prevention side — which is never good. Loss prevention has historically been viewed by operations as a “cost centre” not a revenue generator, making it the likely area for businesses to pull funding from — which could cause other areas of the business to be compromised. Therefore, it is essential for those in high-level loss prevention positions to continue demonstrating the value that loss prevention plays in the organization.
We pride ourselves in the effort put forth, the lessons learned, and successes achieved along the way to becoming the LEADER of one of the fastest growing markets in the world.
Connect with us:
www.hikvision.com
CredWords-Ad__Leader.indd 8 CS_Hikvision_JanFeb.indd 1
@SecurityEd • January/February 2017 1/23/17 10:00 AM 2017-01-23 2:36 PM
15
16 EDUCATION & TRAINING
Make a game of it Training employees in security best practices doesn’t have to be drudgery (or overly expensive) By Megan Brister and Tiffany Williams
U
sers continue to be the most common security vulnerability, with, according to Gartner, 85 per cent of hacks resulting from accidental disclosures and social engineering. However, changing user security behaviour is often left to annual compliance training or focused exclusively on phishing tests, and will result in little measurable improvement to security. Often, training is an “add on” to the security program — something for staff to do in their spare time. In fact, according to a Securing the Human report, more than 50 per cent of awareness personnel have a budget of $5,000 or less. We see training programs and awareness campaigns in other areas — workplace safety at oil and gas companies or clean hands programs in hospitals — succeed in changing how users behave on a day-to-day basis. These training and awareness programs have the same challenges of limited investment and personnel that security programs do. How do cyber security training and awareness personnel learn from the success of other industries and training areas to improve the “human firewall”? Drawing on innovative concepts used
outside the cyber security training and awareness space, organizations can think differently about how they change user security behaviours. What follows are successful training and awareness programs that made measureable improvements in user behaviour. These examples are intended to inspire and kick-start your cyber security training and awareness program and help you realize a shift in behaviour — that ultimately helps protects your critical data and assets.
Gamification Think Pokemon Go. Gamification incorporates game mechanisms — such as leaderboards, levels, and points — into non-game activities to engage and motivate users. Gamification enables organizations to take existing training material that staff may not be using and encourages staff to use it through an online community.
January/February 2017 • www.canadiansecuritymag.com
Ford Motor Company of Canada is an example of successful gamification of existing training content. Ford wanted to improve safety, customer service, and sales. Ford already had training material in these areas. Staff just were not using it. With gamification provider Bunchball, Ford created an online community with levels, badges, trophies, and friendly competition between staff. The result: the first day the site launched, it had more than 100,000 unique visits. Deloitte also gamified its existing Executive Leadership Program — a program with dozens of courses and training content, which went largely under-utilized. In doing so, Deloitte generated 50 per cent faster course content completion. “At Deloitte, we are seeing an uptake in innovative gamified cyber security training solutions. Organizations are creating online communities that enable employees to enter into friendly
EDUCATION & TRAINING 17 social competition and get rewarded to be security champions,” says Marc MacKinnon, Cyber Risk Services Partner at Deloitte Canada.
Rewards and incentives Most security awareness programs produce little improvement due to the focus on dispensing information, rather than influencing on-the-job behaviour of employees. Understanding and using the principles of behavioural psychology helps define training approaches that can effectively change high risk user behaviours. Embedding rewards and incentives (e.g. points programs, gift cards, extra budget for team activities) into security training and education is a way to use the principles of Reciprocity/ Consequence (i.e. people feel obliged to repay, in kind, what has been given to them) or Scarcity (i.e. people overvalue things that are rare, lack availability,
to capture licence plates of those going or are difficult to acquire) to encourage the speed limit. Those people were better security behaviour. entered into a lottery and one lucky In the security space when we use person was selected each month to incentives, they are often based on the receive a percentage of the fine collected “consequence” side of the Reciprocity/ for the month. Consequence Principle. For example, How can you giving users “tickets” apply this principle to for leaving their your security training computers unlocked “Making cyber security and awareness and unattended or training relatable program? Reward leaving confidential departments and documents out — in improves uptake, teams who follow a contravention of a clean desk protocol Clean Desk Policy. understanding.” with an extra social The Swedish event each year. Speed Lottery is an example of applying the “reciprocity” side of the principle Make it relatable to change user behaviour and, in this Cyber security training and education case, reduce speeding. In addition to programs often focus on policy and punishing the high risk behaviour procedures that employees need to — speeding — Sweden rewarded the understand and apply to their daydesired user behaviour — going the to-day work. What if organizations speed limit — by using a traffic camera scrapped their traditional cyber security
Our goal, as the Leading Security Provider, is to drive efficiencies within a client’s security.
We continually strive for methods to meet each client’s unique security requirements while keeping the client’s business goals and budget in mind. We are dedicated to using our resources and experience to create security solutions that address the rising costs of the security profession. The solution is Integrated Guarding, which can combine all three or any combination of our guarding services — On-site, Mobile and Remote — to provide a comprehensive, cutting edge security program. As the leading security provider, Securitas Canada offers security solutions, including on-site security guards, mobile patrol, remote security monitoring, and corporate risk management.
www.securitas.ca — 800-268-0545 @SecurityEd • January/February 2017 CS_Securitas_Feb.indd 1
2017-01-24 2:43 PM
18 EDUCATION & TRAINING
JUNE 14-15, 2017
UNIVERSAL EVENTSPACE • TORONTO
HELP SHAPE THE FUTURE OF CANADA’S SECURITY INDUSTRY SESSION TOPICS: • CYBER SECURITY • SECURITY METRICS • IoT • NATIONAL DEFENCE AND MUCH MORE
SecuritySummitCanada.com Presented by
Canadian THE PUBLICATION FOR PROFESSIONAL SECURITY MANAGEMENT
January/February 2017 • www.canadiansecuritymag.com
training and helped employees apply good security practices to their personal use of technology, such as sharing pictures with friends over Instagram, contributing to a LinkedIn discussion, or buying merchandise online? Deloitte has found that making cyber security training relatable improves uptake, understanding, and application of secure practices. Employees retain knowledge that relates to not only their work, but also their personal circumstances. The UNICEF Dirty Water Campaign is an example of making a topic relatable and yielding significant results. UNICEF wanted to raise awareness and funding for the thousands of children dying each day from lack of clean water. UNICEF bottled dirty water in eight lethal varieties, converted a vending machine to dispense the water, and launched it in Manhattan. Individuals could then “buy” the dirty water through the vending machine and, in doing so, donate to UNICEF’s campaign. By delivering the message in a form to which the public relates (bottled vending water), this innovative media engaged over 7,500 pedestrians, attracted worldwide media coverage, and increased donations beyond expectation. If you think your security training budget is tight, UNICEF did this with a zero dollar budget. There are some straightforward and equally lowcost training ideas to make cyber security relatable in the workplace: • Providing safe online shopping tips or sessions to employees and their families during December. Employees will apply similar online security and password management principles to their work accounts. • Setting up a rogue wireless access point at an off-site meeting (e.g. SSID “conferernceconnect”, with an extra “r”) and seeing how many people connect, then sharing this information and the not-so-careful users during the opening remarks of the meeting. • Publishing a YouTube video series (of publicly available videos) on social engineering individuals’ personal (e.g. phone, bank, insurance) accounts to help Services Desk personnel recognize suspicious behaviour. • Creating a contest in which staff create their own phishing emails to help them understand how phishing works. Have management select the best email for the upcoming phishing test and reward the winning employee. We recognize that even the most innovative idea cannot be successful without the support and investment of leadership. The ideas discussed above are an opportunity to have a more creative conversation with your leadership team and training personnel about refocusing training and awareness efforts. Using gamification and rewards, and making training relatable will help organizations get users’ attention and improve the “human firewall” to defend against cyber-attacks. Megan Brister and Tiffany Williams are cyber security professionals in Deloitte’s Cyber Risk Services practice. (www.deloitte.ca).
Smart access means seamless integration.
Keyscan Aurora V 1.0.14 Access Control Management software seamlessly integrates with Kaba E-Plex® wireless locks and other popular brands of wireless locking systems to provide a single software platform solution.
Advanced security functions include managing, auditing, facility lockdown and controlling access for any number of users, using the same credential at every door throughout a facility.
New interface features – • Microsoft® Certified Webcam support • Multilingual support in four languages • Suprema Biometric reader integration • Easy Lobby Visitor Management integration
Smart access means Aurora – total system control you can trust. 1.888.539.7226 keyscan.ca
20 EXPERT ADVICE
BEYOND BACKUPS Daren Hanson is the vice-president of sales and business development for TeraGo (www.terago.ca)
B
ig data has been described as the “new currency” for business, and with the number of threats to data security growing, protecting that data has become a top concern. One of the best ways a company can protect itself is to implement an effective Disaster Recovery (DR) plan. Whether your company is starting from scratch or needs to improve your current DR plan, these elements will be your best defence against a host of threats.
Properly identify threats and dependencies:
Test regularly: TeraGo’s study found
According to a recent TeraGo study, 45 per cent of companies are not able to identify all the potential threats to their data security. Be sure to conduct a thorough assessment of the potential operational failures, human-induced events, natural disasters and third-party partners, suppliers, and service providers that could impact your data security and operations.
that of those companies that do have a strategy in place, 81 per cent are not testing them to industry standards. To test the effectiveness of a DR plan it should be subject to a walkthrough by the DR team, a recovery simulation, or operational test on a quarterly basis.
Put a plan in place: Develop an easy-to-use, repeatable process that covers each step for recovering damaged IT assets and clearly outlines the procedures necessary to recover them and return back to their normal operation as soon as possible. It’s also wise to plan for duplication of skills so you have at least one backup person.
Outsource to a trusted advisor: The biggest challenge that companies face when it comes to DR planning and testing is finding and committing the proper resources. A Managed Service Provider can effectively develop, manage, test and execute a DR plan by working with business managers to identify threats to the company. This also allows the core business team to concentrate on operating the business.
cyber security APRIL 12, 2017
UNIVERSAL EVENTSPACE, VAUGHAN, ON
WHY YOU SHOULD ATTEND: • Insight into the Federal Government’s national cyber security program • Maintaining the security and integrity of corporate data • Cyber security and the justice system Brought to you by
REGISTER TODAY • SPACE IS LIMITED focusonseries.ca January/February 2017 • www.canadiansecuritymag.com
By Derek Knights
BOOK REVIEW 21
THE TRUTH ABOUT LYING
A Field Guide to Lies: Critical Thinking in the Information Age By Daniel J. Levitin Penguin Canada ISBN 978-0670069941
T
here’s a saying, “A lie travels around the globe while the truth is putting on its shoes,” that many attribute to Mark Twain. If they do, they’re wrong — maybe they’re lying. Poor Mr. Twain also apparently never said, “It ain’t what you don’t know that gets you into trouble. It’s what you know for sure that just ain’t so.” This latter quote opens Part One of Daniel Levitin’s book, “A Field Guide for Lies — Critical Thinking in the Information Age.” The dust jacket calls this book a “primer for the critical thinking that is now more necessary than ever” and that people today are “bombarded” daily with “bad data, half-truths, and outright lies.” Well, it is and we are. For anyone who deals in information accuracy this is an important book. Its author is on the faculties of both McGill University in Montreal and the University of California at Berkeley. I also reviewed his previous book, “The Organized Mind,” in this magazine. Both books show that Professor Levitin has much to say about clarity and discrimination in thinking. The book is in three parts: Part One: Evaluating Numbers; Part Two: Evaluating Words; and Part Three:
Evaluating the World. Part One is particularly interesting for security managers who need to report to senior management with numerical metrics, or maybe more importantly, those who receive those reports! The professor takes great pains to explain how clever manipulation of an x- or y-axis can change a reader’s perception. He shows that merely using averages, without context or care in sampling, can result in “truths” such as: “On average, humans have one testicle.” Part Two features chapters such as: “How Do We Know?” and “Counterknowledge.” In the former, he shows us how we are a story-telling species that acquires information in three ways: we discover it, we absorb it implicitly, or someone tells us (mostly this last one). What is the speed of light? 186,000 miles per second. How do you know? Someone told me. Do you doubt them? No. This is how much of our learning goes. Counterknowledge, then, is a term used to describe the fake stuff, the Facebook fodder, the nonsense spewed lately in a certain election (well, probably
all elections!). In the absence of criticalthinking people, humans will believe this stuff too easily. Part Three gets very technical. Once again, the professor delves into the brain, our “giant pattern detector” that fools us more often than not because it can “project” patterns or significance onto circumstances that don’t warrant it. Have you ever been thinking of someone and just then that person phones or texts you? If it ever happened, you would remember it. But you won’t remember all the times you were thinking of someone and he or she never called. And trust me, this part gets way more technical than that! The Internet permits vast amounts of real and fake knowledge to sit side-byside: knowledge and counterknowledge. It’s training our minds to think critically — and then thinking that way all the time — that will lead us to success. So will reading this book. Derek Knights, CPP, CISSP, CFE CIPP/C, PCI, is the senior manager, strategic initiatives, global security and investigations, at the TD Bank Group (www. tdbank.com). @SecurityEd • January/February 2017
22 PRODUCT FOCUS LOCKS AND DOOR HARDWARE Self-powered lock Dormakaba The Kaba PowerPlex 2000 self-powered electronic lock generates its own power through PowerStar technology, making it an efficient and versatile electronic lockset available with virtually no maintenance costs. Every time the lever is activated, the lock is energized to provide PIN code access. The lock can be simply programmed with as many as 100 different user-codes and five different authority levels with audit trail accountability of the past 1,000 events. The PowerPlex is ANSI/BMHA Grade 1 and is available for cylindrical, mortise and exit trim applications. www.dormakaba.com
Push plate switches Camden Door Controls The CM-35N Ontario Building Code (OBC) compliant push plate switches have a 4-1/2” tall x 2” wide faceplate and can be mounted on 1-3/4” width frames and boxes. The CM-35N was developed specifically for the Ontario automatic door market and features the small mounting footprint of Camden’s CM-25 and the OBC compliant faceplate of its CM-35 single gang series. CM-35 push plate switches are available with a range of graphic options. While CM-35N push plate switches are small enough to fit on door jambs, the regulation 368/13 amendment to the OBC, which became effective Jan. 1, 2015, prohibits that placement in automatic door applications. Switches must be placed a minimum of 600mm (23 -1/2”) beyond the door swing. www.camdencontrols.com
Swing handle with integrated RFID Southco The H3-EM Electronic Locking Swinghandle Series now includes an H3-EM with Integrated Multi-class RFID Reader. It includes the same intelligent electronic locking and monitoring features as the standard H3-EM, but also reads HID 125 kHz RFID credentials and 13.56 MHz iCLASS smart card based credentials. The H3-EM features an integrated HID SE smart card reader and supports multiple readers. It also features integrated LED indicators as well as single-hole panel preparation that is compatible with industry standard enclosures for OEM integration or field retrofits. When connected to an access control system, the H3-EM enables the user to track and record access to the electronic locks, providing an audit trail. www.southco.com
Laser engraved access control Farpointe Data Proximity and smart card credentials are now available with tactile laser engraving. Whether clamshell, printable, printable with magnetic stripe card or key ring or disc tag, Farpointe will permanently laser engrave logos and text, URLs, signature blocks, messaging, other graphics or whatever the manufacturer, integrator or end customer wants. Historically, dye transfer has been the preferred method for adding graphics on identification cards. Laser engraving lets security systems manufacturers, integrators and dealers mark access cards and tags permanently. The images and text can be individualized for each customer’s or organization’s needs. www.farpointedata.com
Bluetooth-enabled keys Medeco Medeco XT and Medeco CLIQ Intelligent Keys feature an optional Bluetooth upgrade. Bluetooth Smart Technology enhances the Medeco Intelligent Keys by connecting wirelessly to most smartphone and tablets using mobile apps. The “connected” Intelligent Keys allow administrators to remotely provide access and schedules to remote key holders, eliminating visits to centralized programming or docking stations. Both the Medeco XT and Medeco M3 CLIQ connected Intelligent Keys are backward compatible with most existing electronic cylinders. Companion apps for the connected keys are available for both Android and iOS mobile platforms.The apps use a simple key holder interface for ease of pairing with and updating the connected Intelligent Keys. www.medeco.com
Digital door lock Adams Rite The Adams Rite RITE Touch digital door lock features a new ADA compliant accessibility lever. The digital door lock provides keyless access control for all-glass openings, offering stylish and flexible access control for single or double glass doors. Intended for indoor applications, the easy to install surface mounted RITE Touch requires no modification to the glass. With choice of thumbturn or ADA compliant accessibility lever, the RITE Touch provides aesthetics with the latest touch screen technology for style and security. www.adamsrite.com
AD INDEX Avigilon 23 www.avigilon.com Bosch 11 http://bit.ly/integratesecurity CANASA 7 www.securitycanadaexpo.com Commissionaires 2 www.commissionaires.ca Focus On 20 www.focusonseries.ca January/February 2017 • www.canadiansecuritymag.com
G4S Hikvision Securitas Security Summit Canada Winsted
24 www.g4s.ca 15 www.hikvision.com 17 www.securitas.ca 18 www.securitysummitcanada.com 13 www.winsted.com
Protect what’s most valuable
Harness the power of intuitive security. Avigilon brings you technology that enables more profitable decisions. From products to customer service to innovative industry breakthroughs, we’ve got the solutions businesses trust when security matters.
• • • • •
Open Video Management Software Self-Learning Video Analytics Superior HD Cameras Storage Management & Data Protection Access Control
Learn more at avigilon.com
© 2017, Avigilon Corporation. All rights reserved. AVIGILON, the AVIGILON logo and TRUSTED SECURITY SOLUTIONS are trademarks of Avigilon Corporation.
3 pm Saturday and all’s well. Let’s keep it that way.
Risk Consulting
Software & Technology
Systems Integration
Security Personnel
AMAG Technology Symmetry GUEST Security Products Magazine New Product of the Year 2016 Visitor Management
When you prepare, you prevent. Preparedness brings peace of mind. And G4S can help you stay ready, with everything from risk analysis and managed services to technology and security personnel. Because it’s good to know you’ve done everything you can to help mitigate risk. To stay prepared, please visit g4s.ca or call 888-717-4447.
culpa qui officia deserunt mollit anim id est laborum et dolor