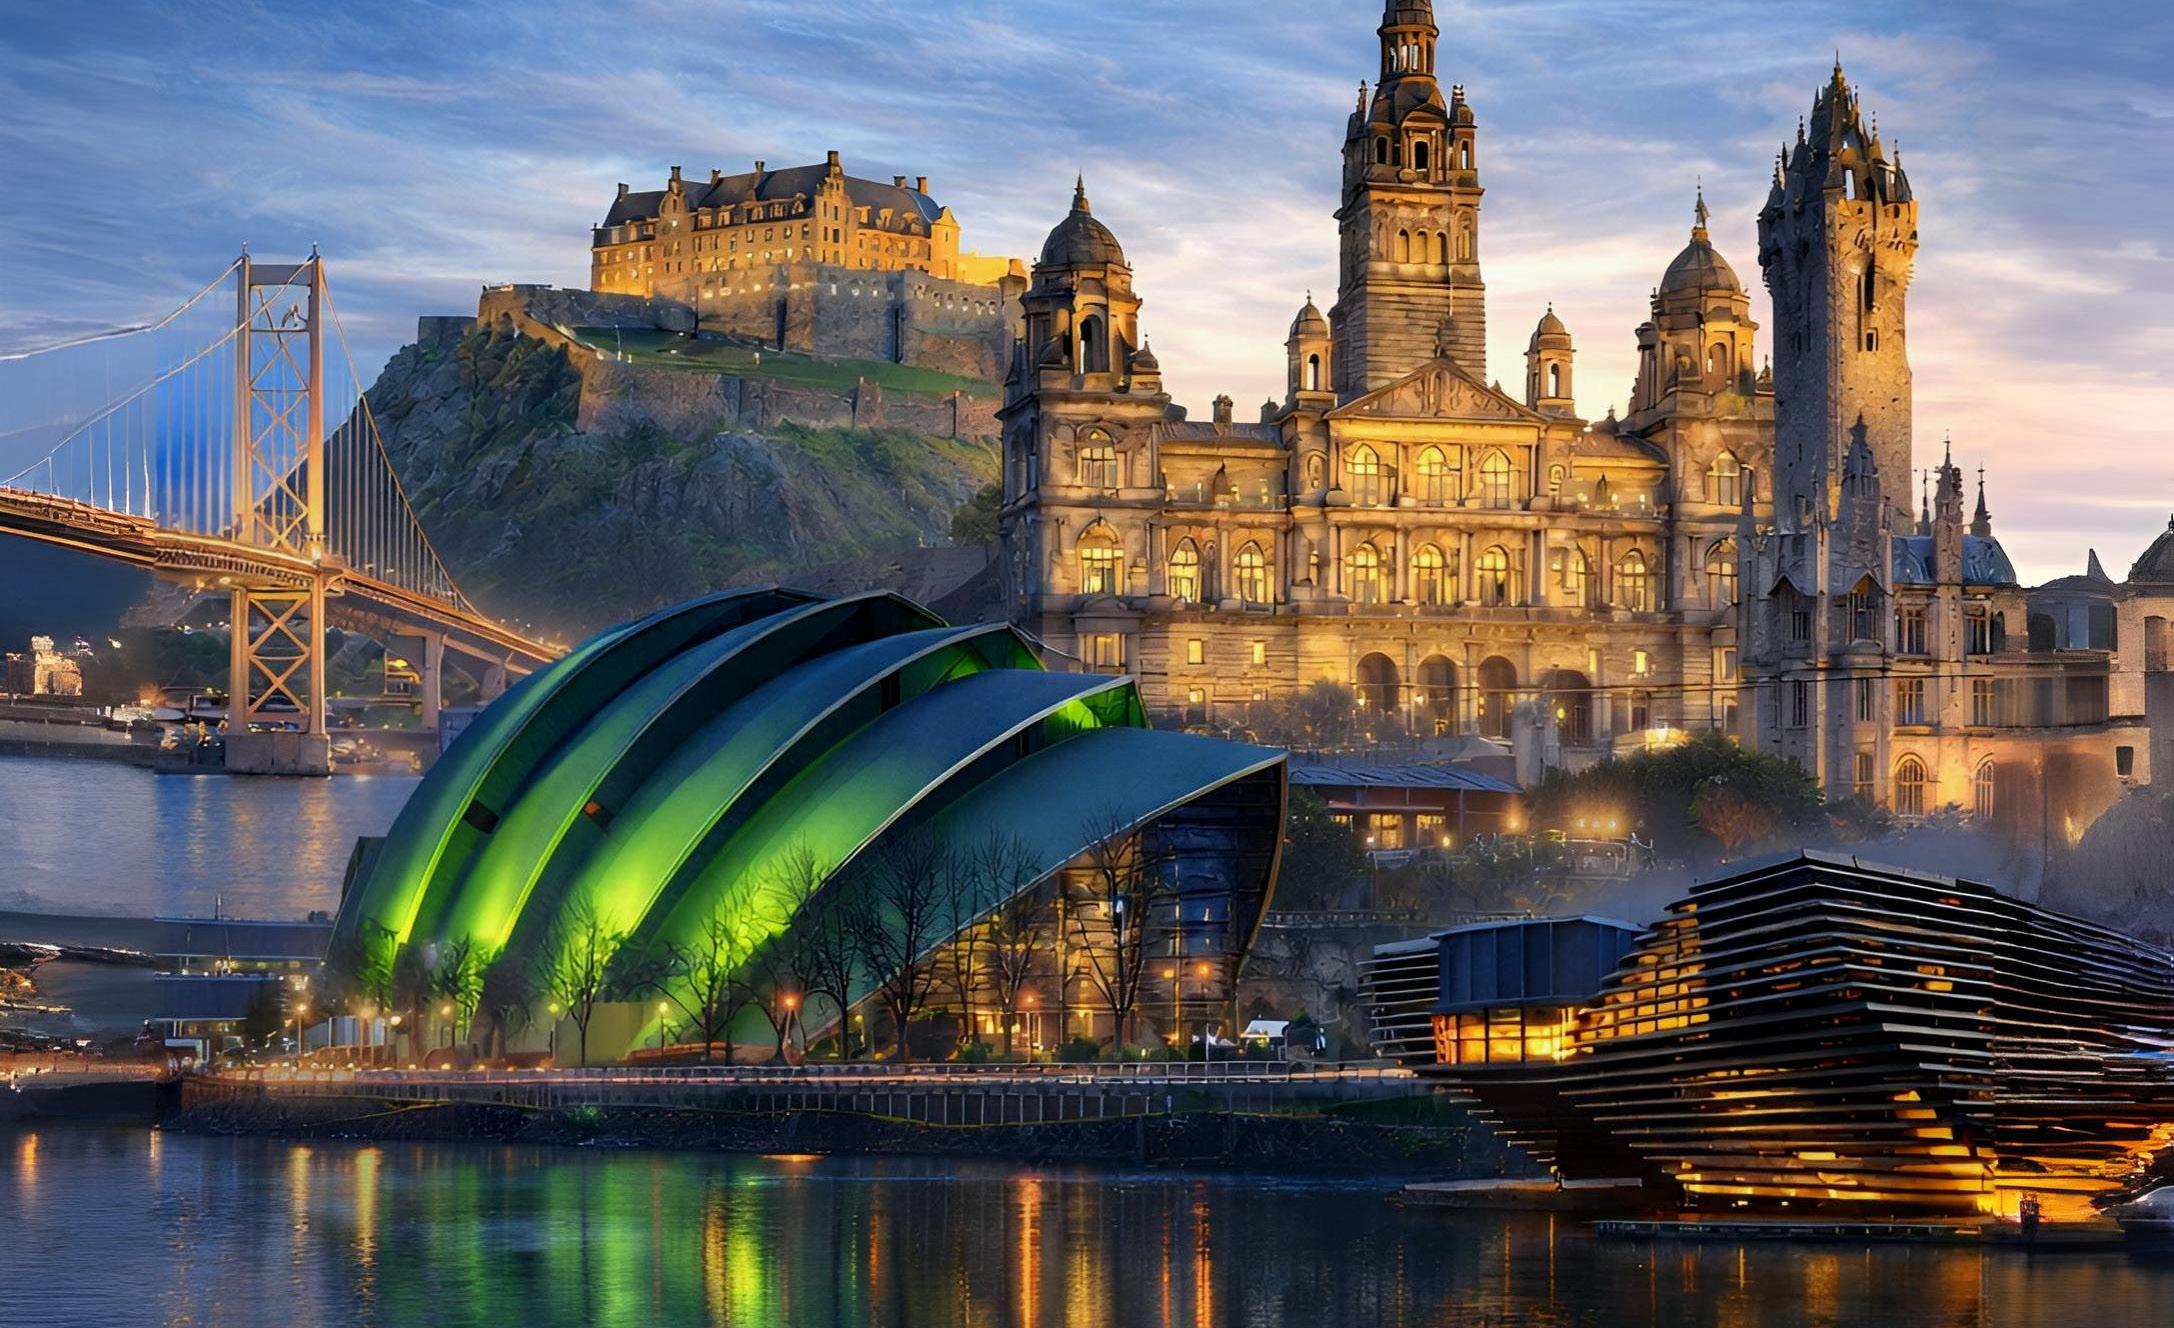
As we head to our 20th edition of Cyber News Global, we will be attending the NCSC National show case event CyberUK 2026 in Glasgow Scotland for the first time. National Cyber Resilience, Ai Governance, Global cyber threats are just a small amount of the many topics that will be discussed over the 2-day event. With this focus comes great opportunity to collaborate where capability is required, CyberUk will provide huge opportunities for the many companies attending and will also present amazing capabilities to the thousands of visitors looking to expand their knowledge and access to expertise.
Global experts will come together to share knowledge, capability, and experiences to help shape the future of Cyber Security and the advancements of Ai and Quantum.
Cyber News Global will be there to capture every opportunity that will be presented, we will meet the experts, hear their views, and share their ideas, this is the start of something truly extraordinary, we have the entire UK Cyber ecosystem to thank for such events as CyberUK, truly a world leading event.
With the advancements in Ai and its use being embraced so widely, it’s no surprise that Ai Governance has become a critical process to ensure that everyone understands their responsibility when utilising Ai to expand their capability. We will feature a special review of Scotland’s Ai Strategy, try to understand what is at stake for every single person and company now deploying Ai in their every day working life.
Quantum computing plans to revolutionise industry like never before, with that in mind CNG has yet another excellent Quantum focused article explain the challenges now facing every sector.
So dear readers, don’t lose sleep, know that there is an army of cyber and Ai warriors out there looking at the future.
Why Cyber Resilience Matters to Government: The Scottish Perspective
The Role of the National Cyber Resilience Advisory Board
I chair the National Cyber Resilience Advisory Board (NCRAB), a body comprised of leaders and influencers drawn from the public, private, and third sectors. Our primary objective is to offer strategic advice, constructive challenge, and ongoing support to Scottish Ministers, the Scottish Government, and other national delivery organisations. This collective effort aims to realise the vision outlined in the Strategic Framework for a Cyber Resilient Scotland 2025 - 2030.
The Importance of Cyber Resilience
Cyber resilience is a concern that touches every aspect of daily life. In today’s digital landscape, individuals and organisations alike are connected through websites, applications, systems, data, and essential services. Increasingly, much of our day is spent online—shopping, banking, managing prescriptions with our GP practices, gaming with friends and strangers, and connecting with others through shared interests. We entrust personal information to companies and government bodies delivering vital public services, often without considering where this data may end up or how it could be used.
Chair, National Cyber Resilience Advisory Board
While Terms and Conditions of Use exist, the majority of people overlook them. Although we benefit from this digital access, it is crucial to ensure these platforms are safe and secure to use and that we understand the risks associated with them.
Cyber threats are escalating at an unprecedented pace and are frequently highlighted in the media. The UK’s National Cyber Security Centre (NCSC) reports increasing frequency and sophistication of hostile cyber activity across the UK. High profile cyber attacks are not outliers but are a growing norm and this is not only about dramatic ransomware headlines although such attacks on retailers, the NHS and others can cause significant detriment both for thencompanies and for individuals and communities.
Data for 2024 shows that nearly half of UK businesses suffered a cyber attack or security breach. Our core message for Scotland is “Online security starts with you. ” This extends from individual behaviour to Board level and government accountability. We know that we need to be proactive because this is not just a “technical issue”; it is a national imperative.
Ministers across the UK have urged Boards to strengthen oversight of cyber Robust incident response plans must be established, regularly tested with board members actively involved, and staff at all levels should be equipped to understand and manage related risks.
Scotland’s Strategic Framework for Cyber Resilience
In November 2025, Scotland unveiled the refreshed Strategic Framework for a Cyber Resilient Scotland. This five-year strategy, spanning from 2025 to 2030, builds upon the strong cyber resilience ecosystem established in the previous strategy. Cyber resilience is not solely about reacting to threats; it involves embedding strength, confidence, and continuity throughout every part of an organisation. Crucially, it is as much about people—their awareness, skills, and capacity to respond effectively— as it is about technology itself. By prioritising cyber resilience, we move from a posture of fear to one of preparedness, and from perceiving risk as a challenge to embracing it as an opportunity.
Collaboration at the Core
Collaboration underpins our strategic approach, recognising that no government can tackle contemporary cyber challenges in isolation.
Maggie Titmuss MBE
Scotland is no exception to this principle. Our approach is built on strong partnerships across sectors, reinforcing that collective effort is critical to safeguard our people and unlock the economic potential of our secure digital future. Cyber resilience is more than a safeguard – it’s the foundation of a bold, modern digital nation. By embedding it into everything we do, we not only protect ourselves but also unlock new possibilities for innovation, progress and a more secure, inclusive future for all of us.
Strategic Priorities to 2030 and Delivery
Our focus leading up to 2030 includes:
• Strengthening national coordination
• Fostering partnership working
• Addressing risks from emerging technologies
• Guiding action across sectors
We have a comprehensive action plan which sits under the strategy which will deliver the priorities set out in the Strategic Framework for a Cyber Resilient Scotland. There are six key outcomes which are underpinned by an inclusive, whole of society approach. Effective communication and optimal use of data will help evidence the impact of our interventions. The document is a living strategy and as such we anticipate change and we continue collaborative partnerships to understand emerging threats and opportunities.
1. People recognise the cyber risks and are well prepared to manage them, Building Cyber Awareness and Education
We will work with partners to continue to reach more people in Scotland and enhance public understanding of cyber risks and best practice through targeted campaigns, educational initiatives and community outreach. Our goal is that every person is supported with the knowledge, skills and tools needed to navigate the digital world securely.
2. Ensuring our national incident response is effective.
We will continuously improve our national cyber security response, through the Scottish Cyber Coordination Centre (SC3), to ensure it is robust and effective in mitigating threats and responding to incidents
3. Scotland’s digital public services are secure and cyber resilient
We will work with national and local government to ensure our digital public services are secure and resilient by default. We will also work together to find solutions to the challenge of ensuring our legacy systems are fit for purpose andsecure.
4. Public sector organisations effectively manage their cyber risk, Strengthening Organisational Resilience
We will work closely with the public, private and third sectors to embed cyber resilience into governance structures, policies and processes.
By promoting robust cyber security standards, sharing intelligence and fostering a culture of security, we can safeguard our economy and critical infrastructure.
5. Supporting professional development
Investing in the professional development of our cyber security workforce, now and for the future, is crucial. We will work with partners to build the talent pipeline, starting from school age, expand opportunities for training and retraining, including our veterans so that our workforce remains at the forefront of innovation and expertise.
6. Strengthening collaboration and partnership
Cyber resilience is a collective effort. We will continue to build strong partnerships through the Cyber Scotland partnership and the SC3 and connect into other networks. By sharing information and best practice, we can create a united front against cyber criminals. We will also align with the UK government’s strategic work on cyber security and resilience
Conclusion
Cyber resilience now sits alongside safety, operational continuity and financial discipline as a core leadership responsibility both within government and in the other sectors. If you treat it as a peripheral concern, you are taking a gamble, not just with systems or reputation, but with revenue and long term confidence.
So, take heed of NCSC guidance for individuals and companies. Improving resilience starts with a clear baseline and Cyber Essentials, the UK Government-backed certification defines minimum protection against common attacks and gives clarity to Boards that fundamental controls are in place. It all starts with the basics.
SCOTLAND’S AI STRATEGY 2026 - 2031
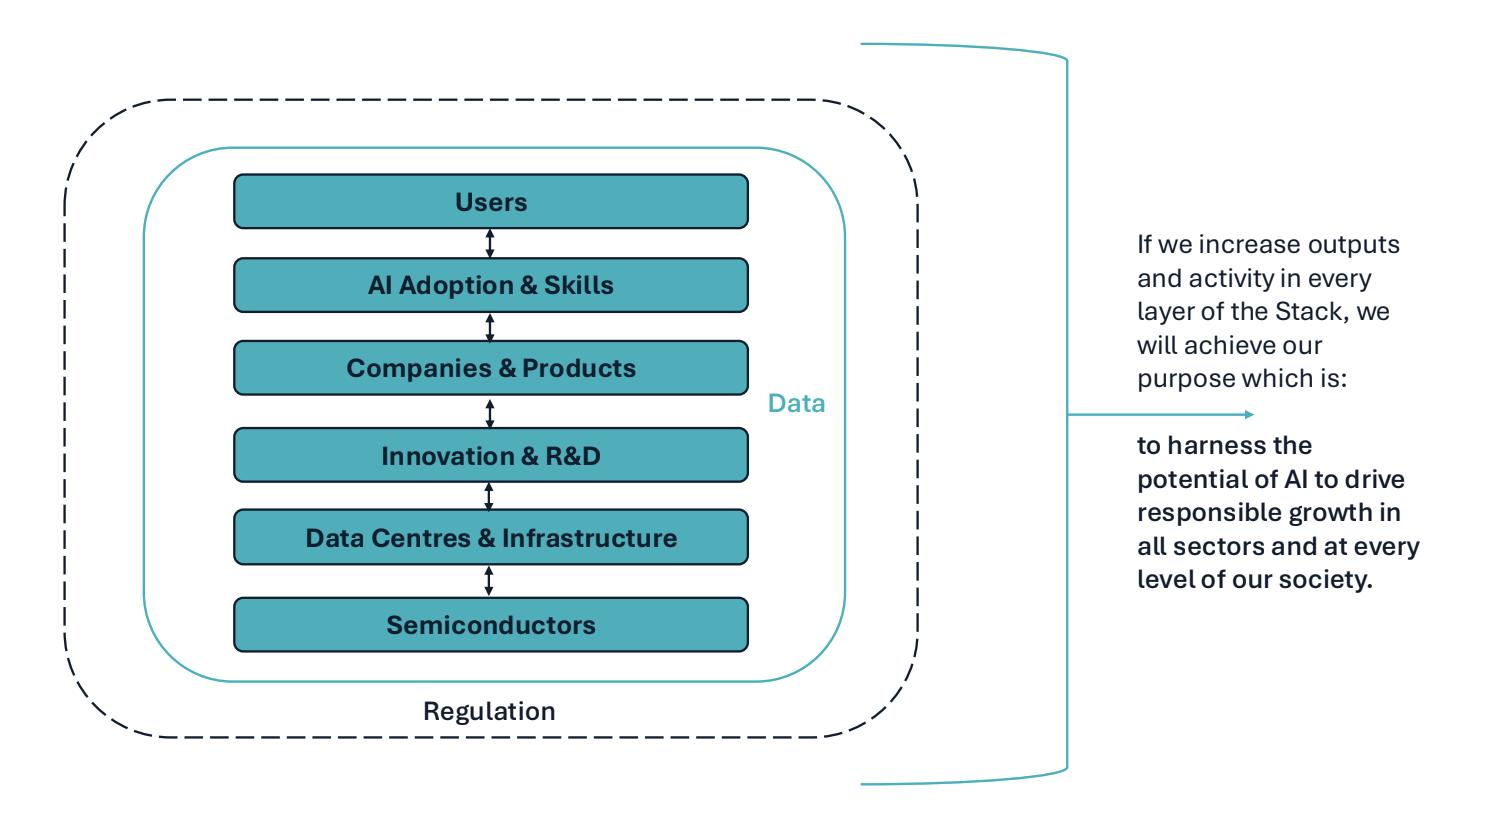
A Leadership Guide for Adopting Scotland’s National AI Strategy This executive summary details Scotland’s AI Strategy 2026-2031 into the essential considerations that leaders across business, public services and academia must understand and act upon. Scotland’s ambition is clear: to harness the potential of AI to drive responsible and inclusive growth across our economy and make a positive difference at every level of society.
Why Leaders Must Act Now
Scotland has helped to shape the modern world. For a small country on the edge of Europe, we have long been at the centre of innovation and new inventions.
We have a proud history of leading scientific and technological change and our ideas, nurtured to enlightenment by our leading universities and colleges, have revolutionised whole schools of thought leading to breakthroughs in fields as diverse as philosophy, photography and physics.
Now, Artificial Intelligence (or AI) presents an opportunity for Scotland to rekindle that pioneering spirit, to lead instead of follow and, by doing so, to harness AI’s potential for responsible, transformative economic growth. “
AI is the great disruptor, re-shaping industries through the power of machine learning – but, as Scots, we have always been comfortable on frontiers.”
Secure the benefits of AI for everyone in Scotland.
That means boosting our economy, closing the productivity gap and driving innovation while also supporting improvement to our health and education outcomes and increasing the efficiency and quality of our public services.
At the same time, we must recognise the wider risks and uncertainties that come with the rapid evolution of AI. People are rightly concerned about transparency, fairness, the impact on jobs and the accelerating pace of change.
Scotland’s response is to address these issues openly and responsibly, demonstrating that progress and safeguards can go hand in hand. Above all, our approach to AI must be firmly rooted in our values and guided by the Scottish Government’s commitment to Fair Work.
Scotland’s Unique AI Strengths: What Leaders Must Leverage
Leaders adopting this strategy must understand the exceptional foundations Scotland already possesses. These are not aspirational for they are live, competitive assets that underpin the entire strategy.
World-Leading AI Pioneers
Scotland’s long association with visionary leaders in AI from Geoffrey Hinton (Nobel Prize, 2024) to Amanda Askell (co-author of GPT3) demonstrates the strength of our academic and research institutions and their ability to attract the finest minds.
World-Leading AI Research
Five Scottish universities were placed in the UK’s top 30 for AI research output in 2025. Edinburgh hosts ARCHER2, the UK’s national supercomputer, and will host the new £750 million UK National Supercomputing Centre. The National Robotarium at Heriot-Watt is driving breakthroughs in medical and offshore robotics.
Renewable Energy Advantage
In 2024 alone, Scotland produced 38.4 TWh of renewable electricity the highest annual total ever recorded, a 13.2% increase on the year before. There is 26.4 GW of new renewable capacity in planning or consented pipelines, one of the largest in Europe relative to population.
Business Leadership & Investment
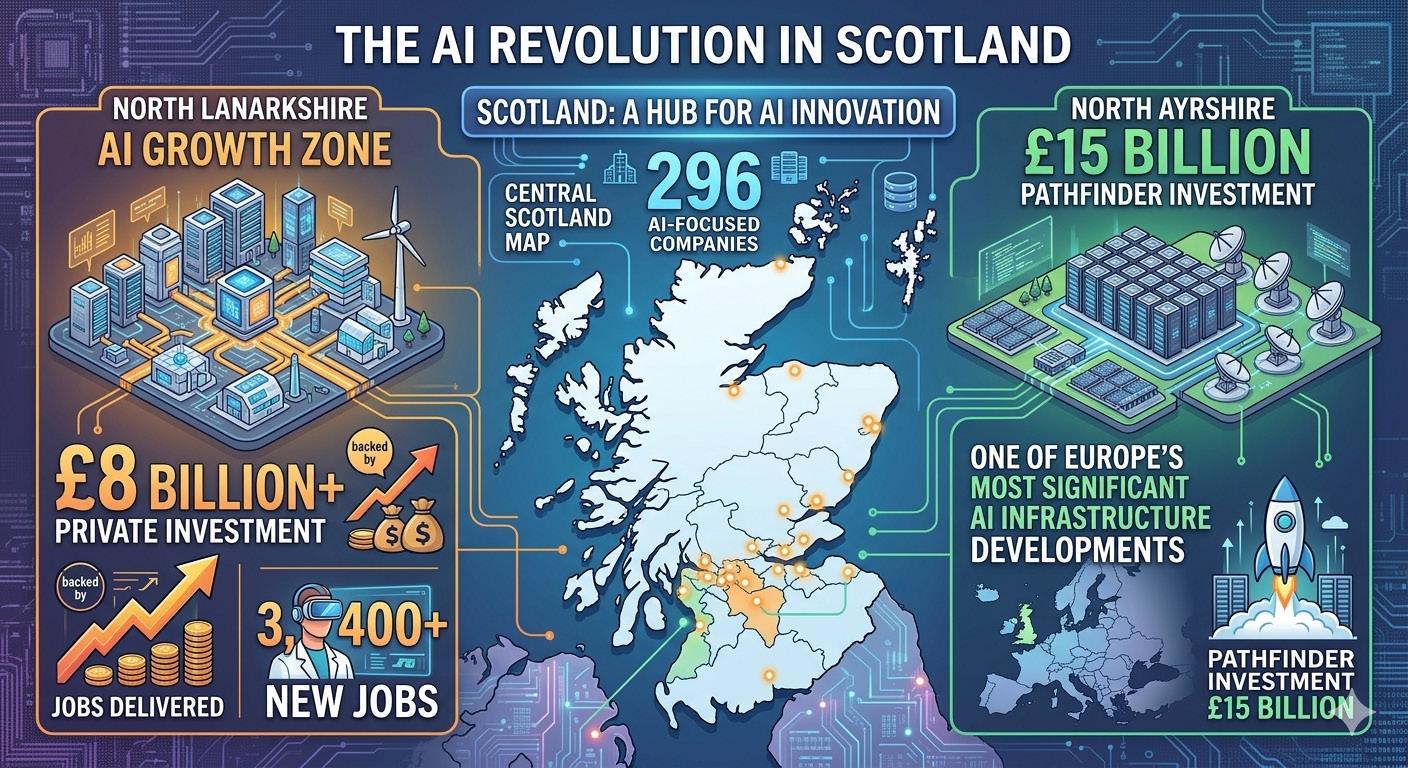
Scotland is home to an estimated 296 AI-focused companies. The first AI Growth Zone in North Lanarkshire is backed by over £8 billion of private investment and is set to deliver more than 3,400 new jobs. A £15 billion AI Pathfinder Investment in North Ayrshire will create one of Europe’s most significant AI infrastructure developments.
The Strategic Imperative: Why Leaders Cannot Wait.
Artificial intelligence is advancing rapidly and offers enormous economic potential. Leaders must internalise the urgency of this moment.
Economic Opportunity Rapid developments in agentic and autonomous AI show how quickly new capabilities are emerging. Adoption remains uneven and Scotland must act to close the gap.
Public Services Pressure
Demand for public services is rising amid tightening public finances. AI has already shown promise in enabling preventative approaches, improving planning, reducing costs and supporting frontline decision-making.
Data Governance
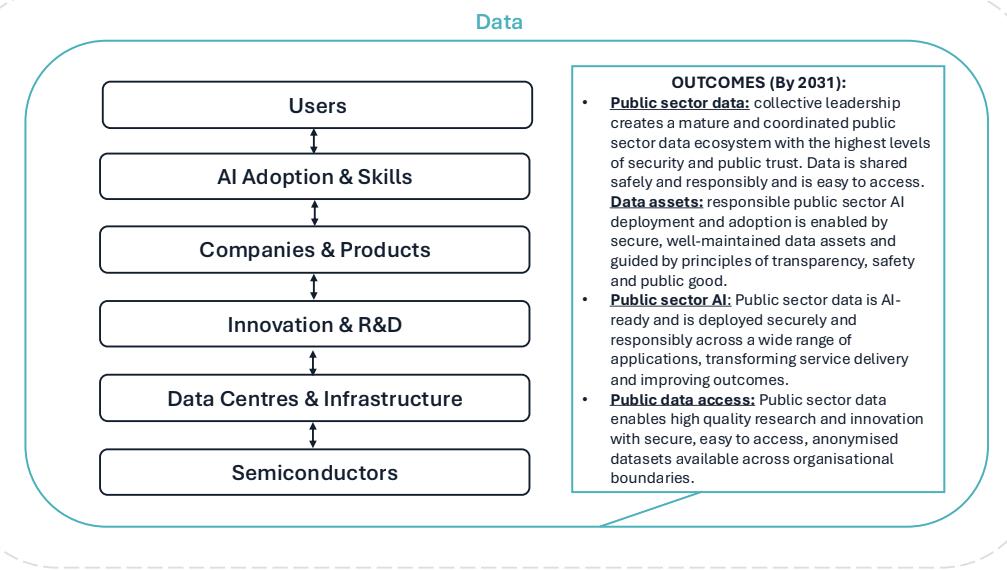
Scotland’s public sector data is often fragmented and difficult to access. Improving data sharing and governance is essential to support safer, more effective services and research.
Global Competition
A worldwide innovation race is underway. Emerging international standards including the OECD AI principles and the EU AI Act are shaping expectations of fairness, transparency and safety.
Scotland must act now to ensure that AI is introduced in ways that are safe, fair and focused on public benefit. This Strategy sets out how Scotland will do this, harnessing the potential of responsible AI to improve outcomes across our economy and at every level in our society.
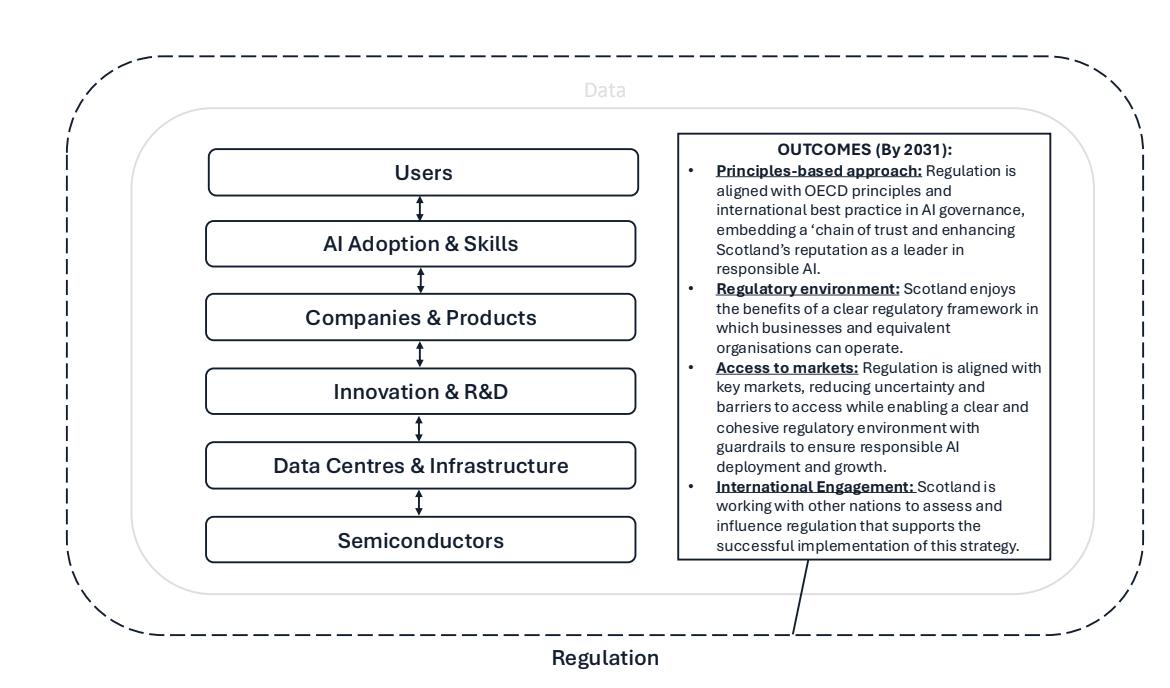
The Four Outcomes Leaders Must Deliver By 2031
The Scottish Government has defined a clear and ambitious purpose for this Strategy: to harness the potential of AI to drive responsible and inclusive growth across our economy and make a positive difference at every level of society. Leaders must orient their organisations around four outcome areas.
The Art of Resilience: Navigating the Complexity of CNI Resilience
Jane Wright Research Engineer,Strathclyde University
Modern infrastructure demands strategic foresight, not reactive defense.
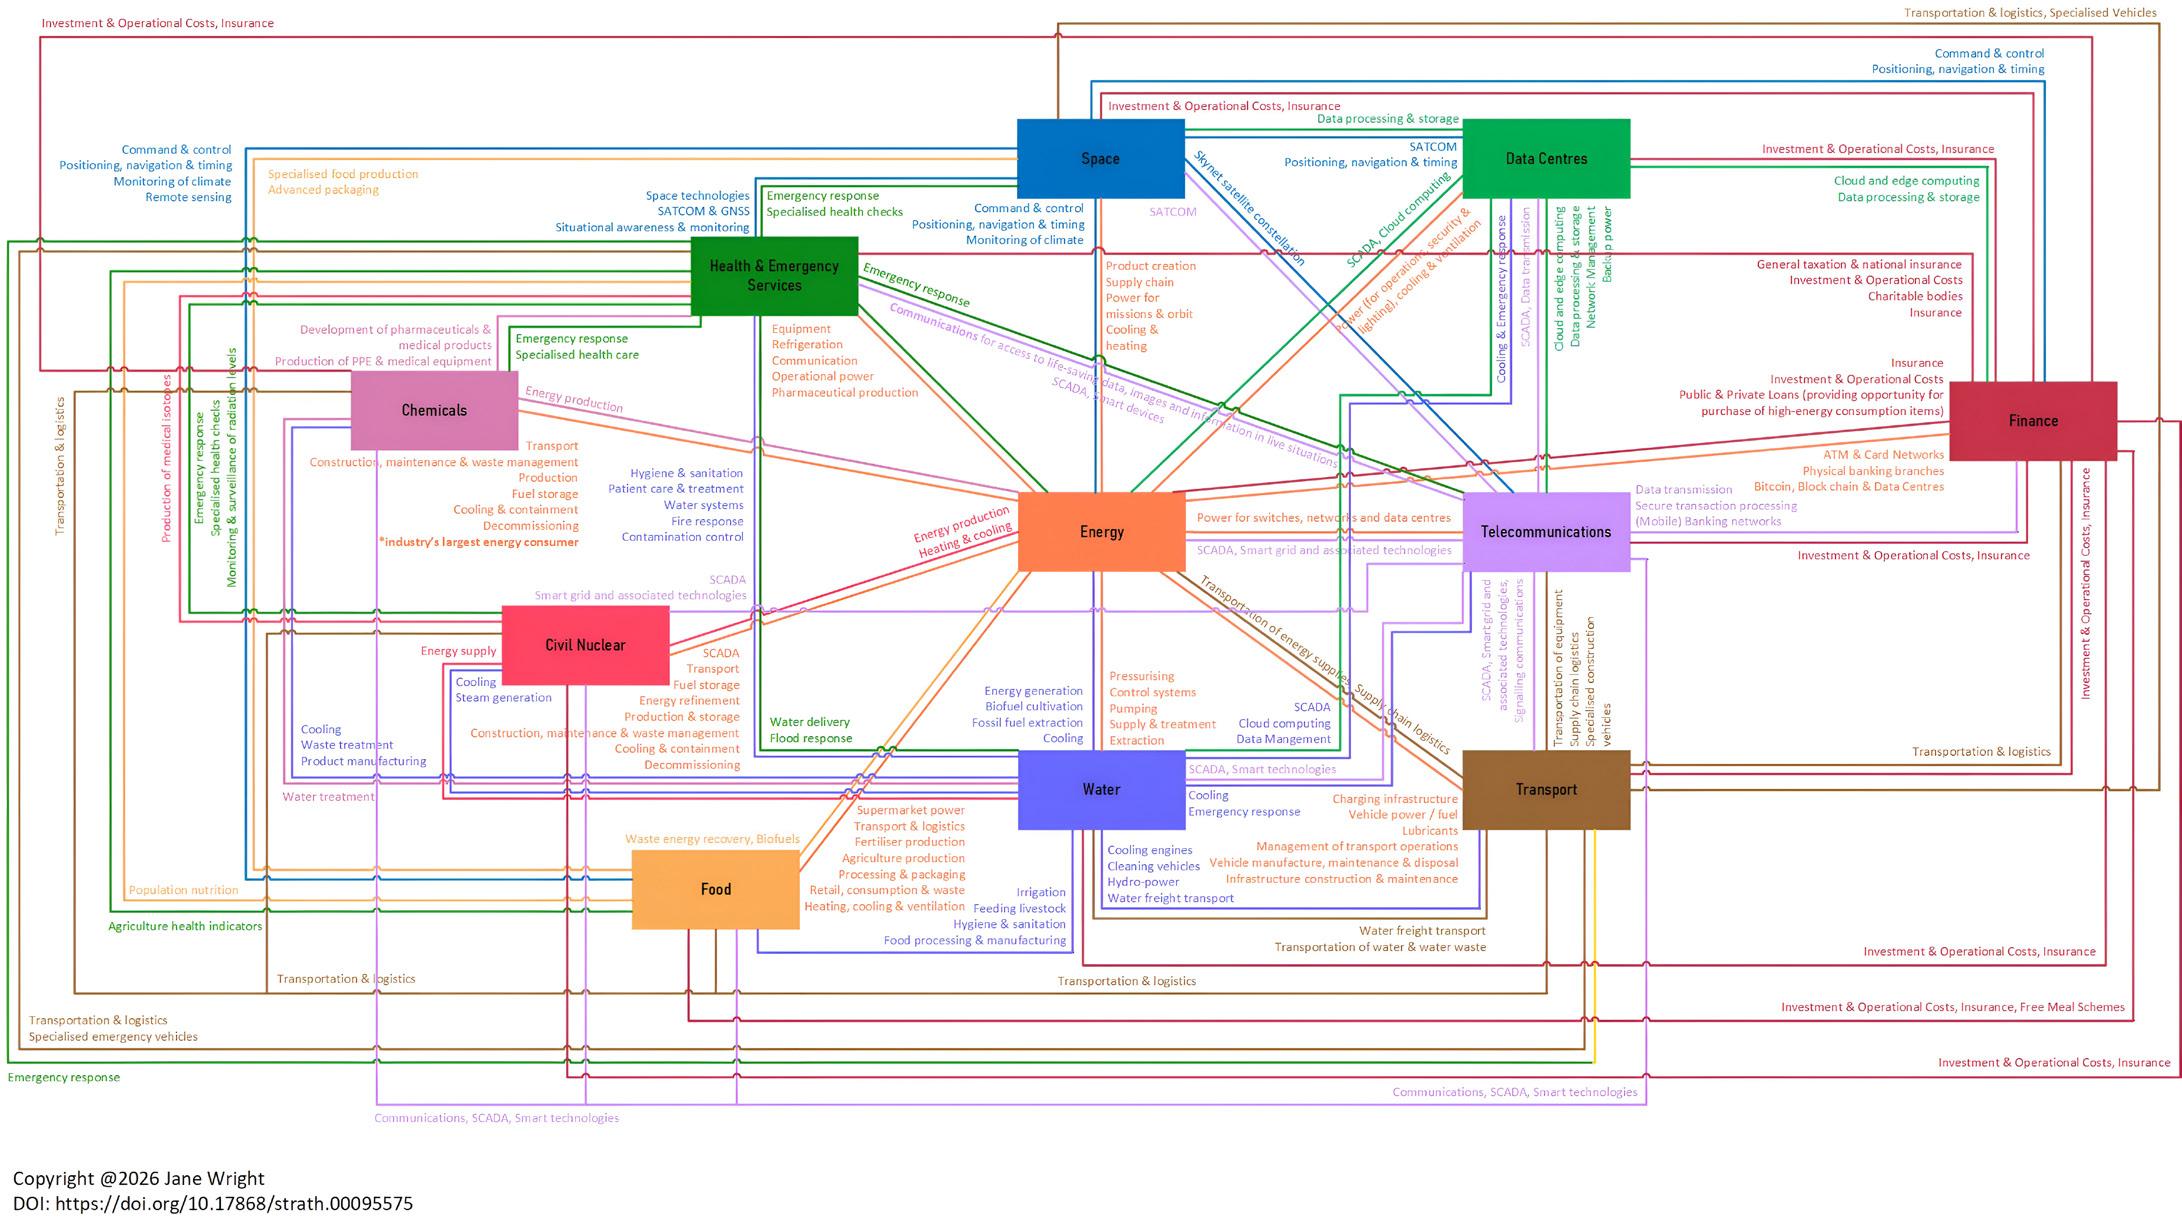
Critical National Infrastructure (CNI) systems have evolved – and continue to evolve – to keep pace with the changing environment in which they operate.
CNI is no longer limited to physical assets but also depends on digital layers, human behaviour and interactions between other infrastructure systems.
The growing scale of interdependency amplifies operational risk, as the entire network of connections becomes increasingly susceptible to disruption. As such, the concept of resilience has become a central focus for all.
Defining Resilience
Resilience is a broad, polysemous word. It is associated with concepts such as risk, response, absorption, capacity, anti-fragility, adaptability and recovery.
Each of these terms carry a distinct meaning and call for different assessment approaches. However, resilience is frequently left undefined, its meaning is not consistently articulated nor shared across individuals, teams and organisations.
This conceptual ambiguity can lead to inconsistencies in both interpretation and measurement. Consequently, interventions addressing lack of resilience may overlook the root causes of systems vulnerability.
The first step towards building resilience is defining resilience for the people, systems, businesses and organisations within the context of the environment. By developing a clearer understanding internally, organisations can engage more effectively with customers, supply chain partners and regulators. Even if stakeholders are not fully aligned, this shared awareness provides a foundation for open discussion.
Standards and Frameworks
Organisations can leverage resilience frameworks and standards to guide and support the development and implementation of resilience. Notable examples include British Standard (BS) 67000 City Resilience, BSI ISO 37123 Indicators for Resilient Cities, ISO 22366 Framework and Principles for Energy Resilience and the upcoming ISO/DIS 22316 Organisational resilience.
Frameworks aimed at resilience within a cyber security context include the European Union Directive on Security of Network and Information Systems (NIS2 Directive), NIST SP 800-160 Developing Cyber Resilient Systems and the NCSC’s Cyber Assessment Framework.
Organisations have also implemented business continuity, crisis and risk management frameworks and standards with the same aim. These frameworks are in addition to technical engineering standards; another dimension of complexity for organisations.
A significant challenge lies in (i) selecting appropriate standards and frameworks, (ii) understanding which are mandated for regulatory compliance or international collaboration, and (iii) evaluating the extent to which they can be integrated effectively, without generating contradictory specifications.
For example, consider the tension between security and resilience. Security specifications primarily focus on confidentiality, integrity and availability, emphasising robust systems and strict controls. In contrast, resilience engineering promotes flexibility, adaptability and extensibility. This raises the question of whether the rigid security structures may conflict with, or even limit, the adaptive capacities encouraged by resiliencefocused approaches.
The Art of Resilience: Navigating the Complexity of CNI
Resilience (Contd:)
Resilience assessment should go beyond generating risk scores or rankings; it must deepen understanding of system dynamics, uncertainties, and the complex challenges that require further exploration.
Many of these frameworks and standards provide well-established theoretical principles and systematic methods for evaluating systems holistically. Applying these frameworks to CNI is complicated by the fact that oversight and influence are exercised by third-party regulatory authorities. This constrains organisational decision-making autonomy such that these conceptual principles have to be operationalised through measurable indicators and outputs. Organisations are incentivised to pursue a ‘good enough’ level of performance, oriented toward meeting the measurable criteria established by the regulatory authority rather than fully realising the underlying principles of resilience.
By reducing resilience to a specific set of measurable metrics, interdependencies, relationships and the influence of uncontrollable external factors are often overlooked. This produces imperfect information, thus limiting the accuracy and usefulness of resilience assessments.
It is recommended that organisations consider their system as part of an interconnected whole, and anticipate and account for the factors considered above.
In doing so, they can avoid becoming overly self-referential and ensure that resilience strategies reflect the broader context in which their system operates.
Considering the Cost of Resilience
Consideration of cost is essential when developing a resilience strategy. Without an understanding of cost, it becomes impossible for organisations to assess effectively which goods and services can be delivered, to what extent, and over what duration. However, the cost of cultivating resilience presents a significant challenge. Unlike traditional investments, where returns can be quantified through revenue or profit, resilience initiatives often do not generate immediately visible financial benefits.
Consequently, securing ongoing funding for resilience measures, much like cyber security, can be difficult, as the value is realised through the avoidance of adverse outcomes – counterfactual scenarios that are inherently difficult to observe and communicate. Monitoring and evaluation systems can provide some metrics as to impact, but effects of resilience-building measures are not always apparent or directly attributable.
Because resilience-related investment is frequently marginalised for firms focused on sustaining a low-profit equilibrium and regulators incentivised to minimise costs for consumers, organisations are forced to adopt a risk-focused approach to resilience. Risk management methodologies focus on spending time, resource and effort in loss avoidance through restricting activities. However, an emphasis on loss avoidance can suppress adaptive initiatives, even when such actions align with the same goal.
Events seldom unfold exactly as anticipated. Organisations must develop the capacity to operate effectively under uncertainty and to tolerate ambiguity as an inherent feature of complex environments.
Given the estimated cost of downtime, expenditure on resilience efforts should effectively pay for itself within a number of years, irrespective of whether a major incident materialises.
Approaching Resilience
Defining and quantifying resilience is inherently complex, and traditional risk assessments alone are clearly insufficient.
Some elements, while inherently immeasurable, are essential to organisational success and system resilience. Thus, organisations must adopt broader approaches that emphasise adaptability, learning and responsiveness to unforeseen challenges.
1. Establish a Minimum Viable Company
Acknowledging that all systems carry some degree of vulnerability, organisations need to identify and prioritise those that are essential to fulfilling their core mission. This includes determining which suppliers, logistics partners and distribution channels are indispensable for sustaining minimum service levels and maintaining cash flow. With this understanding, protective measures can be layered around those priority systems. Mapping these interconnections facilitates a more holistic assessment of the organisational environment and points of potential opportunity and vulnerability.
2. Incremental Advancement
The system should be advanced incrementally toward these objectives through a series of viable, stable intermediate states. Rather than relying on a single, large-scale investment, that may not be economically viable, these stages provide fundable opportunities for progress along alternative pathways and allow for rollbacks if necessary. Implementation must be guided by a prioritisation framework that is regularly reviewed. The approach requires striking a balance: taking sufficient risk to enable meaningful change, while avoiding exposure that the organisation cannot absorb.
3. Celebrating Failure
Organisations need to foster a culture that recognises and learns from failure, while maintaining accountability for negligence. Studies on innovation indicate that failed projects often generate new organisational knowledge and insights that help firms refine their approaches and avoid repeating the same mistakes. By shifting decision-making practices and valuing employees’ contributions in the face of failure, organisations can stimulate greater innovation and learning, generating organisational and economic growth.
Implications of Artificial Intelligence (AI) and Machine Learning (ML)
AI creates both opportunities and risks. Digitalisation has exponentially increased the volume of data produced, collected, stored and shared between systems. Harnessing AI and ML within CNI can help manage this complexity, enabling faster decision-making. It has the capacity to identify patterns or insights that humans might overlook and can accelerate and streamline many cognitive processes. The potential for greater efficiency and scalability offers a significant advantage for the resilience of CNI. However, CNI systems are highly complex and often proprietary. This makes it difficult to gather real-world data for training purposes, raises significant concerns around transparency and accountability, and introduces new vulnerabilities to the system. It is essential to remain cognisant of where and how AI is deployed within CNI, who is using it, and how its integration alters system interactions.
A refreshed approach to resilience is necessary. The goal of resilience assessment extends beyond producing risk scores, rankings or exact values. More critically, it should enhance the assessors understanding of the underlying problem, associated dynamics, inherent uncertainties and areas that require further exploration or research. In this way, assessment becomes a tool for learning and reflection, not just measurement.
The desire for complete control must be relinquished, and the inherent complexity of systems must be acknowledged. It is essential to recognise that operational, policy and regulatory decisions exert significant influence and unintended consequences on systems beyond their immediate boundaries.
Email: jane.wright@strath.ac.uk
SCAN
Leading in Uncertainty: Cyber Resilience Leadership
RICHARD PREECE
In cyber security, leadership has always mattered. Now it matters differently. In a world shaped by geopolitical tension, technological acceleration and deep interdependence, the real challenge is no longer just protection. It is adaptation.
Cyber security has always been a leadership challenge disguised as a technical one. That is even more obvious now.
We are operating in a world defined by overlapping pressures: geopolitical competition, economic strain, technological disruption, threatened physical and digital supply chains and growing social distrust. In that environment, cyber risk cannot be treated as a standalone technical issue. It sits inside a much broader system of dependencies and vulnerabilities.
That changes the job of leadership
The old model was built for a more stable world. Leaders were expected to assess the landscape, set direction, assign responsibilities and drive execution through relatively clear structures. Now the situation has changed, it is no longer enough. In conditions of persistent uncertainty at the technical, operational and strategic levels, leadership cannot just be about setting a plan and holding the line. It must be about sensing change, interpreting what matters and adapting in time.
That may be uncomfortable for some organisations and individuals, because it forces a conversation about what leadership is and how it needs to evolve.
At its core, leadership is about personal power: the ability to win the hearts and minds of others in pursuit of a common purpose. In practice, that means aligning people, often under pressure, cutting through friction and confusion. Ultimately helping organisations move forward when the facts are incomplete and the situation is changing. Cybersecurity and technology professionals are in many ways at the centre of this; it is the job!
Uncertainty is no longer temporary
There is a temptation to treat uncertainty as a passing phase, something to be endured until conditions settle down. That is wishful thinking.
We are living through a structural shift. The assumptions that shaped the post-Cold War era are under strain. Strategic competition is reshaping trade, investment and supply chains. AI is moving fast and quantum computing is just around the corner! Digital dependency is deepening and the boundary between physical and digital infrastructure is becoming harder to separate. Energy systems, water, communications networks, cloud services, semiconductors and data infrastructure supply chains are now tightly entangled.
That matters because cyberspace does not operate in isolation from any of it, it cuts across it all!
Take AI. It is often discussed as though it exists purely in software; it is not. It depends on data centres, power generation, cooling, telecommunications, advanced chips and scarce technical talent. So, the cyber question is not just about securing models or data. It is also about resilience in energy, supply chains, infrastructure and geopolitics. Once seen through that perspective, cyber resilience leadership looks less like a specialist technical function and more like a key contributor to strategy and operations.
That is where many organisations still fall short. They continue to treat cyber as a technical or compliance issue rather than as part of a wider system of organisational resilience. That is neat for org charts and for those used to a more stable, certain, simple and clear world! But it doesn’t reflect reality!
Chief Training Officer at OSP Cyber Academy
Why the leadership model has to evolve
A great deal of leadership culture still rests on a flawed assumption: that leaders are supposed to provide certainty. They are not.
In volatile, uncertain and complex conditions, the pretence of certainty is usually a liability. It narrows the range of views that reach senior decisionmakers, discourages challenge and makes adaptation harder when reality breaks the often-implicit assumptions and biases we all have. Leaders who act as though they already know the answer often create brittle organisations, especially in cyber where threat, technology and context can all move at once. This is a team of teams’ endeavour.
A better approach starts with intellectual honesty. Leaders need enough confidence to say what they do not know. That is not weakness. It is the basis of better feedback and judgment.
From there, the task is to create conditions in which foresight, insight and hindsight can all emerge from across the organisation. Useful signals do not arrive only through formal hierarchy. They may come from engineers, operations teams, risk specialists, frontline staff, external partners or suppliers. If an organisation only listens upwards, or only listens to the same familiar voices, it can miss what matters.
Managing by walking about is still vital, but in the age of Zoom calls, outsourcing, etc, the channels of communication maybe different!
This is not an argument for endless consultation or soft indecision. It is an argument for stronger leadership built on better inputs. Leaders still must decide. They still must take responsibility. But the quality of those decisions depends heavily on whether the organisation is structured to anticipate and surface reality rather than suppress it.
Strategy is now about adaptability
In uncertain times, perhaps the most important strategic capability now is adaptation.
That does not mean abandoning direction or becoming reactive. It means designing organisations that can anticipate, absorb and adapt. It means building flexibility into decision-making, governance, operations and crisis response. It means shortening feedback loops to detect, learn and adjust faster.
Technology teams have understood this for years. The best agile methods were built around a simple point: learning from feedback matters more than rigid planning. The mistake many organisations make is confining that principle to software delivery. The same logic applies much more widely. Leaders should be asking how to build rapid learning into operations, resilience planning, risk management and executive decisionmaking.
That is especially important in cyber resilience, where assumptions can mask vulnerabilities.
The value of scenarios
This is where scenario thinking becomes genuinely useful.
Scenarios are often misunderstood as prediction exercises. They are not. Used properly, they are a way of stress-testing assumptions against multiple severe/ extreme but plausible futures.
That matters because many organisations are built around hidden assumptions they rarely examine. Assumptions about stable suppliers, affordable energy, regulation, available skills, trusted partners or predictable escalation paths in a crisis. Scenarios force leaders to test where those assumptions break and what the consequences would be.
Many organisations have plans for what to do in a disruption or cyber incident. But these are mere arrangements, until the capability and capacity to respond and recover under severe but plausible scenarios has been tested. They may lack decision speed, operational bandwidth, technical depth, or the ability to communicate and coordinate effectively across silos.
Culture is a hard issue
If adaptation is the goal, culture matters far more than many leaders admit.
If leaders want adaptability, they need cultures where people can speak candidly, question assumptions and recover quickly from setbacks. That does not mean lowering standards. Quite the reverse. It means creating an environment where realism is valued. Otherwise, problems are often hidden, weak signals ignored and teams become less capable of clear thinking under pressure.
In uncertain conditions, silence gets filled by rumour and poor communication gets filled by cynicism and fear. People do not need false reassurance. They do need clarity about what is happening, why decisions are being made and what may need to change next. Credibility comes not from pretending to control everything, but from showing that leadership is engaging honestly with reality.
What cyber leaders need to do now
For cyber leaders, the implication is clear. Not to pretend uncertainty can be eliminated; it cannot. The point is to lead through it more effectively. The role still requires the securing of systems, assurance of compliance and respond to incidents. But increasingly to help organisations navigate an environment in which technology, business strategy and geopolitical context are all moving at once.
Be willing to challenge narrow definitions of cyber risk. Look beyond the network to the dependencies that make the organisation function. Build structures that allow information and intelligence to flow across silos. Use scenarios to test assumptions. Develop people who can apply principles (desired outcomes) to context, not just verify compliance with controls. Finally, when decisions are needed, take them with clarity and be ready to review them, when the situation changes.
That demands leaders who are more curious, humble, strategic and adaptive.
SCAN ME
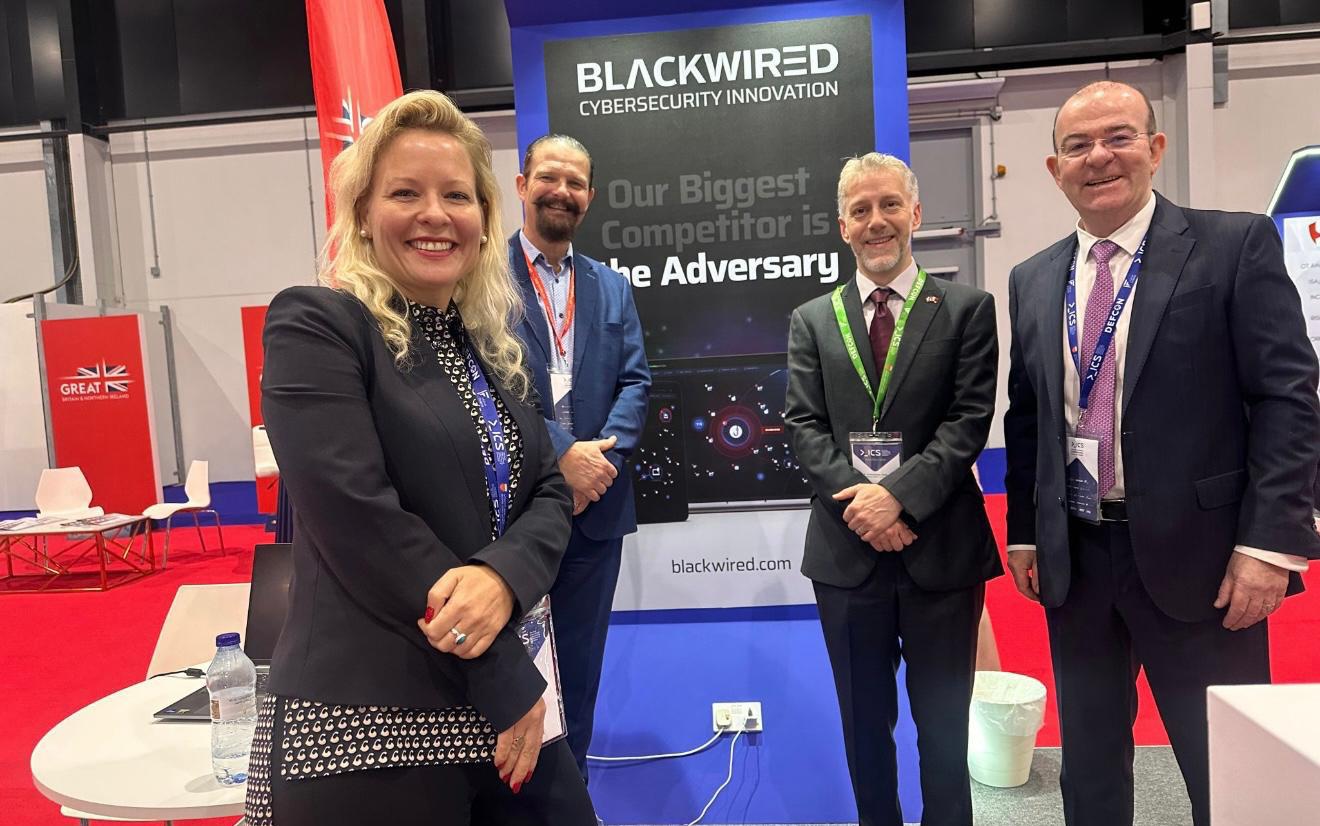
The company feeds this verified, evidencebased Direct Threat Intelligence into an organisation’s security stack via API-based orchestration, preventing cyber weapons from reaching their targets. This level of proactive defence is now essential, especially for major corporations whose ability to operate is increasingly threatened by hostile cyber activity.
ThirdWatch: A Breakthrough in Proactive Defence
ThirdWatch, Blackwired’s intelligence platform, visualises the entire adversary ecosystem in 3D - showing how different campaigns interconnect and how quickly they approach execution, including identification of zero detection malware and ransomware.
Key Differentiators
1. A vast and continuously updated cyber weapons data lake ThirdWatch includes millions of malicious artefacts collected from the surface web, deep web and dark web. Because attackers often reuse or adapt existing malware families, this historic dataset enables rapid pattern recognition and variant identification.
2. AI trained on true intelligence tradecraft The platform’s models learn adversarial behaviour—not only signatures or IOCs—allowing them to map campaigns, predict progression and understand intent.
3. Zero-day identification and deep darkweb collection Blackwired specialises in identifying malicious assets and infrastructure before they are deployed, often long before they appear in commercial threat feeds.
4. Zero-touch, external visibility The platform never requires access behind a customer’s firewall. It observes the adversary space externally, then uses an API to orchestrate intelligence into endpoints with speed and precision.
5. No false positives All intelligence is evidence-based and verified. This eliminates the costly human verification burden that overwhelms many SOC teams.
These elements combine to create Direct Threat Intelligence—intelligence derived not from compromised systems, but from observing adversaries themselves in real time.
ThirdWatch
ThirdWatch is the only cyber security platform capable of producing Direct Threat Intelligence (DTI), i.e. cyber threat insights and analysis specific to an organization at global, regional, country and organizational levels.
The Platform’s Third Party Risk Intelligence Module enables organisations to score third party and supply chain risk, based on priority and operational importance, whereas the enhanced Attack Surface Management Module (eASM) maps the direct, external threats facing an organisation to its known vulnerabilities, delivering rapid prioritisation.
Using graph technology, ThirdWatch visualises the entire adversary ecosystem in 3D—showing how different campaigns interconnect and how quickly they approach execution.
What’s Next for 2026?
Looking ahead, Ruth emphasises that 2026 will be a challenging year. Anticipated developments include:
•Greater nation-state and organised crime led cyber-attacks of critical national infrastructure
•Continued growth of ransomware and extortion models
•Escalation in deepfake-driven fraud
•Rising dependency risks in third-party and cloud ecosystems
•The emergence of “shadow AI” inside organisations
•Increased targeting of crypto, DeFi and stablecoin markets
•The growing urgency of quantum-resilient encryption
Yet Ruth also stresses that the defensive use of AI—when deployed at the right architectural level—offers a route to resilience. Understanding where attackers sit across the OSI model, and spotting malicious behaviour long before execution, will define the organisations that remain secure in the years ahead
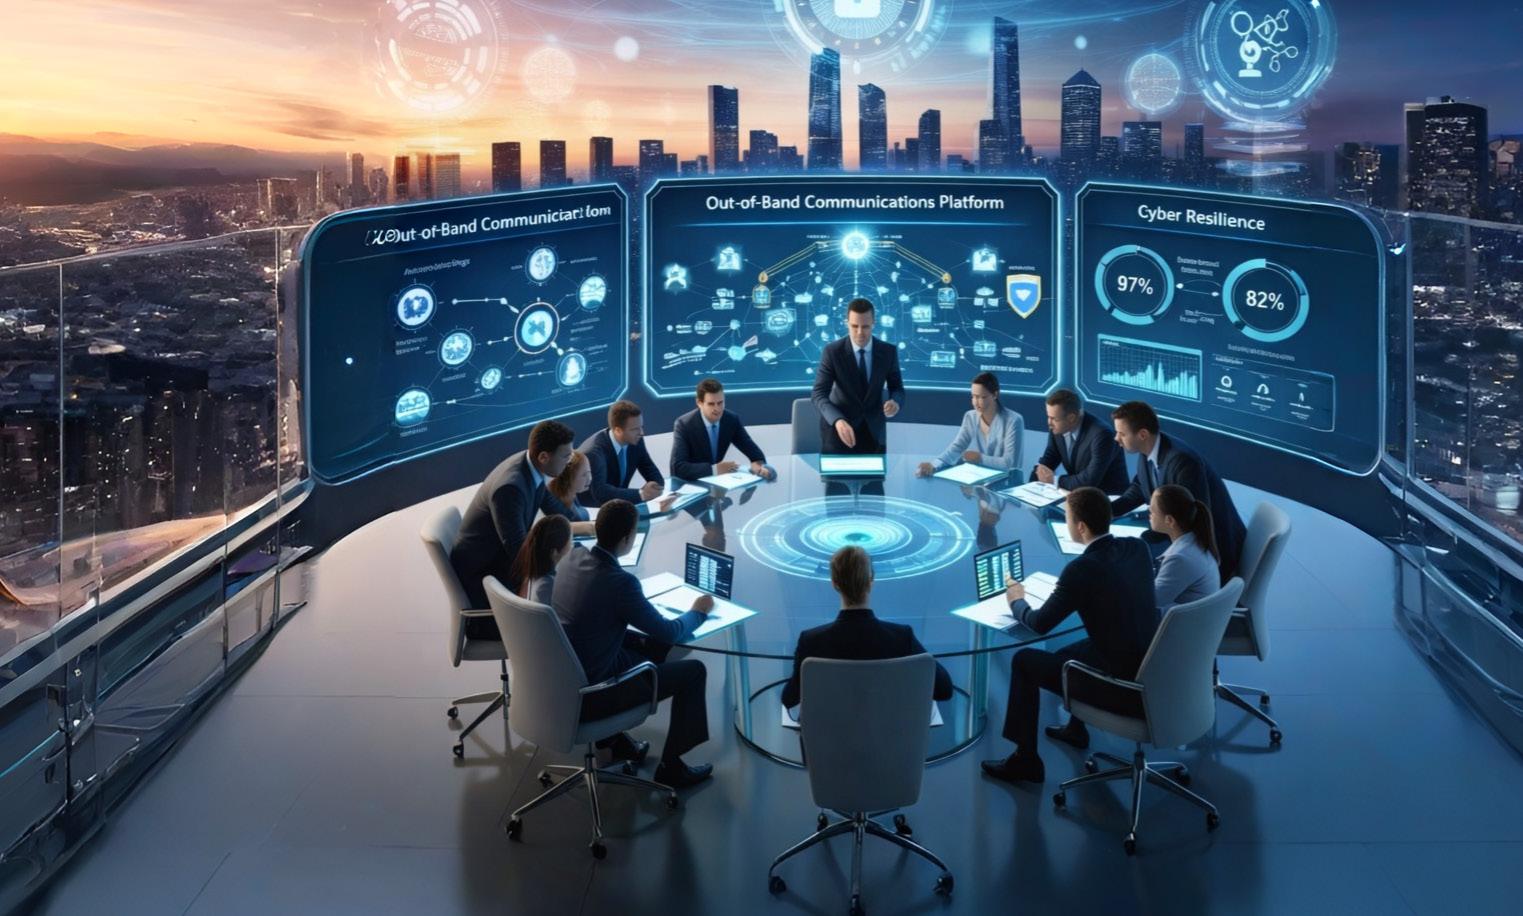
Out-of-Band Communication: The Missing Layer in Cyber Resilience
James Mullins
“When you use those same tools to manage the breach...you’re basically handing over your crown jewels to the attacker.”
There is a persistent assumption in cyber security that when systems fail, organisations will still be able to coordinate their response.
In practice, that assumption does not hold. As cyber-attacks become more sophisticated, the systems organisations depend on most, email, chat platforms, and collaboration tools, are increasingly the first to be compromised. Yet in the middle of an incident, teams continue to rely on those same channels to make decisions, share intelligence, and attempt recovery.
The result is a structural weakness in how resilience is designed. The tools intended to support coordination can quickly become part of the threat surface itself.
When communication becomes exposure
Modern attackers are not just looking to disrupt operations. They are seeking visibility.
Once inside a network, gaining access to internal communications is often straightforward. This gives attackers a real-time view of how an organisation is responding, what actions are being taken, how decisions are being made, and where the pressure points are.At that point, the dynamic of the incident changes. Response efforts are no longer private; they are observable.
This is where many organisations unintentionally make the situation worse. By continuing to use compromised communication channels, they extend the attacker’s advantage. Every message risks revealing intent. Every coordination step becomes visible.
Out-of-band communication exists to address this exact problem. It creates a separate, controlled environment where response coordination can continue without exposure. Not as a secondary convenience, but as a deliberate layer of operational design.
The first 60 minutes is a leadership problem
Where incidents tend to break down is not in tooling, but in decision-making.
In the early stages of a breach, many organisations find themselves asking basic questions:
• which communication channel should be used?
• where is the incident plan stored?
• who has authority to act?
These questions are rarely answered quickly under pressure.
The issue is not complexity. It is a lack of rehearsed governance.
“If leadership is still debating which WhatsApp group to use...you’ve already lost.”
This reflects a broader pattern. Too many organisations operate on what could be described as a “strategy of hope”, the assumption that a serious breach is unlikely, or that existing structures will hold under stress.
In reality, resilience depends on preparation that has been tested. Organisations that respond effectively are not improvising. They are executing predefined processes within environments that are ready to activate immediately.
A secure, pre-configured “war room” is therefore not an enhancement. It is a baseline requirement for maintaining control when primary systems cannot be trusted.
From communication to coordination
Out-of-band communication is often framed narrowly, as a way to maintain contact when systems go down. In practice, its role is broader. Resilient response depends not just on communication, but on coordination. That requires structure:
• access to playbooks
• clarity on escalation paths
• alignment between technical teams and leadership
• The ability to act in a way that is both efficient and accountable
Vice President of Sales for EMEA and APAC
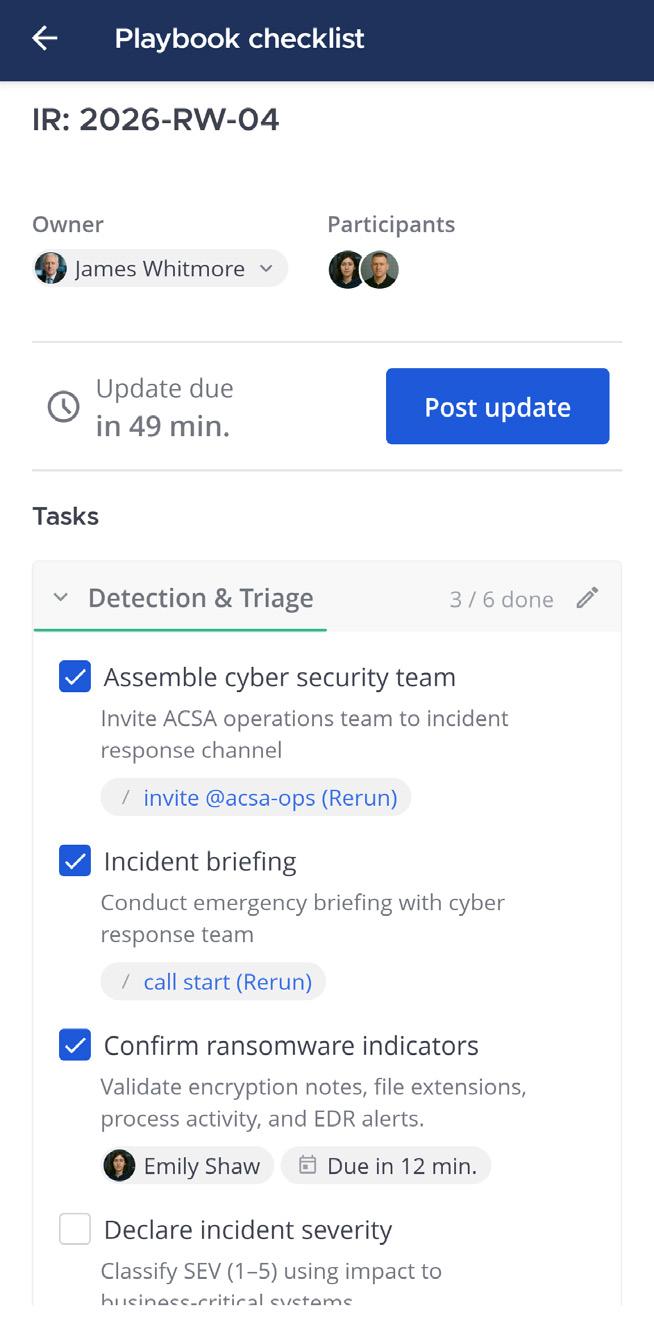
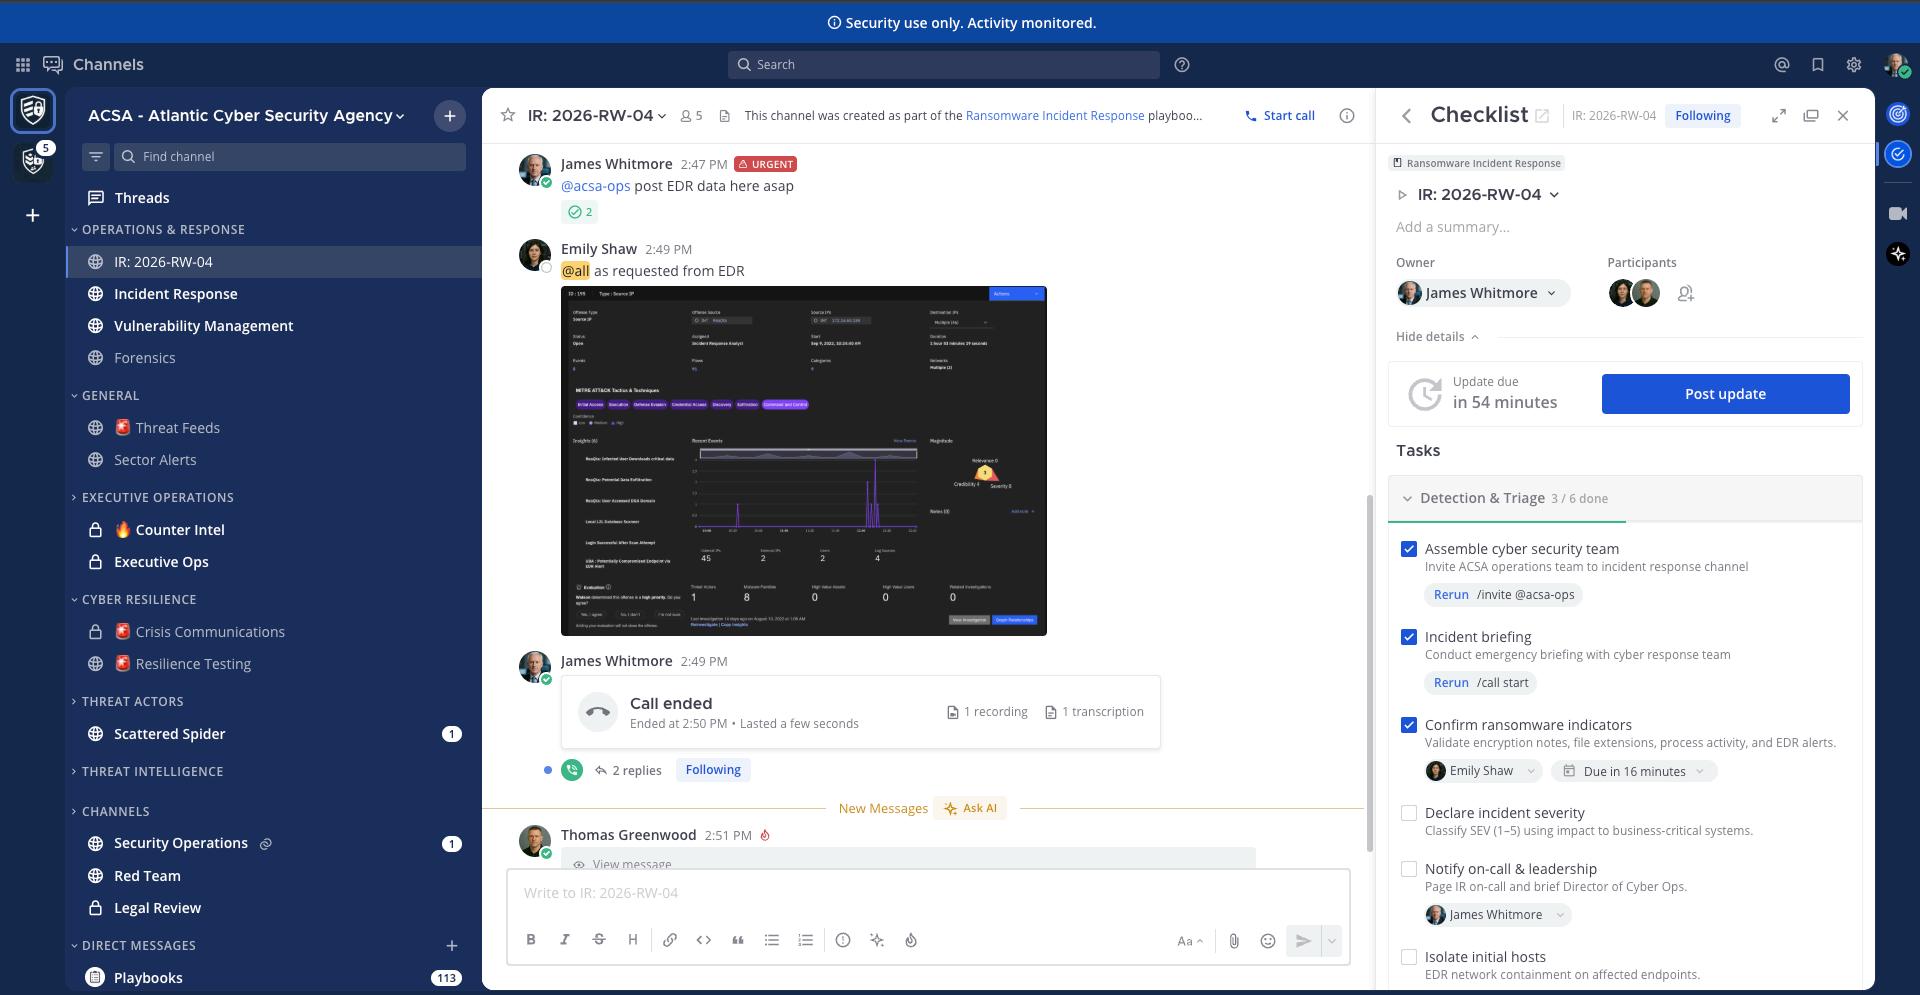
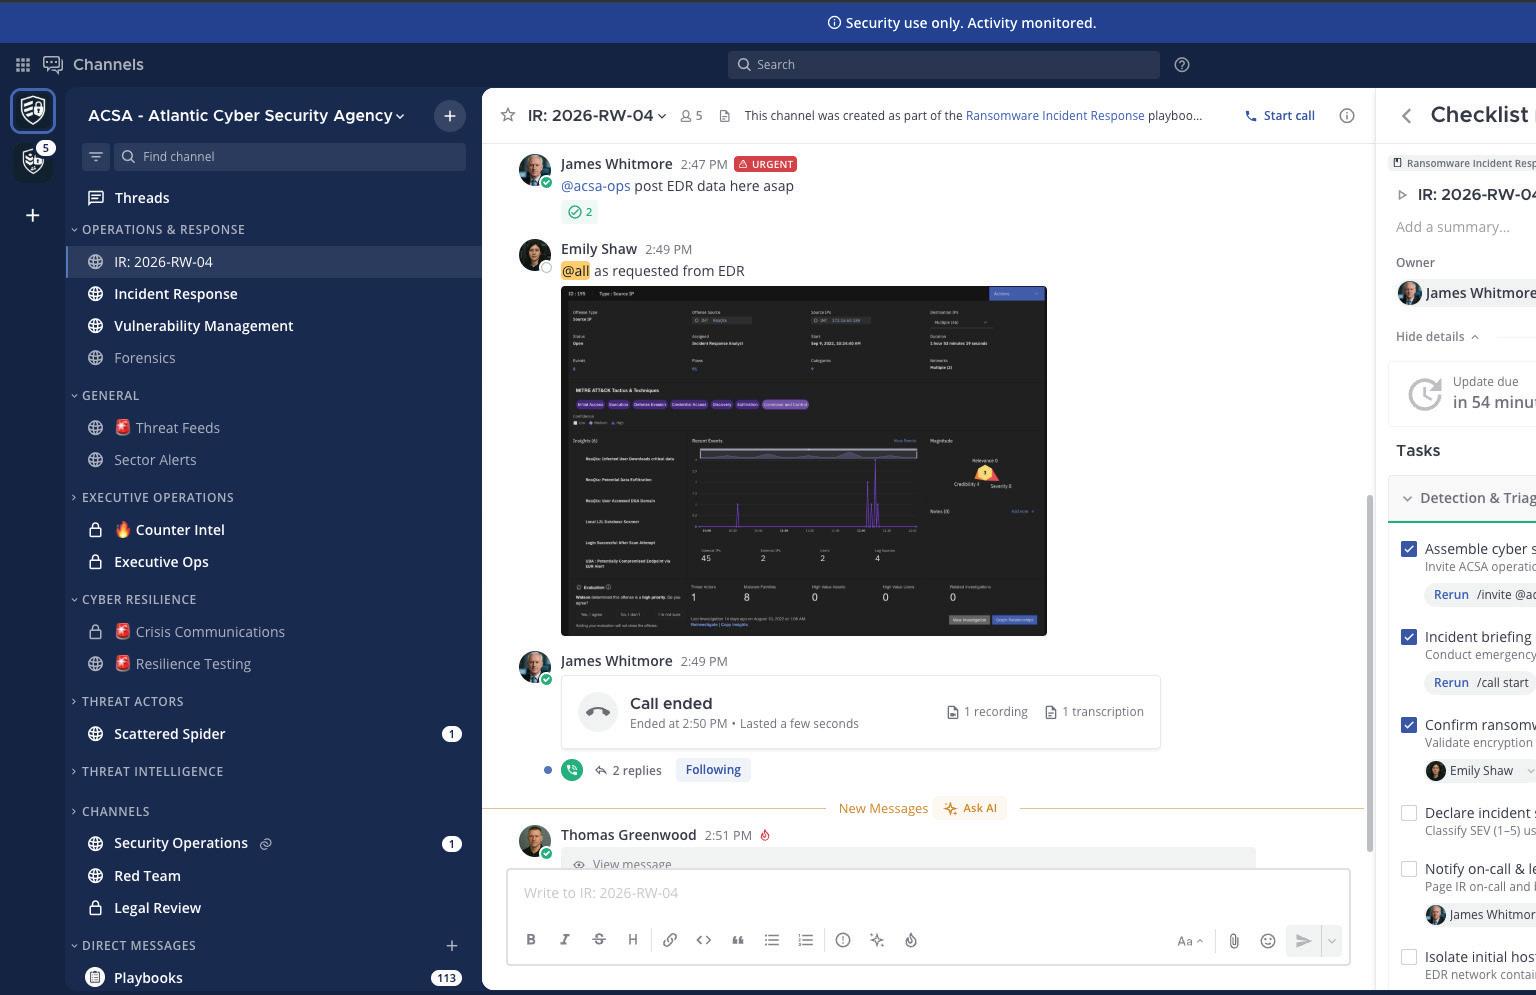
This is where digitisation of governance becomes important. When incident response frameworks are embedded directly into the collaboration environment, teams are able to move more decisively. They are not searching for guidance; they are executing it.
The platform, in this context, becomes more than a messaging layer. It becomes part of the operational control system that enables recovery.
Creating a blind spot
Cyber defence is often discussed in terms of visibility, how to detect, monitor, and respond to threats across complex environments.
But during an active incident, there is another requirement: the ability to operate without being seen.
By deploying an out-of-band environment on a separate network segment or within a secure private cloud, organisations can establish a coordination layer that is isolated from the compromised system.
“What you create is a blind spot for the attacker... they might see your main network, but they can’t see that coordinated response happening in the background.”
This separation restores a degree of control. While the primary environment may be disrupted or fully visible to an attacker, response efforts can continue elsewhere, securely, deliberately, and without interference.
Without that separation, every action risks being anticipated or countered. With it, organisations regain the ability to respond on their own terms.
The limits of convenience
In the absence of a prepared alternative, organisations tend to default to whatever is available. Increasingly, that means consumer messaging applications.
While these tools provide immediate connectivity, they introduce significant governance challenges. They are not designed for regulated environments, they lack auditability, and they provide little assurance over how information is handled or retained.
This creates a second-order risk. The organisation may manage the immediate incident, but struggle to account for its actions afterwards: what decisions were made, how they were made, and whether they met required standards.
Cyber incidents are no longer viewed purely as technical events. They are governance events, subject to scrutiny from regulators, boards, and stakeholders. In that context, informal communication channels are insufficient.
A simple test of readiness
“If your only plan is to use something like WhatsApp you are not meeting the boardlevel priority for secure governance.”
A credible approach requires more than a documented plan. It requires a hardened, segregated environment that is preconfigured, tested, and ready to activate without delay.
Resilience is an operational discipline
There is a tendency to treat resilience as something that can be added, like another capability layered onto existing systems.
In practice, resilience is an outcome of design. It reflects decisions about architecture, governance, and operational readiness made well before an incident occurs.
Out-of-band communication is a central part of that design. It ensures that when systems fail, coordination does not.
Because in a modern cyber incident, the critical question is not whether an organisation can still communicate. It is whether it can still coordinate, decide, and act without the attacker watching.
Resilience is an outcome of design. It reflects decisions about architecture, governance, and operational readiness made well before an incident occurs.
That is what ultimately defines resilience.
For many organisations, the gap is not awareness but execution.
A useful starting point is a simple question: if your primary communication systems were compromised tomorrow, how would your teams coordinate?
If the answer depends on improvisation, or on tools that fall outside governance and compliance frameworks, then resilience has not yet been achieved.
If you are reviewing your organisation’s cyber resilience or incident response readiness, visit mattermost.com to learn more or reach out to our team.
It’s Only Data.. Until It Isn’t
Why organisations must rethink their approach to data protection
By Irene Coyle, Data Protection Officer
Trust
Many organisations believe data protection is about policies, registers and regulatory compliance. In reality, it is about something far more fundamental: trust. When organisations mishandle personal data, the real damage is not just operational or financial – it is the loss of confidence from the people whose information they hold. But as a data governance specialist I believe data protection is not about documentation. It is about trust, leadership and understanding the real value of the data organisations hold.
There is one phrase I often use when explaining the importance of data protection to leadership teams:
“It’s only data... until it isn’t.”
From Policing to Data Governance
My perspective on data protection was shaped during a 30-year career with Police Scotland, where handling sensitive information was an everyday responsibility.
“We’ve Never had a Breach”
Data protection often suffers from an image problem.
For many organisations, it still feels like an administrative task – something to be documented, filed away and revisited only when a regulator asks questions.
Policies are written, registers are completed and GDPR compliance boxes are ticked. But this mindset fundamentally misunderstands the purpose of data protection.
It is not simply about compliance. It is about trust.
Over three decades working in policing and now as Chief Operating Officer at OSP Cyber Academy, I’ve seen how organisations approach sensitive information – and more importantly, how quickly the consequences appear when that information is mishandled.
Much of that work involved developing systems and processes designed to protect highly sensitive personal data. One initiative I was involved in was the creation of a vulnerable persons database – designed to support individuals who required additional protection and safeguarding.
Working with information of that nature quickly changes how you view data.
You realise that data is never just a record in a system. Behind every data entry is a real person – someone whose safety, privacy or wellbeing could be affected if that information is mishandled.
Later in my policing career, I was responsible for implementing GDPR across the recruitment function. It was a fascinating challenge because it highlighted how many organisations initially see data protection as a purely legal or administrative requirement. In reality, it is far more than that.
One of the most common questions organisations ask about data protection is also one of the most revealing:
“We’ve never had a breach – so why do we need to invest in this?”
At first glance, that may seem like a reasonable question. When nothing has gone wrong, data protection can feel abstract. It can appear procedural, even bureaucratic.
But data protection should never be about waiting for something to go wrong.
It is about understanding the value of the data your organisation holds.
Every organisation processes personal data – employee records, payroll information, customer data, contracts, supplier details and more. That information represents something incredibly important: trust.
And trust is something organisations build carefully over time but can lose very quickly.
It’s Only Data.. Until It Isn’t
Another common misconception is that organisations assume they are unlikely targets for cyber-attacks. But many breaches do not originate from direct attacks at all.
They come through third-party suppliers, partners or inherited systems.
So even if an organisation believes it is unlikely to be targeted, it must still consider the broader ecosystem surrounding its data.
Ultimately, data protection is about foresight. I always ask “If your systems were disrupted tomorrow, would you know which data matters most?” and “would your team know what to do in the first critical hour?”
Data Protection is Not Just GDPR paperwork
Another persistent myth is that data protection is primarily about documentation.
Policies, procedures and compliance frameworks are important. But documentation alone does not protect data. Data protection is fundamentally about how organisations think and behave when handling information.
The questions organisations should really be asking are practical ones:
• What data do we hold?
• Why do we hold it?
• Where is it stored?
• Who is responsible for it?
Many organisations proudly point to the policies they have in place with a big smile on their face. But policies that sit unread in folders or shared drives provide very little protection.
“Policies don’t protect data – people do.”
That is why structured training is so important. When staff understand how data flows through their organisation, how breaches occur and when to escalate concerns, the conversation moves from theory to practice.
Recognised training programmes –particularly those aligned with frameworks such as National Cyber Security Centre (NCSC) guidance – help organisations build real capability.
They help people recognise early warning signs of incidents, understand lawful data processing and embed accountability across the organisation.
Most importantly, they help leaders move beyond compliance towards competence.
The Real Risk isn’t the Fine
When organisations think about the consequences of data breaches, the discussion often centres on regulatory fines.
While financial penalties can be significant, they are rarely the most damaging outcome.
Reputation is. When personal data is mishandled, the message people hear is not about the size of a regulatory fine. The message they hear is much simpler:
“You didn’t protect me.”
That perception affects confidence from customers, employees and partners alike. Trust is therefore a leadership issue.
Data protection cannot be seen as solely the responsibility of the Data Protection Officer. That would be the equivalent of saying cyber security is solely the responsibility of the IT department.
Neither assumption is true.
Protecting data requires awareness and accountability across the entire organisation.
When Human Error Causes a Crisis
Many high-profile breaches are associated with sophisticated cyber-attacks. Yet some of the most damaging incidents arise from far simpler causes.
Human error remains one of the most common contributors to data breaches.
A recent example involved the inadvertent publication of personal information relating to approximately 9,400 police officers and staff in Northern Ireland. The data was mistakenly disclosed through a Freedom of Information response.
The incident was not malicious. But the consequences were severe.
Thousands of individuals were exposed, legal action followed and the PSNI faced intense public scrutiny.
It highlights an important reality: many breaches are not the result of malicious intent, but simple mistakes made by people who do not fully understand the risks.
The Importance of Knowing Where Your Data is
Understanding where organisational data resides is one of the most critical aspects of effective protection.
Without visibility, organisations cannot properly secure their information.
A well-known example illustrates this risk.
In 2018, Marriott International disclosed a breach affecting approximately 339 million guest records worldwide. The intrusion originated from a booking system belonging to Starwood Hotels – a company Marriott had acquired several years earlier.
Attackers had already gained access to the system before the acquisition and remained undetected.
When regulators investigated, the issue was not just the cyber intrusion itself. It was the due diligence surrounding the systems Marriott had inherited.
The organisation had not fully assessed the personal data stored within those systems.
The result was a regulatory fine of over £18 million and widespread reputational damage.
The lesson is simple:
“You cannot protect what you cannot see.” Data mapping is not merely administrative work. It is about gaining visibility of where risk exists within the organisation.
Without that visibility, organisations are effectively operating with blind spots.
And blind spots are where risk quietly grows.
Three Priorities for Leaders
For leaders trying to strengthen their organisation’s approach to data protection, the starting point does not need to be complicated.
In fact, it can be distilled into three priorities.
Clarity
Leaders must understand what data their organisation holds and how it flows across systems, departments and external partners.
Accountability
Responsibility for data must be clearly owned rather than assumed.
Culture
Many breaches arise from simple behavioural issues – an email sent to the wrong recipient, an incorrect spreadsheet attachment or access rights not removed when someone leaves the organisation.
These are not technology failures.
They are awareness failures.
When people understand why data matters, behaviour changes.
And when leadership supports structured training and governance, the organisation becomes both more competent and more confident in its data protection practices.
Preparation, Not Perfection
Data protection can feel overwhelming for organisations. But it should not be about achieving perfection. It should be about preparation.
Behind every data record is a person – a colleague, customer or member of the public. When that information is mishandled, what is damaged is not just data.
It is trust.
The reassuring reality is that many incidents are preventable through simple governance measures: visibility, accountability, training and leadership oversight.
When those elements are in place, good governance should actually feel uneventful.
And that is exactly how it should be. Because the real goal of effective data protection is not headlines. It is steady confidence.
After all: It’s only data.. until it isn’t.
Author:
Irene Coyle is Chief Operating Officer at OSP Cyber Academy and a cyber resilience and data protection specialist with over 30 years’ experience in policing, governance and organisational risk management. She works with leadership teams across public and private sectors to strengthen cyber resilience, data protection capability and practical governance.
To
listen to Irene Coyle interview with Scan Me
Control Through Access: Rethinking Cybersecurity in Emerging Technology Systems
Espionage draws value from access to confidential knowledge during research, design, and early development, when technologies remain inside controlled environments and knowledge remains concentrated among a relatively small group of actors.
Advanced technologies often take shape well before public deployment through a combination of technical choices, legal arrangements, investment structures, supply-chain design, and strategic decisions that influence their development, transfer, and use. I work inside that terrain, at the intersection of international business law, emerging technologies, and national security, with a focus on cross-border transactions, technology transfer, and export control.
Experience in space-related and advanced technology matters sharpened that perspective early, because strategic capabilities move across jurisdictions through legal structures long before they appear as finished systems. Cybersecurity therefore appears in my work as a structural issue. It is present in the way access is granted, in the way data flows are organised, and in the way trust is operationalised between actors who operate under different regulatory and geopolitical conditions. Law, capital, and technology meet at the point where access is defined, and that point carries enormous consequences for how exposure develops across the life of a system.
Access defines exposure from the outset. Legal and operational arrangements structure access to technological systems, define information exposure, and determine how that exposure develops through ongoing engagement. Partnerships, supply chains, investment structures, licensing terms, joint development arrangements, and procurement pathways all shape the access architecture around a system. Contracts sit at the center of that architecture because contracts distribute rights, responsibilities, interfaces, and permissions.
Cross-border collaborations make that dynamic especially important because each additional layer of operational integration can produce another layer of visibility. Early visibility influences capability development, market timing, procurement decisions, and competitive positioning. Advantage forms where knowledge is most concentrated, and timing strengthens that advantage as technology moves toward deployment.
Technical safeguards come afterward. By the time a technical control is installed, access may already have been widened through the design of the relationship itself. My work repeatedly returns to that point. Due diligence, in this context, functions as a security discipline in substance. It requires close attention to counterparties, ownership structures, technology pathways, data handling arrangements, export-control implications, and the operational meaning of proximity. Exposure follows the structure of access throughout the system lifecycle. Systems carry that exposure forward as they mature, scale, and connect to other systems.
Cybersecurity discourse often concentrates on attacks, breaches, and resilience. A significant part of my work focuses on risk mitigation and due diligence within legal and operational structures, where exposure is shaped through access configuration, technology transfer, supplychain integration, and information visibility, and where cyber espionage represents one of the most consequential manifestations of that structure. Espionage draws value from access to confidential knowledge during research, design, and early development, when technologies remain inside controlled environments and knowledge remains concentrated among a relatively small group of actors. Advanced research, proprietary technologies, trade secrets, internal communications, design parameters, and emerging capability roadmaps form the real terrain.
Visibility at that stage gives insight into direction. It reveals how systems are being built, how priorities are evolving, which capabilities are receiving investment, and where strategic intent is taking shape.
A further dimension appears when attention shifts from immediate-value information to information that retains significance across extended periods. Strategic communications, national securityrelated data, and confidential financial and strategic information that reflect how capital, resources, and capabilities are organised over time belong in that category. Investment portfolios and allocation strategies provide insight into how capital is positioned, where priority sectors are emerging, how future actions are structured, and which capabilities are expected to receive sustained backing. Financial positioning retains its relevance within this dynamic, as it reflects future decisions that unfold over time. Strategic communications carry a similar significance because they reveal how institutions frame decisions and sequence action. Value persists across time because the decisions embedded in such information unfold across time.
Time therefore becomes part of the exposure structure. Within cybersecurity and intelligence communities, the phrase “store now, decrypt later” captures a straightforward logic: encrypted information acquired in the present can retain strategic value as computational capability evolves. Data is preserved with the expectation that access conditions will change. Early access and future capability become linked through a single timeline.
Quantum computing defines that trajectory. Cryptographically relevant quantum computers influence the assumptions on which current encryption systems rely across financial systems, government communications, critical infrastructure, and many forms of protected data exchange. Contemporary cryptographic schemes rest on computational conditions that define what counts as secure in the present. Quantum capability changes those conditions. Protection therefore becomes a question of duration. Confidentiality depends on how long encryption remains effective as computational capability develops.
The sequence remains continuous: access takes place early, encryption preserves content under current conditions, and computational capability changes the duration of that protection.Cyber espionage and quantum cybersecurity operate across the same lifecycle, linking how access is structured with how protection holds over time. Post-quantum cryptography enters here as a planning and implementation priority, because the transition touches infrastructure, standards, procurement cycles, system inventories, and institutional capability. Quantum communication also matters within this landscape, since communication integrity and secure transmission remain central to trust across distributed systems. Quantum sensing broadens the picture further by bringing additional strategic implications into navigation, timing, detection, and broader operational environments.
As computational capability evolves, the conditions that sustain that protection evolve as well, which influences how previously collected encrypted data can be accessed over time. The structure of access and the evolution of capability therefore remain connected throughout the lifecycle of the system, and managing that connection requires attention to the frameworks that govern how technologies and data are controlled in practice. Legal and regulatory structures sit directly within this transition. They remain inseparable from how advanced technologies are accessed, transferred, and integrated into operational systems, and their effect becomes visible through the way access, control, and data movement are organised across those systems.
Contracts define who can access specific technologies and data, how that access is exercised, and under which operational conditions interactions take place, while data governance frameworks determine how information is stored, processed, and shared across interconnected environments.
Further, compliance requirements and export control regimes introduce jurisdictional constraints that regulate which actors may access particular capabilities and under what conditions, and technology transfer rules further shape how technical knowledge, software, and hardware move between entities and across borders. These layers operate together, and alignment between them determines whether access, control, and system behaviour remain coherent as technologies evolve.
Divergence across these layers creates inconsistencies in how access is implemented and enforced, and exposure develops within those inconsistencies, carrying forward into system
This structure becomes more complex in environments where the same underlying technologies are used across both civilian and security contexts. Civilian frameworks define access through regulatory requirements, accountability standards, and controlled deployment conditions, while security and defence applications follow strategic priorities linked to national interests and operational objectives. The same technology can therefore be subject to one set of access conditions in a regulated environment and a different set of conditions in a security-driven context, even though its technical properties remain unchanged. Governance operates across these conditions, shaped by how technologies are used in practice.
Questions of control, proportionality, and state interest arise at this intersection, shaping how access is granted, restricted, and exercised across jurisdictions and operational environments.
At this point “readiness” becomes the point where all of these threads converge. Technological change accelerates quickly. Institutional adaptation follows a longer timetable. My own work in this area has focused on narrowing that distance through initiatives designed to connect awareness, governance, capability development, and practical adoption. Since 2020, that effort has taken shape through the Quantum Technology Adoption Program and through platforms such as the Quantum Innovation Summit, where policymakers, regulators, researchers, cybersecurity actors, investors, and industry leaders can engage the same questions from different operational positions. Applied work matters because abstract awareness rarely shifts institutions on its own. Real readiness grows through foresight, governance, planning, and action. Maritime use cases, logistics challenges, and infrastructure applications show how the discussion moves from theory into implementation, where institutions can evaluate genuine operational value, identify bottlenecks, and prepare transitions in a way that reflects real conditions.
Trabelsi Leob Founder and President, Vernewell Group Inc.,
Emerging technologies reshape how systems are built, how information moves, and how control is exercised across digital environments. Cybersecurity evolves within that same movement, shaped by how institutions structure access and align with technological change as it unfolds. Staying ahead in this environment requires a structured approach. It begins with foresight, understanding where technological capability is heading and how it will influence existing systems. It requires governance, ensuring that development and deployment take place within frameworks that support trust and control. It depends on planning, translating that understanding into concrete strategies and operational pathways. It is completed through action, where those strategies are implemented and sustained. Institutions that move through this sequence early position themselves at the front of the curve. Institutions that move through this sequence early position themselves at the front of the curve and define how cybersecurity is applied within emerging technologies.
Interview with Malak Trabelsi Leob:
Malak
Dubai, UAE
HYBRID EVENT PLATFORM HYBRID EVENT PLATFORM
Bridging Science, Sovereignty, and Scale
Bridging Science, Sovereignty, and Scale
The global platform for quantum The global platform for quantum and emerging technologies and emerging technologies
Grand Hyatt Dubai Conference & Exhibition Centre, UAE 28-30 SEP 2026
Organized By Media Partner
From Shadow AI to Structured Governance:
How Enterprises Are Balancing Innovation and Risk
The Urgent Shift to AI Governance
Enterprises are moving from ad hoc AI usage to structured, risk-aware governance. This shift is essential because with every powerful new technology come both opportunities and challenges. The real focus is on how organizations can introduce and manage AI with proper controls—without killing innovation.
How AI Adoption Evolved from Ad Hoc to Structured
AI has been around for some time, particularly through machine learning, but its recent explosion has transformed how organizations operate and how people work and live. The COVID-19 pandemic accelerated this by forcing a shift from office-based to remote and hybrid workforces, creating tremendous pressure on enterprises to adapt quickly.
Initially, AI adoption was largely ad hoc. Different departments identified promising use cases—often through SaaS features or simple pilots—and implemented them without formal governance processes. This shadow AI mirrored the early days of digital transformation around 2014–2015, when organizations rushed to become web- and mobile-based for competitiveness and customer interaction. Big data and data science followed, but AI’s rapid spread created new complexities.
Big data and data science followed, but AI’s rapid spread created new complexities. Over the past year and a half, organizations have begun moving from shadow AI to formal governance.
This includes establishing clear AI usage policies, frameworks for responsible and ethical use of AI, high-level AI steering committees, and comprehensive AI inventories. These inventories help organizations stay on top of all AI use cases and track how they evolve.
Different organizations are at varying levels of maturity. Some have well-defined AI governance committees with clear criteria for acceptable and unacceptable use, while others are still catching up. In the UAE, government entities are setting a high bar by taking serious control over AI governance, recognizing the significant risks of uncontrolled deployment.
From Model-Centric to RiskCentric Governance
A key evolution is the shift from model-centric to risk-centric governance. In the model-centric approach, enterprises focused narrowly on the AI model itself and the specific use case— primarily its accuracy and business value. They often lacked a full picture of the overall risk the organization faced when deploying that system.
The risk-centric approach is more holistic and mature. It asks critical questions: Even if the model delivers good return on investment and measurable value, how much risk does it expose the organization to? This includes responsibility, ethics, respect for individual privacy, the nature of training data, and broader implications.
Higher-maturity organizations are adopting this perspective to address not just technical performance but also privacy, bias, and societal impact.
Embedding Governance by Design
Another major change is moving from bolt-on governance to embedded governance. In cybersecurity’s early days, security was often an afterthought— approached just before go-live as a simple checkbox. The industry matured to “secure by design,” involving security professionals from day zero.
AI governance is following the same journey. Mature organizations now speak of “ethical by design” or “responsible by design.” Governance teams get involved right from the start, even as models are being trained. They ensure data is responsibly sourced, does not violate privacy, and has proper approvals from data subjects. This embedding integrates AI governance into existing mechanisms such as project and change management, third-party risk, data governance, security, and privacy-by-design.
From Shadow AI to Structured Governance:
How Enterprises Are Balancing Innovation and Risk
The result is a more scalable process that supports rather than blocks business initiatives.
Achieving Visibility Through AI Inventory
Visibility is foundational to effective governance. Many organizations still lack a reliable map of where AI is being used, including capabilities hidden inside vendor tools.
Without a solid AI inventory, governance remains reactive.
Inventory is the number one critical factor in any governance initiative. Standards like ISO 27001, ISO 42001, and others all begin with asset management for good reason.
For AI, however, visibility is more complex than traditional IT systems. An AI system can draw data from dozens of sources, involve multiple training layers, and include intricate processes.
Many organizations are adopting a Configuration Management Database (CMDB) approach to AI— breaking systems down into layers and components, each with subelements, to ensure every part is secure, respects privacy, and meets ethical standards. This granular view enables better monitoring and control.
Clarifying Roles, Responsibilities, and Decision Rights
AI’s complexity also complicates roles and ownership. Traditional IT systems had clear business owners and system owners. With AI, ecosystemvernance bypasses as teams seek workarounds
Best practice is to break down roles and responsibilities with high granularity.
Some responsibilities may be shared, requiring primary and secondary owners. The AI Steering Committee provides high-level oversight.
Organizations that invest time in clearly documenting these elements build stronger, more effective AI governance frameworks.
Balancing Control with Innovation
Striking the right balance between control and innovation remains challenging. Too much control restricts experimentation and drives shadow AI. Too little exposes the enterprise to regulatory, ethical, security, and reputational risks.
The EU AI Act aims to achieve this balance by focusing on risk levels.
Principal Information Security Officer at the Ministry of Energy & Infrastructure
Vijay Velayutham
Use cases with minimal business impact can have lighter oversight, while those affecting individuals’ health, job performance, recruitment decisions, or societal outcomes require stricter controls, greater explainability, and accountability.
Tiered approaches—fast, lowfriction paths for low-risk uses and rigorous oversight for high-risk applications—help maintain agility while managing exposure.
The Growing Need for Technical Depth and Explainability
Technical depth is increasingly important. Governance bodies must address explainability, bias, adversarial risks, model drift, and robustness.
Explainability means the ability to trace an AI system’s decisions back to specific data inputs and criteria.
For instance, if AI scores job candidates or evaluates employee performance, the organization should later explain exactly why a particular score was assigned.
This technical area brings together machine learning, data privacy, programming, and governance. Governance committees and even boards will increasingly need members with technical understanding of AI. Without it, a gap emerges between governance expertise and technological reality. Future regulations may mandate such expertise at the highest levels.
Leadership and the Path Forward
As AI permeates every part of enterprise operations, leaders must deepen their understanding of its benefits and risks. Education is essential so executives can oversee how AI is used, controlled, and governed ethically while remaining aware of potential pitfalls.
The journey from shadow AI to structured, risk-aware governance is well underway. Organizations that embed responsible practices, maintain strong visibility, clarify roles, and balance innovation with control will be best positioned to harness AI’s advantages sustainably and ethically.
Effective AI governance is not about slowing progress. It is about enabling trustworthy, responsible advancement in the AI era.
About Vijay Velayutham:
Vijay Velayutham heads Governance, Risk Management and Compliance for the Ministry of Energy and Infrastructure in the UAE. Previously, he led the same function for the Smart Dubai platform and its Big Data platform. With 25 years in technology, including 19 years in cybersecurity spanning operations, security monitoring, incident response, and now risk management and governance, Vijay Velayutham has witnessed multiple waves of technological and cybersecurity change.
SCAN ME
Watch our exclusive pod cast Interview with Vijay Velayutham
THE CHAIN THAT BINDS US — AND THE COURAGE TO BREAK FREE
By The Rt Hon Stephen McPartland — Global thought leader in
cyber security, post-quantum cryptography and critical digital infrastructure
Supply chain cyber security sits at the epicentre of the geopolitical storm. But within the turbulence lies a journey every organisation can begin today — one that builds extraordinary competitive advantage with every step forward.
The global supply chain is no longer just a commercial construct — it is the central nervous system of our society, and it is under sustained, sophisticated attack.
State-sponsored threat actors, ransomware syndicates, and a new generation of AIaugmented adversaries are probing every node, every vendor, every unpatched firmware revision with a patience and precision that most organisations are wholly unprepared to meet. The geopolitical fractures — US-China decoupling, the continuing reverberations of Russia’s war in Ukraine, the scramble for rare earth dominance — have turned the supplier ecosystem into the most consequential battlefield of our era.
But here is where I diverge sharply from the prevailing commentary. Too many conversations about supply chain cyber security devolve into a catalogue of catastrophe, leaving organisations paralysed at the foot of what feels like an unscalable mountain. I want to change that framing entirely, because this is not a mountain to be conquered in one impossible leap. It is a path — one that organisations across Britain can begin walking right now, with the tools and knowledge they already have, building momentum and competitive strength with every stride they take.
The most important thing any organisation can do today is not the most sophisticated thing. It is the most foundational. Map your supply chain. Know who your critical suppliers are.
Understand what data they touch, what systems they connect to, and what your exposure looks like if they are compromised. This sounds deceptively simple — but the majority of organisations, including large and complex ones, cannot answer these questions with confidence.
That gap is not a failure. It is an opportunity. The moment you can answer those questions, you have moved meaningfully ahead of most of your peers. You have done something real. And that momentum matters enormously.
From that foundation, build outward. Introduce meaningful vendor security assessments — not questionnaire theatre, but genuine scrutiny of security postures, incident response capabilities, and software provenance. Establish contractual security baselines. Begin building your software bill of materials. Each of these steps, taken in sequence, does not feel like climbing a mountain. It feels like making tangible, measurable progress. Because it is. The organisations that have been on this journey for even twelve months will tell you the same thing: starting is the hardest part, and every step thereafter builds confidence as much as it builds capability.
AI: the game-changer that must be secured first
Here is where the opportunity becomes genuinely electric — and where I want to be unequivocal about something that is not yet receiving the attention it deserves. Artificial intelligence is transforming what is possible in supply chain cyber security. Predictive threat intelligence platforms are mapping third-party risk postures in real time. AIdriven continuous monitoring is replacing the annual audit ritual with live, dynamic visibility. Autonomous anomaly detection is surfacing compromise indicators that no human team could find at the speed and scale required. For organisations that have done the foundational work — that know their supply chain, that have baseline security controls in place — AI-powered tooling is now dramatically accelerating what was once a years-long maturity journey. The path is getting shorter and faster, and that is a genuinely thrilling development.
But I want to make a point that is equally important, and one that too many AI evangelists are glossing over. To truly harness AI as a business transformation tool — to embed it in your operations, your decision-making, your customer relationships, your supply chain — you must first secure it. An AI system that ingests your supplier data, your procurement intelligence, your operational telemetry, is only as trustworthy as the security architecture surrounding it.
Because it is extraordinary. Nation states are already harvesting encrypted data today with the explicit intention of decrypting it once quantum computers reach sufficient capability. The organisations that build their cyber-resilient supply chain foundation now, and then begin migrating toward quantum-resistant cryptographic standards as their maturity grows, will hold a structural security and competitive advantage that latecomers simply cannot replicate. Post-quantum readiness is not a second mountain. It is the natural summit of the path you are already walking. And the view from there — of a truly secure, AIempowered, quantum-safe British business landscape — is worth every step of the climb.
Smash through the fear
A compromised AI pipeline does not just leak data. It corrupts the very intelligence that your organisation is relying upon to make decisions. Adversaries who understand this — and the most capable ones absolutely do — are already targeting AI training data, model infrastructure, and the APIs that connect AI tools to businesscritical systems.
Genuine AI adoption and genuine cyber resilience are not parallel workstreams. They are the same workstream. Every business serious about unlocking AI-driven efficiency must treat securing its AI infrastructure as a prerequisite, not an afterthought. Get your supply chain cyber-secure, and you are not just protecting your business. You are building the trusted foundation upon which real AI transformation can safely stand.
The UK’s first-mover window
Britain sits at a genuinely enviable inflection point. We have world-class academic institutions, a financial services sector with arguably the most sophisticated operational resilience frameworks on earth, and the NCSC providing strategic depth that few allied nations can match. Our regulatory environment — shaped by the Product Security and Telecommunications Infrastructure Act and the forthcoming Cyber Security and Resilience Bill — is creating the scaffolding for a trusted digital economy.
Britain should not be waiting for that paradigm to arrive. Britain should be building it. The chain that currently binds us is not the threat landscape. It is not the geopolitics. It is our own hesitation. It is time to break free and step forward. And we have a cyber startup ecosystem that is punching well above its weight globally. The foundation is not merely solid. It is exceptional.
The geopolitical instability that generates so much boardroom anxiety is itself the argument for urgency rather than delay. Fragmented global supply chains create precisely the conditions in which trusted, cyber-resilient British suppliers become the preferred partners of multinational corporations and allied governments. Provenance, integrity, and demonstrable security posture are becoming procurement criteria of the first order. This is an export opportunity of extraordinary scale — and it is available to organisations that have taken exactly the kind of foundational steps I described earlier. Cyber-resilient growth is not a cost centre. It is a market differentiator, a brand asset, and an engine of genuine economic value creation.
The horizon: a quantum-safe future worth building toward
For those organisations that are already on this journey — that have their supply chain mapped, their AI infrastructure secured, their vendor risk programmes operational — I want to offer a glimpse of what the path ahead looks like.
What I cannot accept — and what this moment simply will not permit — is allowing a narrative of complexity and overwhelm to become the reason Britain hesitates. I see decision paralysis everywhere I travel: executives who know they need to act but are frozen by the fear of acting imperfectly. Let me be plain. An imperfect vendor risk programme that is live and operational is worth a hundred strategies that never leave the strategy document. A supply chain that is 70% mapped and actively being secured is transformatively better than one that is 0% mapped while awaiting a perfect solution. Progress compounds. Confidence builds. And in this technological revolution, the organisations that move — that innovate relentlessly, that treat each step forward as the foundation for the next — are the ones that will write the rules of the new global paradigm. www.linkedin.com/in/stephenmcpartland
Turning Global AI Regulation into a Game the World Can Understand
AI GOVERNANCE WORLD CUP
The world is entering a new era of artificial intelligence regulation. Across continents, governments are drafting laws, issuing guidance, and publishing frameworks to govern the design, development, and deployment of AI systems. Yet for all its importance, AI governance remains an abstract subject for most people. It is technical, legalistic, and often perceived as dry. The AI Governance World Cup was conceived as a response to that challenge: a way of turning global AI regulation into something understandable, comparative, and genuinely engaging.
What Is the AI Governance World Cup?
At its heart, the AI Governance World Cup is a structured comparison of national AI governance frameworks, presented in the format of a football tournament. Instead of watching two national teams compete on the pitch, audiences watch two regulatory systems compete across defined pillars: risk management, transparency, enforcement, scope, ethics, and innovation strategy.
Each “match” compares the strengths and weaknesses of two countries’ approaches to governing AI. The result is not determined by referees or VAR, but by informed community participation.
Why Football?
The idea rests on a simple observation. Football unites people. The FIFA World Cup is one of the most watched events in the world, drawing hundreds of millions of viewers and creating shared cultural moments that endure for decades.
People remember where they were when a famous goal was scored or when an underdog nation advanced further than expected. Regulation, by contrast, rarely inspires that kind of emotional engagement. The AI Governance World Cup seeks to borrow the structure and energy of sport and apply it to one of the defining policy debates of our time.
How it works
The format is straightforward. For each participating jurisdiction, a detailed governance report is prepared. These reports examine the architecture of a country’s AI framework:
whether it is legislative or guidance-based, whether it adopts a risk classification model, how it defines high- risk systems, which actors are regulated, and what enforcement mechanisms are available. Technical thresholds, such as compute limits used to define systemic models, may also be considered. The aim is not to oversimplify, but to distil complex regulatory ecosystems into comparable components. To ensure fairness, each match is assessed against consistent criteria.
These pillars might include the robustness of risk classification, clarity of obligations, transparency requirements, cybersecurity safeguards, institutional oversight, and balance between innovation and precaution. By using the same metrics across jurisdictions, the comparison becomes structured rather than rhetorical. It allows observers to see not only which country has legislated, but how it has legislated and where its priorities lie.
Once the comparative analysis is presented, the audience becomes part of the process. Voting can take place at conferences, online, or through social media platforms. In some formats, participants vote pillar by pillar, awarding points for each dimension
From KYC to KYAI: Know Your AI
A recurring theme in AI governance discussions is the need for organisations to “know their AI.” Borrowing from financial regulation’s “Know Your Customer” principle, the concept emphasises understanding what systems are in use, what data they process, and what risks they pose. The AI Governance World Cup reinforces this mindset.
By examining how different countries classify and manage risk, participants gain clarity on their own responsibilities. Governance becomes less about abstract compliance and more about operational awareness.There is also a geopolitical dimension. Regulatory frameworks are not merely protective mechanisms; they are instruments of influence. The so-called “Brussels Effect” demonstrated how European data protection rules shaped global practice. AI governance may follow a similar trajectory. Countries that establish credible, coherent frameworks may set de facto standards beyond their borders. The World Cup format makes this competitive dynamic explicit. It frames AI regulation as part of a broader contest over norms, trust, and technological leadership.
AI Governance Performs on a Global Stage
Critically, the initiative recognises that public memory shapes policy discourse. Iconic sporting moments endure because they combine narrative, emotion, and shared experience. Regulation rarely achieves that combination. By aligning AI governance debates with the structure of a tournament, the World Cup creates reference points. Participants may recall that one country “advanced” due to stronger risk controls, or that another fell short on enforcement clarity. These associations anchor complex policy discussions in memorable narratives.
None of this diminishes the seriousness of AI governance. On the contrary, it underscores its importance. Artificial intelligence is increasingly embedded in healthcare, finance, public services, and critical infrastructure
Decisions about how to regulate these systems will shape innovation trajectories, market access, and public trust for decades. The AI Governance World Cup offers a way to democratise that conversation without diluting its substance.
A Pivotal Moment for AI Governance
Ultimately, the value of the AI Governance World Cup lies in its ability to bridge two worlds: the technical realm of policy design and the cultural realm of shared experience. It recognises that engagement is not a luxury but a necessity. If regulation remains confined to specialist circles, its legitimacy may suffer. If it becomes part of a broader, participatory dialogue, it stands a better chance of being understood and respected.
As the global AI landscape continues to evolve, so too will the frameworks that govern it. Comparisons will intensify. Debates will sharpen. The AI Governance World Cup does not claim to resolve these tensions. Instead, it provides a platform for exploring them in a structured and accessible way. In doing so, it transforms AI governance from a background technicality into a visible, collective endeavour. In a world where millions gather to watch a ball cross a line, perhaps it is not unreasonable to gather, too, to consider how algorithms cross borders. The stakes, after all, are just as high.
Turning Global AI Regulation into a Game the World Can Understand
Ai governance world cup
The world is entering a new era of artificial intelligence regulation. Across continents, governments are drafting laws, issuing guidance, and publishing frameworks to govern the design, development, and deployment of AI systems. Yet for all its importance, AI governance remains an abstract subject for most people. It is technical, legalistic, and often perceived as dry. The AI Governance World Cup was conceived as a response to that challenge: a way of turning global AI regulation into something understandable, comparative, and genuinely engaging.
What Is the AI Governance World Cup?
At its heart, the AI Governance World Cup is a structured comparison of national AI governance frameworks, presented in the format of a football tournament. Instead of watching two national teams compete on the pitch, audiences watch two regulatory systems compete across defined pillars: risk management, transparency, enforcement, scope, ethics, and innovation strategy.
Each “match” compares the strengths and weaknesses of two countries’ approaches to governing AI. The result is not determined by referees or VAR, but by informed community participation.
Why Football?
The idea rests on a simple observation. Football unites people.
The FIFA World Cup is one of the most watched events in the world, drawing hundreds of millions of viewers and creating shared cultural moments that endure for decades. People remember where they were when a famous goal was scored or when an underdog nation advanced further than expected. Regulation, by contrast, rarely inspires that kind of emotional engagement. The AI Governance World Cup seeks to borrow the structure and energy of sport and apply it to one of the defining policy debates of our time.
How it works
The format is straightforward. For each participating jurisdiction, a detailed governance report is prepared. These reports examine the architecture of a country’s AI framework: whether it is legislative or guidance-based, whether it adopts a risk classification model, how it defines high- risk systems, which actors are regulated, and what enforcement mechanisms are available.
Technical thresholds, such as compute limits used to define systemic models, may also be considered. The aim is not to oversimplify, but to distil complex regulatory ecosystems into comparable components. To ensure fairness, each match is assessed against consistent criteria. These pillars might include the robustness of risk classification, clarity of obligations, transparency requirements, cybersecurity safeguards, institutional oversight, and balance between innovation and precaution.
By using the same metrics across jurisdictions, the comparison becomes structured rather than rhetorical. It allows observers to see not only which country has legislated, but how it has legislated and where its priorities lie.
Once the comparative analysis is presented, the audience becomes part of the process. Voting can take place at conferences, online, or through social media platforms. In some formats, participants vote pillar by pillar, awarding points for each dimension of governance.
In others, an overall winner is selected based on the aggregate strength of the framework. The essential principle remains the same: the community is invited to weigh evidence and form a view parallel. This creates narrative symmetry and helps anchor the discussion in a broader cultural moment.
Even where football scheduling does not dictate the pairing, comparisons can be designed to spark meaningful debate— European Union versus United States, for instance, or Singapore versus Canada. The structure is flexible, but the comparative discipline remains constant.
Contrasting Ai Governance Philosophies
One of the most illuminating aspects of the AI Governance World Cup is the way it exposes differences in regulatory philosophy.