
Passwords were initially created for a very basic digital environment.
At present, it is estimated that users have at least a dozen accounts with their work, shopping, banking, and entertainment platforms, among others. So, it’s almost impossible for users to remember the credentials of all the services they use. That’s why password reuse is very common.
Using password-only authentication has these implications:
Increased threat of credential theft
Often password change requests
Onboarding difficulties
Susceptibility to phishing attacks
User dissatisfaction with cross-device experiences
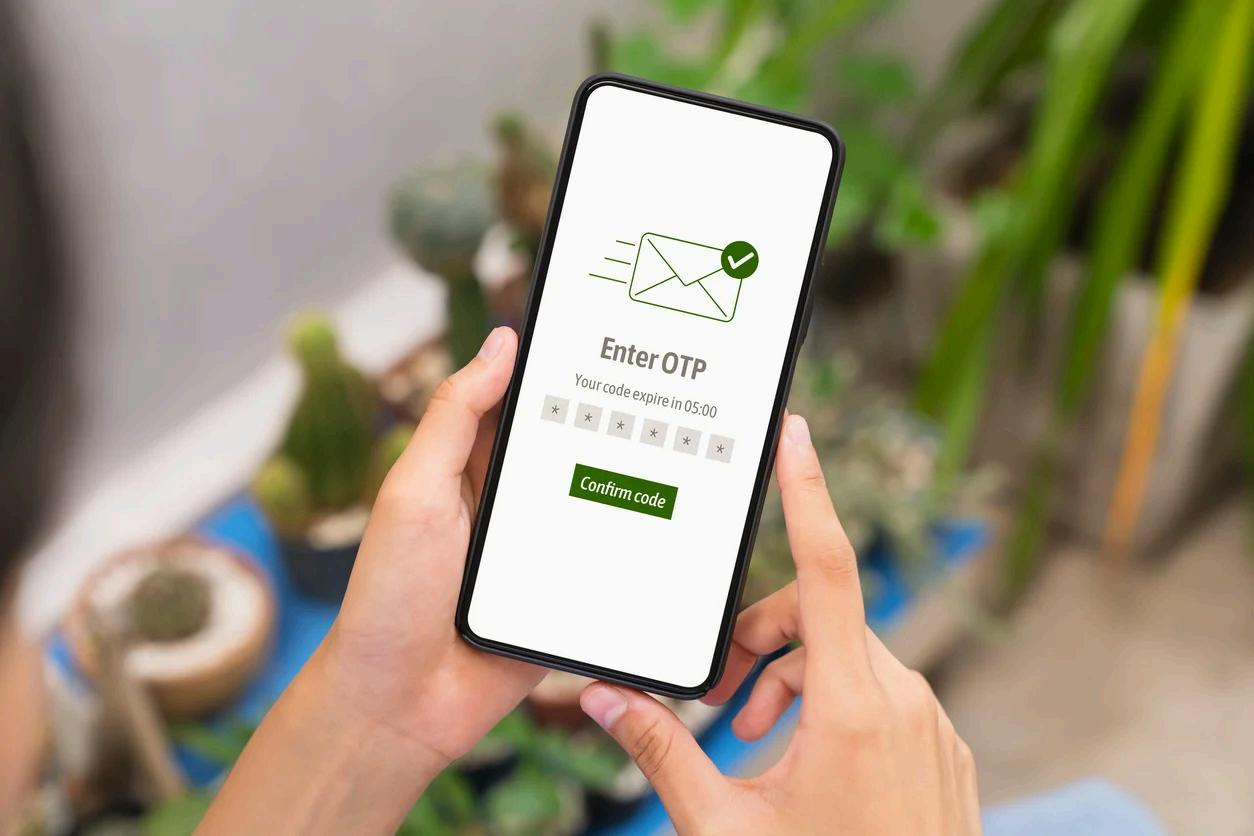
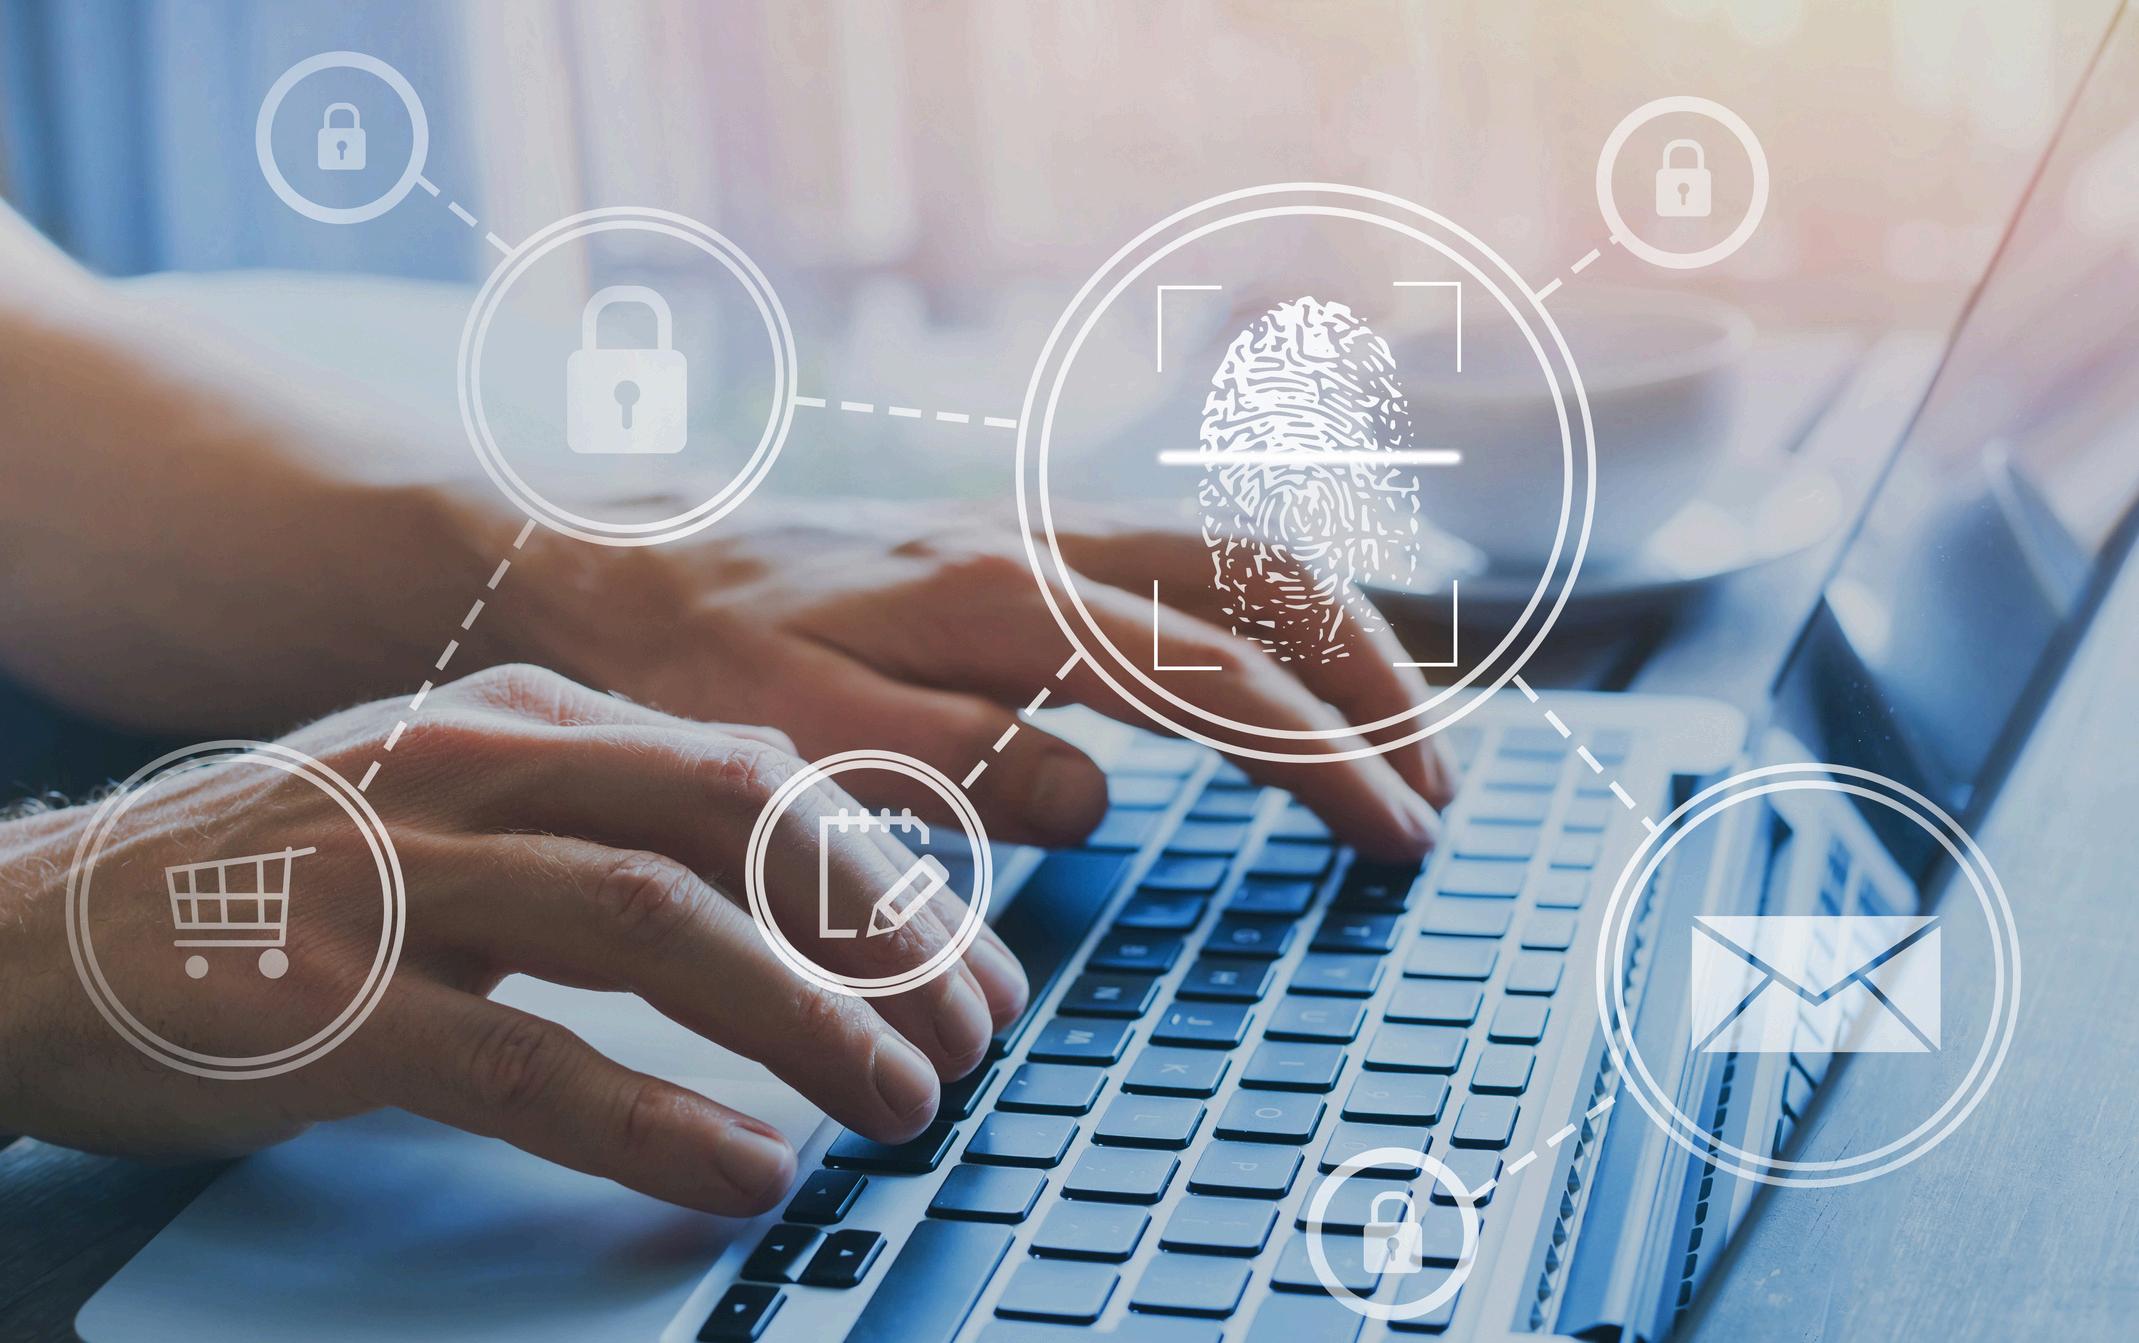
For this reason, many businesses are moving towards passwordless authentication techniques. Instead of requiring users to come up with passwords and remember them, authentication could be done based on a user having a verified phone number, email address, or other factors of identity that are trusted. This not only enhances security but also makes it more user-friendly.
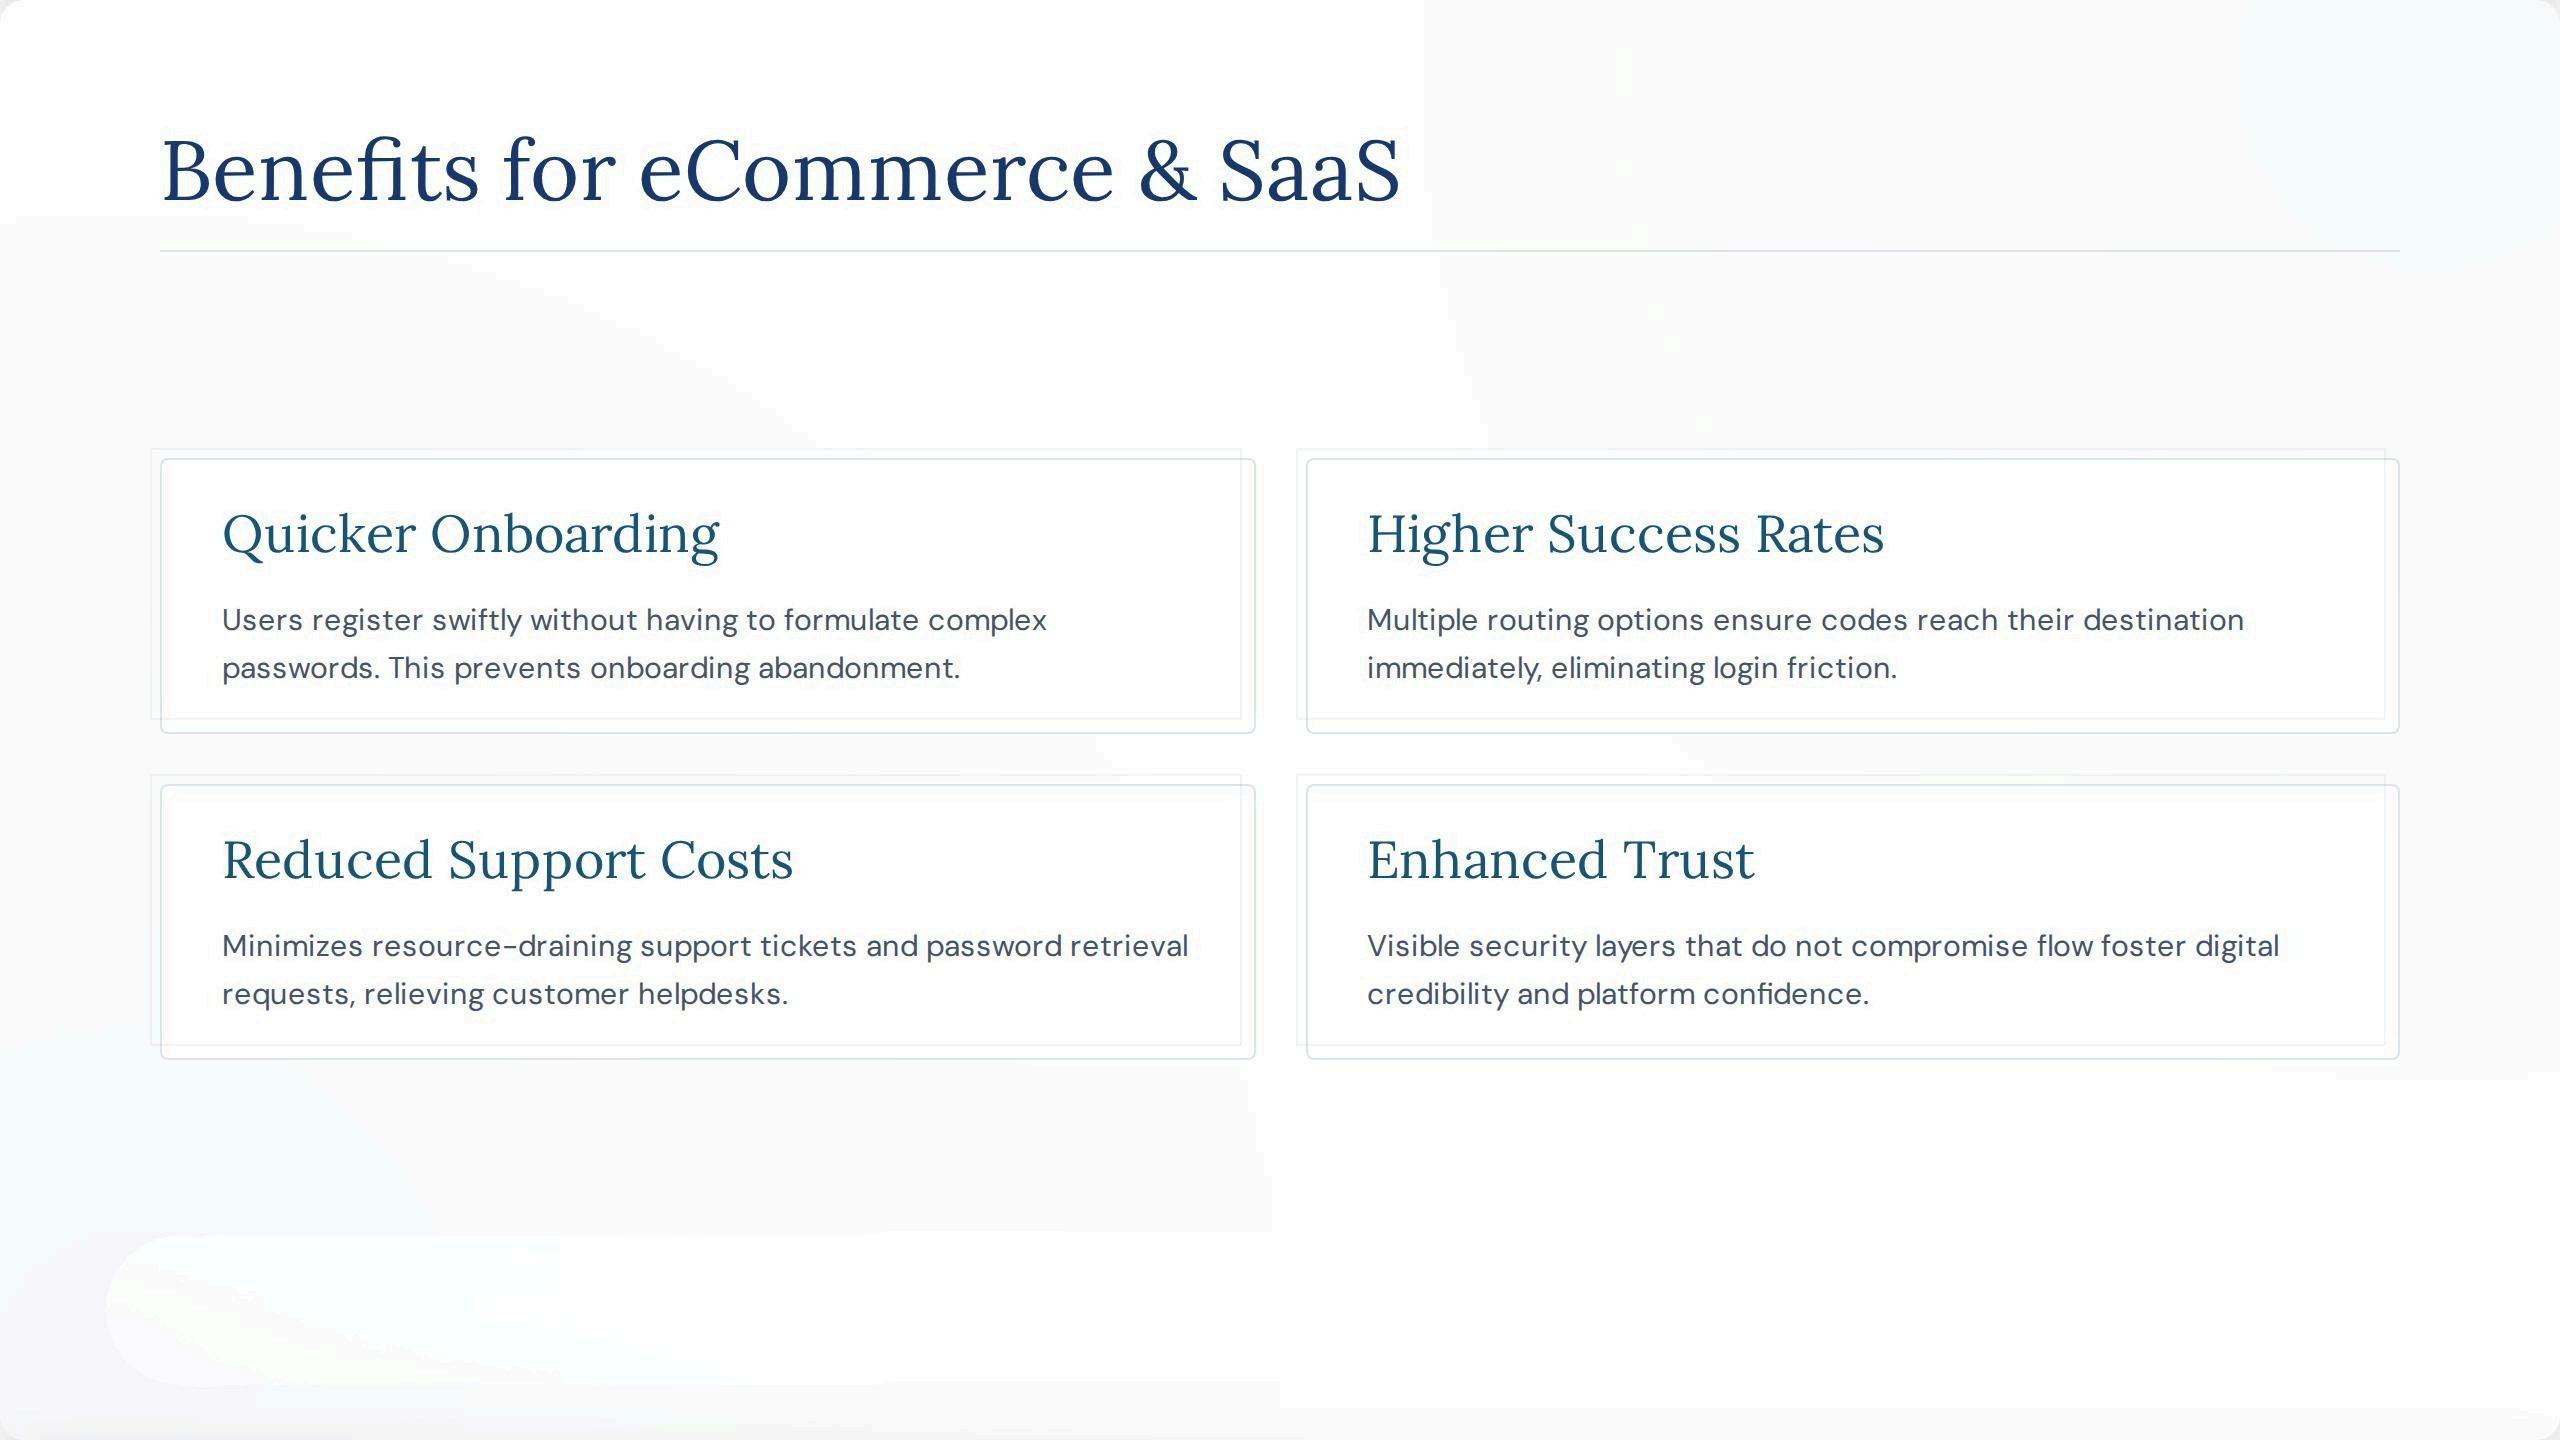
Besides the security benefits, the desire for a better experience is also motivating users to prefer passwordless authentication. Quick access frequently means quite a bit higher onboarding success and better product use.
www.authyo.io support@authyo.io